What Is CMMC Compliance? Requirements, Levels and the Certification Process
Published on
February 26, 2026
/
updated on
October 6, 2026
How to read the CMMC level off your contract, what the 3 levels require, how certification works, and what falls due each year.
You meet CMMC compliance requirements by protecting the government information your contract puts on your systems, to the standard that contract names, and proving it where a contracting officer checks. When CMMC language arrives in a contract or a flowdown from a prime in the defense supply chain, the first two questions are always the same: what is CMMC compliance, and which level does this contract point to?
Status in September 2026. On 13 July 2026 the Department of War suspended the move to Phase 2 (2), and a DFARS class deviation now binds contracting officers to that suspension (15). The rule is unamended, and Phase 1 self-assessments stay in force (2, 3).
What is CMMC compliance?
CMMC compliance means meeting the security requirements the Department of Defense (DoD) attaches to your contract, at the level the contract names, and proving it through an assessment. The rule's own CMMC compliance definition is narrower than the phrase suggests: the Cybersecurity Maturity Model Certification (CMMC) program is designed to ensure defense contractors are "properly safeguarding" federal contract information (FCI) and controlled unclassified information (CUI) on their own systems (3).
- Why it exists. Contractors already had to protect this information under DFARS 252.204-7012 and FAR 52.204-21. CMMC "does not alter" those requirements; it "provides a means of verifying implementation" of them (3).
- Where its requirements come from. The CMMC standard writes no controls of its own; it works from existing standards: FAR 52.204-21 and two publications of the National Institute of Standards and Technology (NIST), SP 800-171 and SP 800-172 (3). Most of the work is implementing cybersecurity standards that predate CMMC.
- What "CMMC 2.0" means. DoD announced the current program as "CMMC 2.0" in November 2021, replacing the five levels of CMMC 1.0 with three (17).
Compare CMMC with NIST SP 800-171. The relationship between CMMC and NIST SP 800-171 sets out how the two fit together and which NIST revision Level 2 binds.
Which companies need CMMC compliance?
CMMC applies to DoD contractors and subcontractors, at any tier, whose contract puts FCI or CUI on their own information systems (3). Membership of the defense industrial base comes from your government contracts and the information they involve, not from your company's size.
The two DFARS clauses that bring CMMC into your contract
DoD CMMC requirements reach you through two pieces of contract language.
- DFARS 252.204-7021 puts the obligation into DoD contracts (4).
- DFARS 252.204-7025 sits in the solicitation, names the level and makes a current CMMC status a condition of award (5).
A contracting officer "shall check SPRS and not award" without a current status at the required level, and the same check applies before an option or an extension (1). SPRS is the Supplier Performance Risk System, where government contractors post their status. Two buys are outside CMMC: those made only for commercially available off-the-shelf items, and Federal information systems you run on the Government's behalf (3).
FCI or CUI: the type of information decides your level
The program manager selects the CMMC status "based upon the type of information, FCI or CUI" your systems will handle in the work (3).
- Federal contract information (FCI) is information "not intended for public release, that is provided by or generated for the Government under a contract to develop or deliver a product or service to the Government" (4).
- Controlled unclassified information (CUI) is information that a law, regulation or Government-wide policy requires to be handled with safeguarding or dissemination controls (4).
Both are sensitive information the Government controls. If you handle federal contract information only, a Level 1 self-assessment is required; if you do not handle controlled unclassified information at all, no independent assessment is needed (6). Figure 1 shows the path from the information to the level.
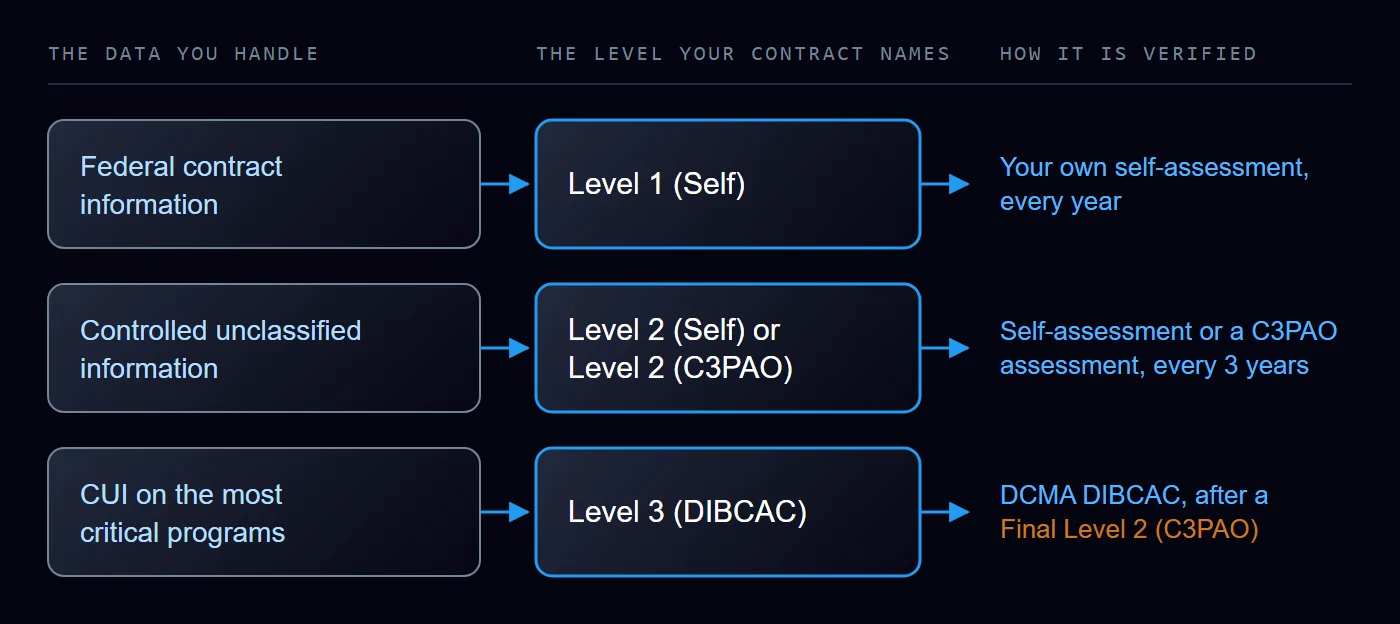
Adapted from: 32 CFR 170.15 to 170.18 (3).
How to tell whether you handle CUI
Check four places before you decide that you hold no CUI.
- Markings. CUI carries a banner marking, "CONTROLLED" or "CUI" (18).
- The contract. Covered defense information includes information "marked or otherwise identified in the contract" (12).
- What you produce. It also includes information "collected, developed, received, transmitted, used, or stored by or on behalf of the contractor in support of the performance of the contract" (12), so drawings or test data you create can count unmarked.
- The CUI Registry. It lists every approved CUI category and its markings (18).
CMMC flowdown to subcontractors
CMMC flows down from prime contractors to subcontractors "throughout the supply chain at all tiers" that handle FCI or CUI (3). A subcontractor handling only FCI needs Level 1 (Self); one handling CUI needs at least Level 2 (Self), and Level 2 (C3PAO) under a prime at Level 2 (C3PAO) or Level 3 (3). Each subcontractor affirms compliance before award and annually (4).
CMMC levels explained: Level 1, Level 2 and Level 3
CMMC has three levels, and the type of information in the contract decides which one applies (3). Many guides still call them Foundational, Advanced and Expert, the names used when CMMC 2.0 was announced (17); the rule numbers them and names none (3). A C3PAO is a CMMC Third-Party Assessment Organization, an accredited firm that performs Level 2 certification assessments; DIBCAC is the Defense Contract Management Agency team that performs Level 3 assessments (3, 4).
Level 1: basic safeguarding of federal contract information
Level 1 is for contractors that handle FCI but no CUI. Its 15 requirements are the basic safeguards of FAR 52.204-21(b)(1): limit system access to authorized users, identify and authenticate them, sanitize media before disposal, control physical access and visitors, protect system boundaries, correct flaws promptly and keep malware protection current (3, 22). You self-assess every year, enter the result in SPRS and affirm annually. No POA&M is allowed, so all 15 must be met (3).
Level 2: broad protection of controlled unclassified information
Level 2 is for contractors that handle CUI. Its 110 requirements are those of NIST SP 800-171 Revision 2 in 14 domains, including multifactor authentication, FIPS-validated cryptography for CUI, audit logs traced to individual users and an incident-handling capability (3, 16). The contract names a self-assessment or a C3PAO certification assessment, repeated every three years, with an annual affirmation (3). A Conditional status is possible when your score divided by the 110 requirements is 0.8 or higher, with the POA&M closed within 180 days (3).
Level 3: enhanced protection of CUI on critical programs
Level 3 is for CUI "associated with a critical program or high value asset" (23). It adds 24 requirements from NIST SP 800-172 to the 110 (3), among them:
- a security operations center that operates 24/7;
- an incident response team deployable within 24 hours;
- penetration testing at least annually;
- threat hunting and a supply chain risk plan.
A Final Level 2 (C3PAO) on the same scope comes first; DCMA DIBCAC then assesses every three years, and a cloud provider does not remove the 24 requirements (3).
The three CMMC levels side by side
Table 1 compares the three levels on what you implement, how you are assessed and what you keep up.
Table 1. The three CMMC levels: requirements, assessment and what you keep up.
| Level | For | Requirements | Assessment | POA&M allowed | Status current for |
|---|---|---|---|---|---|
| Level 1 | FCI | 15 at 48 CFR 52.204-21(b)(1) (3) | Self-assessment every year (3) | No (3) | 1 year (4) |
| Level 2 | CUI | 110 of NIST SP 800-171 Rev. 2 (3, 6) | Self-assessment or C3PAO, every three years (3) | Yes, closed within 180 days (3) | 3 years (4) |
| Level 3 | CUI on the most critical programs (3) | Level 2 plus 24 from NIST SP 800-172 (3, 6) | DCMA DIBCAC, every three years (3) | Yes, closed within 180 days (3) | 3 years (4) |
Sources: as numbered in each row. Every level adds an affirmation at each assessment and annually (3). While the Phase 2 suspension lasts, only Level 1 (Self) and Level 2 (Self) may be designated (7).
What decides Level 2 (Self) or Level 2 (C3PAO)
The program manager or requiring activity chooses per procurement, weighing (3):
- the criticality of the mission capability;
- the type of acquisition program or technology;
- the threat of loss of the information;
- the impact if security deficiencies are exploited.
So you can hold Level 1 for one contract and need Level 2 for another. A higher status covers the lower ones on the same scope (3). Levels 2 and 3 end in a Conditional or a Final status and Level 1 in a Final status only: seven statuses in all (4).
Take the levels one at a time. A per-level walkthrough is in the three CMMC levels in detail.
CMMC requirements: the 14 domains and what each requirement asks
CMMC security requirements at Level 2 are the 110 requirements of NIST SP 800-171 Revision 2, grouped in 14 domains (3, 16). The rule incorporates Revision 2 although NIST superseded it with Revision 3 in May 2024 (9), and the Department will move to Revision 3 only "with future rulemaking" (6).
The 14 CMMC domains at Level 2
Each domain is a NIST requirement family, and its two-letter code starts every requirement identifier, as in AC.L2-3.1.1 (3). What each one requires, with its number of requirements (16):
- Access Control (AC), 22: who may use systems and what they may do, CUI flow, remote and wireless access.
- Awareness and Training (AT), 3: security awareness, role training and insider-threat awareness.
- Audit and Accountability (AU), 9: audit logs traced to individual users, reviewed and protected.
- Configuration Management (CM), 9: baselines, inventories, security settings and change control.
- Identification and Authentication (IA), 11: user and device identity, multifactor authentication, password rules.
- Incident Response (IR), 3: an incident-handling capability, reporting and testing.
- Maintenance (MA), 6: controlled maintenance, off-site sanitization, multifactor authentication for remote maintenance.
- Media Protection (MP), 9: marking, protecting, encrypting and sanitizing media with CUI.
- Personnel Security (PS), 2: screening before access and protection at terminations and transfers.
- Physical Protection (PE), 6: physical access, visitors, access logs and alternate work sites.
- Risk Assessment (RA), 3: periodic risk assessment, vulnerability scanning and remediation.
- Security Assessment (CA), 4: control assessments, plans of action, monitoring and the system security plan.
- System and Communications Protection (SC), 16: boundary protection, deny-by-default networking, FIPS-validated encryption of CUI.
- System and Information Integrity (SI), 7: flaw remediation, malware protection, alerts and attack monitoring.
Check the controls list by level. Every requirement, domain by domain, is in the CMMC controls list by level.
What a single CMMC requirement is made of
Each requirement has a statement, assessment objectives and evidence, and the assessor scores the objectives (8). A requirement is MET only when every objective is satisfied on final evidence; drafts and unapproved policies are not accepted, and one NOT MET objective fails the requirement (3, 8).
Evidence covers your policies and processes as well as your CMMC practices. Most objectives require testing, because testing "demonstrates what has or has not been done" (8). Take CA.L2-3.12.3, "Monitor security controls on an ongoing basis" (8):
- the assessor examines the security plan and the records of its reviews;
- interviews the people responsible for it;
- tests the monitoring itself.
CMMC timeline in 2026: where the program stands after the Phase 2 suspension
CMMC is in force, but its next phase has been on hold since 13 July 2026. CMMC implementation was to run in four phases a year apart (3).
Table 2. The CMMC timeline.
| Date | What happened |
|---|---|
| 15 October 2024 | The CMMC Program rule, 32 CFR part 170, was published (10) |
| 16 December 2024 | The rule took effect (10) |
| 10 November 2025 | Phase 1: the DFARS rule took effect and CMMC entered contracts through DFARS 252.204-7021 (6, 11) |
| 13 July 2026 | The Department of War suspended the move to Phase 2 and ordered a 60-day review (2) |
| 10 November 2026 | Planned start of Phase 2, Level 2 (C3PAO) as a condition of award; suspended (2, 3) |
| 10 November 2028 | The CMMC clause goes into every contract where FCI or CUI will be on contractor systems (15) |
Sources: as numbered in each row.
What the suspension changed, and what still applies
- Designation. Program managers "must only include the need for CMMC Level 1 (Self) or Level 2 (Self) assessments" (7).
- Existing contracts. Solicitations are amended and contracts lose the certification requirements at the next option or administrative modification (7). Class Deviation 2026-O0025 directs contracting officers to "remove or revise the Cybersecurity Maturity Model Certification (CMMC) requirements in new and existing solicitations and contracts" (15).
- Still required. "All Phase I self-assessment requirements remain firmly in place" (2), and DFARS 252.204-7012 still applies: protect covered defense information with NIST SP 800-171 and report cyber incidents within 72 hours (7, 12).
- The rule. A class deviation is not rulemaking; 32 CFR part 170 is unamended (3). The CMMC Reform Task Force review has produced no published guidance as of September 2026 (2).
Trace what changed between CMMC 1.0 and 2.0. The change history is in what changed between CMMC 1.0 and 2.0.
How to get CMMC certification: 8 steps
To get CMMC certification you confirm your level, prepare the environment, get assessed on your level's route and post the result in SPRS.
Step 1: Confirm the level your contract requires
Read the level in the DFARS 252.204-7025 provision of the solicitation, or ask the prime what it flows down (3, 5). The level and its route decide every later step.
Step 2: Define your assessment scope
The scope "must be specified prior to assessment" and is the set of assets that will be assessed (3). It drives the effort and the cost of everything after it; the scope section below explains how it is drawn.
Step 3: Run a gap assessment
Assess every requirement of your level against your environment with the objectives the assessor will use (8), so the identified gaps are known before an assessor finds them.
Step 4: Implement the missing requirements
Close the gaps. A requirement that is not implemented is NOT MET whatever the plan says: a POA&M is "not a substitute for a completed requirement" (3).
Step 5: Write or update the system security plan
The system security plan (SSP) describes your boundary and how each requirement is met. Without a current one, the assessment "could not be completed due to incomplete information and noncompliance with 48 CFR 252.204-7012" (3).
Step 6: Put remaining gaps on a POA&M, where allowed
A POA&M is never allowed at Level 1. At Level 2 the score must reach 0.8 of the 110 requirements, no item may be worth more than 1 point (except non-FIPS-validated CUI encryption), and six requirements never qualify, among them the SSP and three physical access controls (3, 6).
Step 7: Choose a C3PAO and get assessed
Level 1 and Level 2 (Self) are self-assessments entered in SPRS; Level 2 (C3PAO) is performed by a C3PAO and entered through eMASS; Level 3 is performed by DCMA DIBCAC (3). C3PAOs are authorized and accredited by the CMMC Accreditation Body (3), currently the Cyber AB, which runs a marketplace of certified assessors (6). CMMC assessments examine documents, interview staff and test systems (8).
Step 8: Record the result in SPRS and affirm it
SPRS issues a CMMC unique identifier for each system assessed (4). The Affirming Official, "the senior level representative" of the organization, then affirms compliance at the assessment and annually (3). A Final status records full compliance on the scope; a Conditional status must have its POA&M closed within 180 days (3). Conditional is enough for award at Levels 2 and 3, not at Level 1 (1).
Walk through an assessment end to end. What happens during it is in how a CMMC assessment runs.
The CMMC process inside your company: scope and enclaves
Scope decides how much of your company the CMMC requirements reach: the requirements that protect CUI apply inside the boundary you draw (3). At Level 1 the scope is the systems that handle FCI; at Level 2 it is built from five asset categories (3).
CMMC asset categories at Level 2
Every asset in your environment falls into one of five categories, and each is assessed differently (3).
Table 3. CMMC Level 2 asset categories.
| Category | What it is | How it is assessed |
|---|---|---|
| CUI assets | Process, store or transmit CUI | Against all Level 2 requirements |
| Security Protection Assets | Provide security functions to the scope | Against the requirements relevant to what they provide |
| Contractor Risk Managed Assets | Can, but are not intended to, handle CUI | SSP review, a limited check if questions arise |
| Specialized Assets | IoT, operational technology, government equipment, test equipment | SSP review only |
| Out-of-Scope Assets | Cannot handle CUI and protect no CUI asset | Not assessed; the exclusion must be justified |
Source: 32 CFR 170.19(c), table 3 (3). Every in-scope asset goes in the asset inventory, the SSP and the network diagram.
Enterprise or enclave: where CUI is allowed to live
- The whole enterprise. CUI moves through your ordinary network, and the scope covers it all.
- An enclave. CUI stays in a logically separated segment; sending properly encrypted CUI out of it "does not incur an extension of the CMMC Assessment Scope to include the enterprise networking components" (6).
Two things break an enclave. Encryption alone "does not, by itself, prevent data transfer or enforce the security boundary of a network" (6). And a virtual desktop endpoint stays out of scope only if every one of these holds (6):
- the session blocks copying, file transfer and printing;
- it carries only video, keyboard and mouse data;
- it sits behind multifactor authentication to the virtual desktop server.
Is this tool CMMC compliant? How to judge a vendor before you buy
No product is CMMC compliant on its own: an organization holds a CMMC status, and a tool only helps or hinders its evidence. Check these before you sign.
- The requirements it helps satisfy, by identifier. A vendor that cannot name them is describing a feature.
- FedRAMP Moderate, if it will hold CUI. The provider must be FedRAMP Moderate authorized or meet the equivalency of the Department's December 2023 memo, even for encrypted CUI (6), and follow the clause's incident reporting rules (12).
- Evidence in writing. A requirement handled by a provider is "considered MET if adequate evidence is provided" (8).
- Records an assessor can read. Who moved what, where and when, in final form (3).
- What stays yours. A managed service provider "is not required to have its own CMMC assessment" (6), but its services are assessed "as part of the OSA's assessment" (3), and the OSA is you.
How to maintain CMMC compliance after certification
You maintain CMMC compliance by keeping the assessment on its cycle, the affirmation annual and the evidence current.
What falls due, and when
Figure 2 shows the fixed schedule after certification, from the assessment cycle to the six years you keep evidence (3, 8).

Adapted from: 32 CFR 170.15 to 170.18, 170.21 and 170.22, and the CMMC Assessment Guide, Level 2 (3, 8).
To maintain compliance between assessments you also repeat the work the requirements prescribe (16):
- assess the controls "periodically" and monitor them "on an ongoing basis" (3.12.1, 3.12.3);
- update the system security plan "periodically" (3.12.4);
- scan for vulnerabilities and correct flaws "in a timely manner" (3.11.2, 3.14.1);
- train staff on security risks and their duties (3.2.1, 3.2.2);
- report cyber incidents to DoD within 72 hours (12).
Why the annual affirmation carries legal weight
The affirmation is signed by the organization's senior level representative (3). A false one is a legal risk: since 2021 the Justice Department has used the False Claims Act against contractors "knowingly misrepresenting their cybersecurity practices or protocols" (19), and in October 2024 The Pennsylvania State University paid $1,250,000 over allegations that it failed to implement required controls and misrepresented when it would (20).
Keep CUI inside the boundary in your data workflows
Change breaks evidence between assessments: a new file-sharing tool, a new site or subcontractor, or a change inside the environment (6). Your data workflows keep the boundary: classify files as they are created, control what enters the enclave, and stop CUI being copied out. Whether a change needs a new assessment "is the responsibility of the Affirming Official" (6).
CMMC assessment guides and documents, by name and version
A Level 2 assessment rests on three public documents, and Level 1 has its own guide.
Table 4. The documents behind a CMMC assessment.
| Document | What it answers |
|---|---|
| CMMC Assessment Guide, Level 1, Version 2.13, September 2024 | How to self-assess the 15 Level 1 requirements (21) |
| CMMC Scoping Guide, Level 2, Version 2.13, September 2024 | What is inside and outside your Level 2 scope (13) |
| CMMC Assessment Guide, Level 2, Version 2.13, September 2024 | What an assessor examines for each requirement (8) |
| NIST SP 800-171A, June 2018 | The assessment procedures behind those objectives (8, 14) |
Sources: as numbered in each row. The CMMC guides are on the DoD CIO site named in the rule's appendix A (3).
Check the edition: CMMC still assesses against the June 2018 SP 800-171A, although NIST withdrew it in May 2024 (8, 14). And the guides "do not have the force and effect of law" (8, 13): where a guide and the regulation differ, the regulation decides.
Common CMMC compliance mistakes
- Treating a tool as compliance. Buying a service moves the work, not the accountability (3, 6).
- Treating a self-assessment as practice. Level 1 (Self) and Level 2 (Self) are statuses in their own right (3).
- Drawing the network diagram before deciding where CUI lives. The scope is fixed before the assessment starts (3).
- Stopping work during the suspension. Phase 1 self-assessments and DFARS 252.204-7012 still apply (2, 7), so cybersecurity compliance work continues.
Next steps for CMMC compliance
- Find your level in the clause in front of you and the information you will handle.
- Fix the scope and run a gap assessment before anything is bought or written.
- Plan what recurs: the assessment cycle, the annual affirmation and current evidence.
Shortlist CMMC compliance companies. If you are comparing providers, how to compare CMMC compliance companies sets out what to check.
Get your scope and your gaps settled before you bid
We are a CMMC Registered Practitioner Organization with Cyber AB Registered Practitioners on staff. Our work is readiness:
- fixing the assessment scope;
- running a gap assessment against the requirements for your level;
- drafting the system security plan and the plan of action and milestones;
- developing the policies and procedures behind them.
The certification assessment itself is performed by a separate accredited C3PAO, not by us. If a solicitation or a prime has put a level in front of you, talk to our CMMC compliance consulting team about what it will take.
Sources
- eCFR, 48 CFR subpart 204.75, Cybersecurity Maturity Model Certification. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-A/part-204/subpart-204.75
- Department of War, Forging the Arsenal of Freedom: Department of War Suspends CMMC Phase II Requirements, 13 July 2026. https://www.war.gov/News/Releases/Release/Article/4542329/forging-the-arsenal-of-freedom-department-of-war-suspends-cmmc-phase-ii-require/
- eCFR, 32 CFR part 170, Cybersecurity Maturity Model Certification (CMMC) Program. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170
- eCFR, 48 CFR 252.204-7021, Contractor Compliance with the Cybersecurity Maturity Model Certification Level Requirements. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-H/part-252/subpart-252.2/section-252.204-7021
- eCFR, 48 CFR 252.204-7025, Notice of Cybersecurity Maturity Model Certification Level Requirements. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-H/part-252/subpart-252.2/section-252.204-7025
- DoW CIO, CMMC Frequently Asked Questions, July 2026. https://dowcio.war.gov/Portals/0/Documents/CMMC/FAQsv6.pdf
- DoW CIO, Cybersecurity Maturity Model Certification Procedures (Attachment 1 to the memorandum implementing the suspension of CMMC Phase II), 13 July 2026. https://dowcio.war.gov/Portals/0/Documents/Library/ImplementingSuspensionCMMC-PhaseII.pdf
- DoD CIO, CMMC Assessment Guide, Level 2, Version 2.13, September 2024. https://dowcio.war.gov/Portals/0/Documents/CMMC/AssessmentGuideL2v2.pdf
- NIST, SP 800-171 Rev. 3, Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations. https://csrc.nist.gov/pubs/sp/800/171/r3/final
- Office of the Federal Register, Cybersecurity Maturity Model Certification (CMMC) Program, 89 FR 83092. https://www.federalregister.gov/documents/2024/10/15/2024-22905/cybersecurity-maturity-model-certification-cmmc-program
- Office of the Federal Register, Defense Federal Acquisition Regulation Supplement: Assessing Contractor Implementation of Cybersecurity Requirements, 90 FR 43560. https://www.federalregister.gov/documents/2025/09/10/2025-17359/defense-federal-acquisition-regulation-supplement-assessing-contractor-implementation-of
- eCFR, 48 CFR 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-H/part-252/subpart-252.2/section-252.204-7012
- DoD CIO, CMMC Scoping Guide, Level 2, Version 2.13, September 2024. https://dowcio.war.gov/Portals/0/Documents/CMMC/ScopingGuideL2v2.pdf
- NIST, SP 800-171A, Assessing Security Requirements for Controlled Unclassified Information, June 2018. https://csrc.nist.gov/pubs/sp/800/171/a/final
- Office of the Assistant Secretary of War for Acquisition and Sustainment, Class Deviation 2026-O0025, Revision 3: Revolutionary FAR Overhaul Part 40, DFARS Part 240, 3 September 2026. https://www.acq.osd.mil/dpap/dars/classdev/DFARS_RFO/Part-240/2026-O0025_Rev3_TAB_A_Deviation_Memo.pdf
- NIST, SP 800-171 Rev. 2, Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations, February 2020 (updated January 2021). https://csrc.nist.gov/pubs/sp/800/171/r2/upd1/final
- Office of the Federal Register, Cybersecurity Maturity Model Certification (CMMC) 2.0 Updates and Way Forward, 86 FR 64100, 17 November 2021. https://www.federalregister.gov/documents/2021/11/17/2021-24880/cybersecurity-maturity-model-certification-cmmc-20-updates-and-way-forward
- eCFR, 32 CFR part 2002, Controlled Unclassified Information (CUI). https://www.ecfr.gov/current/title-32/subtitle-B/chapter-XX/part-2002
- U.S. Department of Justice, Deputy Attorney General Lisa O. Monaco Announces New Civil Cyber-Fraud Initiative, 6 October 2021. https://www.justice.gov/archives/opa/pr/deputy-attorney-general-lisa-o-monaco-announces-new-civil-cyber-fraud-initiative
- U.S. Department of Justice, The Pennsylvania State University Agrees to Pay $1.25M to Resolve False Claims Act Allegations Relating to Non-Compliance with Contractual Cybersecurity Requirements, 22 October 2024. https://www.justice.gov/archives/opa/pr/pennsylvania-state-university-agrees-pay-125m-resolve-false-claims-act-allegations-relating
- DoD CIO, CMMC Assessment Guide, Level 1, Version 2.13, September 2024. https://dowcio.war.gov/Portals/0/Documents/CMMC/AssessmentGuideL1v2.pdf
- eCFR, 48 CFR 52.204-21, Basic Safeguarding of Covered Contractor Information Systems. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-H/part-52/subpart-52.2/section-52.204-21
- NIST, SP 800-172, Enhanced Security Requirements for Protecting Controlled Unclassified Information: A Supplement to NIST Special Publication 800-171, February 2021. https://csrc.nist.gov/pubs/sp/800/172/final




FAQ
Is CMMC now required?

Yes, with one change. The rule is in force and Phase 1 self-assessment requirements "remain firmly in place" (2). The Department of War suspended the transition to Phase 2 on 13 July 2026, so Level 2 (C3PAO) and Level 3 (DIBCAC) may not be designated for now (7), and DFARS Class Deviation 2026-O0025 binds contracting officers to that (15). DFARS 252.204-7012 still applies.
What happens if I don't get CMMC certified?
You lose the work. A contracting officer "shall check SPRS and not award" to an offeror without a current CMMC status at the level the solicitation requires (1), and the same check blocks an option exercise or an extension on a contract you already hold. A Conditional status still wins you the award at Levels 2 and 3; at Level 1 only a Final status counts.
How much does CMMC compliance cost?
It depends on your level, on how much of your environment falls inside the assessment scope, and on how many of the requirements you already meet. Scope is the biggest single variable, which is why it is fixed first (3). For a breakdown of what drives the number, see what CMMC certification costs.
How long does CMMC certification last?
Three years for a Final Level 2 or Level 3 assessment, and one year for a Final Level 1 (Self): those are the windows in which a status counts as current (4). The Department states the same cadence in words, annually at Level 1 and every three years at Levels 2 and 3 (6). A Conditional status is much shorter, expiring 180 days after its CMMC Status Date unless the POA&M is closed out (3).
Who is responsible for CMMC compliance?
Your organization, and one named person inside it. The Affirming Official is "the senior level representative" responsible for the organization's compliance, and the affirmation goes in after every assessment and annually thereafter (3). External providers do not take that on. A managed service provider handling CUI is assessed inside your scope and needs no certification of its own, and you must require and ensure that a cloud service provider holding CUI meets requirements equivalent to the FedRAMP Moderate baseline (3, 6).
Is NIST 800-53 the same as CMMC?
No, but they are related. CMMC Level 2 assesses the requirements of NIST SP 800-171 Revision 2 (3). NIST derived those requirements from FIPS 200 and the moderate security control baseline of NIST SP 800-53, tailored for CUI on nonfederal systems, and warns that meeting them does not automatically satisfy NIST SP 800-53 (16). No CMMC level is scored against NIST SP 800-53.
What is a CUI enclave in CMMC compliance?
A segment of your environment that is logically separated from the rest and holds the CUI, so the assessment scope stops at its edge rather than covering your whole company. Where the enclave is otherwise logically separated, sending properly encrypted CUI out of it "does not incur an extension of the CMMC Assessment Scope to include the enterprise networking components" (6). Encryption on its own does not create that separation.
About the author
Patrick Ibrahim
—
Senior Director, Compliance Services
With over a decade of experience in information security, working with hundreds of companies including fortune 50 organizations and startups alike, Patrick excels at all things compliance.
Patrick’s expertise spans ISO, PCI, HITRUST as well as CMMC in the Federal space, with hands-on experience conducting combined audits (PCI DSS, SOC 2, HITRUST). With a proven track record in BCPDR planning and realistic tabletop testing, Patrick is passionate about delivering actionable strategies that not only secure data but also ensure business continuity during disruptions.