SOC 2 Compliance for Startups: Steps, Timeline, Cost, and Partners
Published on
January 6, 2026
/
updated on
October 21, 2026
A startup's path to a first SOC 2 report in 6 steps, with the pentest question, cost drivers, and 7 questions for a CPA firm.
In SOC 2 compliance for startups, the first goal is one document, an attestation report from a certified public accountant (CPA) firm on the controls that protect your customers' data (1). You get there in six steps: scope the system, run a readiness assessment, close the gaps, collect evidence, bring in a CPA firm, and keep the report current.
An enterprise prospect's security questionnaire asks for "your SOC 2 report", and a team with no security hire has to work out what that means.
Buyers judge the report itself, and an experienced reviewer can spot one built from a template. Many companies get SOC 2 because a customer's contract requires it, and if that customer rejects the report, "it's not worth the paper it's on", says Jeff Cook, a member of the SOC 2 Working Group at the American Institute of Certified Public Accountants (AICPA) (2). The firm you choose matters as much as the controls you build.
This guide shows founders and CTOs of SaaS, fintech, health tech, and AI startups when SOC 2 is needed, which type to get first, the timeline and cost, whether you need a pentest, and how to choose consultants, CPA firms, and platforms.
What SOC 2 Is and What a Startup Actually Receives
People call it SOC 2 certification, yet what a startup receives is an attestation report. SOC 2 belongs to the AICPA's System and Organization Controls (SOC), "a suite of service offerings CPAs may provide in connection with system-level controls of a service organization" (1). CPAs perform the examination under the AICPA's attestation standards: they test your controls, and they give an opinion on them (2).
The AICPA's Journal of Accountancy notes that "compliance" is "a term never used in SOC 2 examinations" (2). The examination ends in a SOC 2 report carrying the CPA's opinion rather than a compliance certificate.
The report covers one or more of five trust services categories. Security is addressed in most SOC 2 examinations, and its criteria, the common criteria, are part of the set for every category you include. Even a report that leaves the security category out, which the criteria call "uncommon", still uses the common criteria for the categories it covers (3). The other four categories add criteria of their own.
Table 1. The five trust services categories
| Category | What it covers | Who might add it (examples) |
|---|---|---|
| Security | Information and systems protected against unauthorized access, unauthorized disclosure and damage | Included in most SOC 2 reports |
| Availability | Information and systems available for operation and use to meet the entity's objectives | A service customers depend on to stay up |
| Processing integrity | System processing that is complete, valid, accurate, timely, and authorized | A platform that processes transactions for customers |
| Confidentiality | Information designated as confidential, protected to meet the entity's objectives | A service holding customers' confidential business data |
| Privacy | Personal information collected, used, retained, disclosed, and disposed of to meet the entity's objectives | A service handling sensitive data such as patient records |
Source: 2017 Trust Services Criteria, .12 to .15 (3); read October 2026.
SOC 2 reports "are restricted to specified parties with sufficient knowledge and understanding of the service organization's system" (2), so the report goes only to the customers who ask for it. The version you can publish is a SOC 3, a general use report that "can be freely distributed" (4).
A SOC 1 is a different report: it evaluates controls likely relevant to customers' internal controls over financial reporting (2). The SOC 1 vs SOC 2 comparison explains which one a buyer means, and the guide to what a SOC 2 report contains walks through its sections.
Why SOC 2 Compliance Matters for Startups
SOC 2 matters to a startup because enterprise customers ask for it before they sign, and one report answers what their security review would otherwise ask line by line. A report helps a startup in these ways:
- It answers security questionnaires. Enterprise buyers' procurement teams send security questionnaires about access, encryption, incident response, and vendors. The rows a report already covers can point to it instead of a fresh written answer.
- It can shorten the security review in your sales cycles. A buyer's security review that starts from a report has fewer open questions to clear before signature. If a competing vendor in the same deal has no report, yours settles questions the buyer still has to ask them.
- It gives the buyer's risk reviewers what they need. In the words of the AICPA's Journal of Accountancy, SOC 2 reports "provide a level of detail sufficient to address the user's vendor risk management needs" (2).
- It builds the security program you need anyway. Readiness work puts access reviews, change management, logging, and incident response in place. The same controls improve your security posture whether a buyer reads the report or not.
When Does a Startup Need SOC 2?
The clearest trigger for SOC 2 for startups is a written customer request, in a security questionnaire or in a contract clause. Other signals can bring the start forward, and others show it can wait.
Start now if:
- One of your enterprise deals is in procurement, and the buyer's checklist or draft contract asks for a SOC 2 report.
- Your buyers are regulated: payment, lending, and financial data platforms are asked for a report by the banks they serve, and vendors that process patient data are asked by their healthcare customers.
- Several mid-market prospects or existing enterprise clients have sent the same security review questions.
- A funding round's due diligence asks for a SOC 2 report or for evidence of your security program.
It can wait if:
- No customer has asked yet, and your product and cloud setup still change from week to week.
- Your current buyers are small companies that accept a completed questionnaire without a report.
- You would be pursuing SOC 2 only because competitors mention it, with no request in the pipeline.
SaaS startups also have a middle path: a readiness assessment now, and the examination once a buyer asks. The readiness work tells you what the examination would find, and the small-team section below shows how to keep it lean.
SOC 2 Type 1 or Type 2: Which Should a Startup Get First?
Get a Type 1 first when a deal needs a report soon and your controls are new; go straight to a Type 2 when buyers want evidence that the controls operated over time. Before you choose, ask the buyer which type its questionnaire accepts.
The Trust Services Criteria define the two. A Type 2 report covers controls "throughout a specified period" and includes an opinion on whether they operated effectively, with the service auditor's tests and their results. A Type 1 addresses the same subject matter without that opinion and without the tests (3).
Table 2. SOC 2 Type 1 vs Type 2 for a first report
| Type 1 | Type 2 | |
|---|---|---|
| What the opinion covers | The system description and the design of the controls | The description, the design, and the operating effectiveness of the controls |
| Period | No opinion on operation over a period | A specified period, often called the observation period |
| Tests of controls in the report | Not included | Included, with the results |
| When a startup might pick it | A deal needs a report soon and the controls are new | Buyers ask for a Type II report or for evidence over time |
Source: 2017 Trust Services Criteria, .16 and its appendix A, Glossary (3); read October 2026.
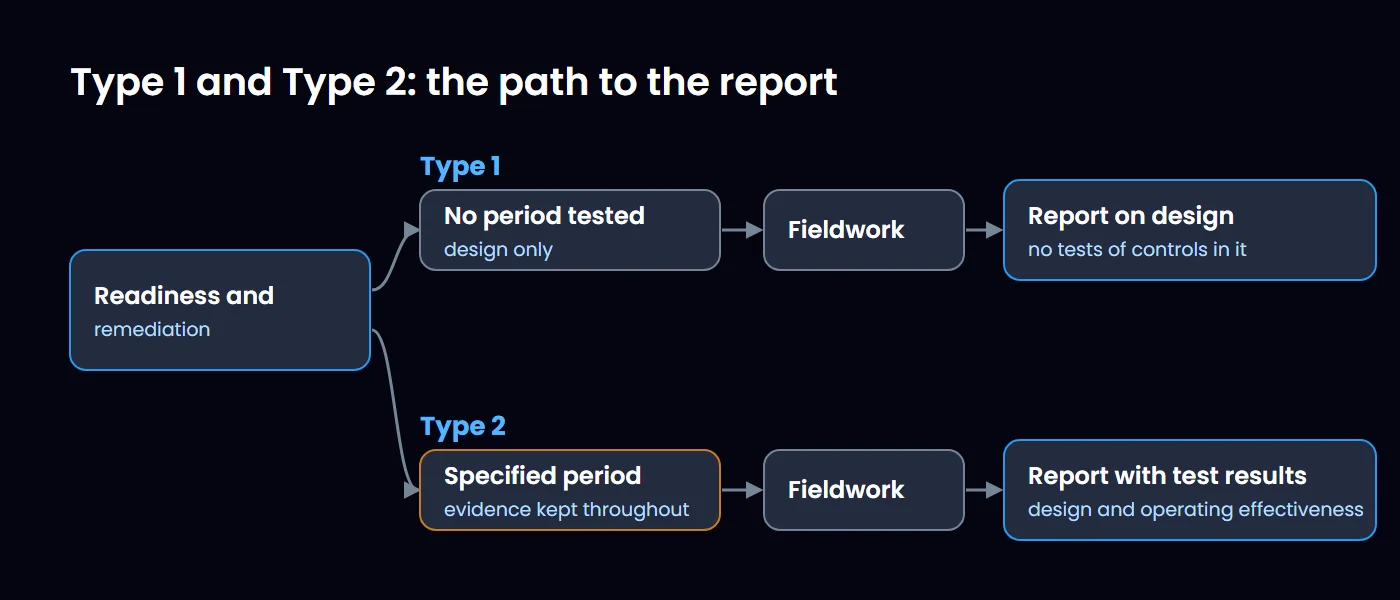
The length of the Type 2 period is set when you scope the examination. A buyer that asks for evidence over time will still need the Type 2, so plan the Type 1's description and controls to carry into the Type 2 period that follows. The SOC 2 Type 1 vs Type 2 comparison covers both reports in detail.
How to Get SOC 2 Compliance as a Startup: 6 Steps
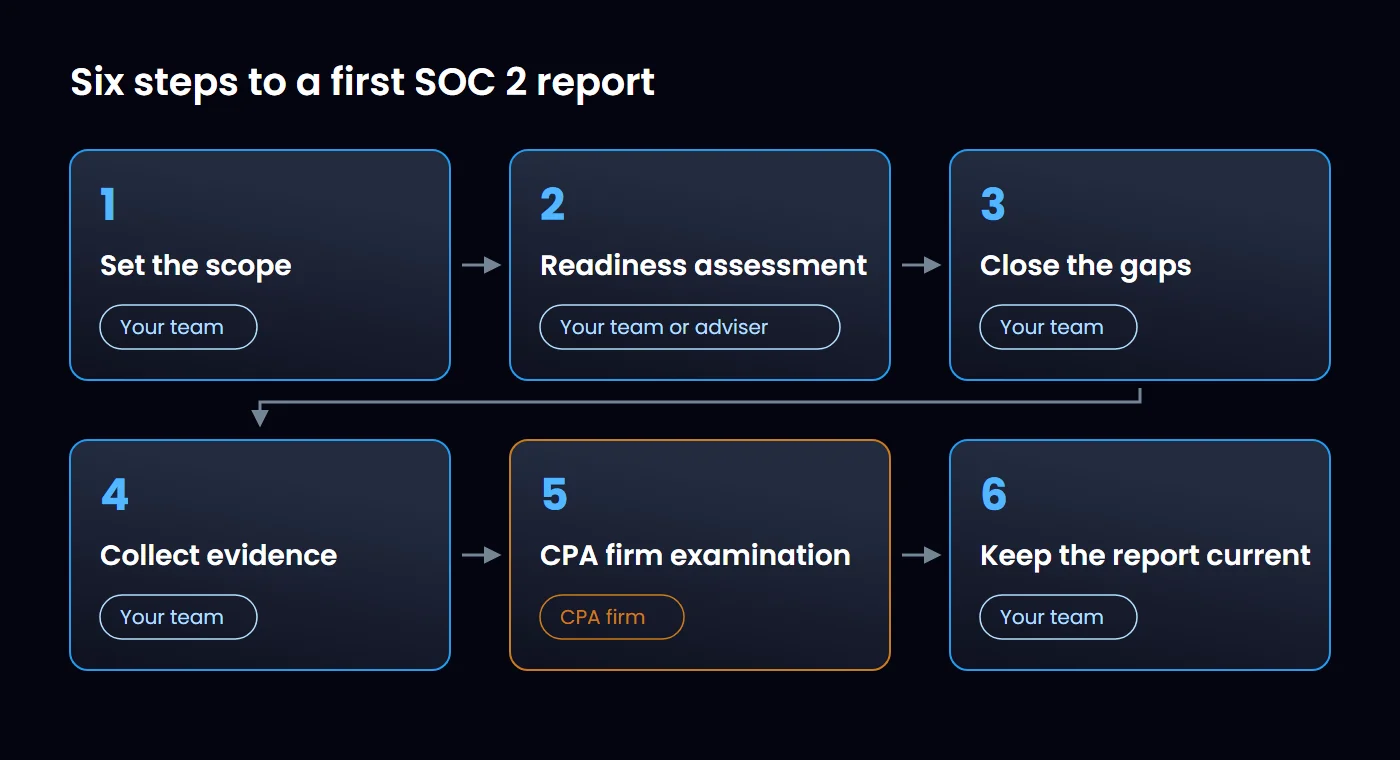
The SOC 2 process for a startup runs in six steps, from scoping to keeping the report current. The guide to SOC 2 attestation covers the examination itself in more depth.
Step 1: Set the Scope Your Customers Ask For
Scoping sets the system boundary, the trust services categories, and the report type. Your team decides them, because they describe your service; an adviser can guide each choice and document what you settle on. Every place customer data lives, a failover environment or an analytics database included, belongs inside the boundary or is named as out of scope.
For a Type 2, choose the CPA firm at this stage too, because its examination covers the period your controls run through and that period is set in advance. The small-team section covers how narrow to keep the scope.
Step 2: Run a Readiness Assessment
A readiness assessment compares the controls you run today with the criteria in scope and lists every gap. Done by your team or by an adviser, this gap analysis shows your SOC 2 readiness before anyone pays for an examination. It includes a SOC 2 risk assessment: which threats to your service matter, and which controls answer them. The output is a gap assessment report, with each gap mapped to its criterion and to the evidence that would close it. That report sets the order of the remediation work.
Step 3: Close the Gaps With Policies and Controls
Your team writes the policies and puts the SOC 2 controls in place; an adviser can specify what each control must achieve and review drafts. The SOC 2 requirements guide lists the criteria in full. Work through these security controls in the first remediation pass:
- Access controls: single sign-on, multi-factor authentication, and quarterly access reviews.
- Change management: code review and approval before a release reaches production.
- Logging and monitoring: alerts someone is assigned to answer.
- Vendor management: a list of vendors with access to customer data, reviewed on a schedule.
- Incident response: a written plan, tested before the period starts.
- Backups and disaster recovery: restores that have been tested.
- Security awareness training: for every hire, with a record of completion.
Write the security policies and procedures to match what the team already does. A policy that describes a practice nobody follows can show up as an exception when the CPA firm tests it.
Step 4: Collect Evidence From Day One
For a Type 2, the service auditor tests whether the controls operated "throughout a specified period" (3), so the evidence has to cover the whole period. Evidence collection starts the day the period starts:
- Access approvals and removals, with dates
- Change tickets with their reviews
- Completed access reviews and training records
- Incident and alert records with their follow-up
Assign each control an owner who captures its evidence on a schedule. Where the same capture repeats every week, a tool can take it over.
Step 5: Bring In a CPA Firm for the Examination
SOC reports are "examinations performed by CPAs in accordance with the AICPA's Statements on Standards for Attestation Engagements" (2), so the SOC 2 audit itself is a CPA firm's work. The controls it examines are those "included in management's description" of your system (3): your management writes that description, and the firm evaluates it.
During fieldwork the firm tests the controls and asks for their evidence; your team gives the answers. For a Type 2, the fieldwork is completed after the period ends. Audit preparation means a current evidence register and control owners who know where their evidence lives. The questions to ask before you sign are in the section on choosing SOC 2 assessment partners.
Step 6: Keep the Report Current
A Type 2 covers one period, and the next report covers the next one. Controls and evidence keep running between compliance audits, and the scope is revisited when the system or the vendors change. Between reports, watch a few signals:
- How fast alerts get a response
- How many vulnerabilities the last quarter found, and how many were closed
- Whether access was removed when people left
The FAQ below covers how long a report stays useful to buyers.
Getting SOC 2 With a Small Team and a Tight Budget
To achieve SOC 2 with a small team and no full-time compliance hire, keep the scope to what the buyer asked for and pay for outside help only where the team lacks the expertise. These moves keep the cost down:
- Scope to the request. If the buyer asked about security, a security-only report is possible: the criteria may be used for a category "either individually or in combination with controls in other categories" (3), and for security the common criteria are the complete set. Draw the boundary around the service that buyer uses, not around the whole company.
- Name one owner, with control owners in each team. One person, such as the CTO or a senior engineer, owns security and compliance until there is a security team, and keeps the plan moving. Engineering owns change management, operations owns access and backups, and people operations owns onboarding and training records.
- Buy help where you lack the expertise. A readiness assessment, a policy review, or a penetration test can come from an outside service provider, while the daily operation of the controls stays with your team. That split keeps the compliance program yours after the report.
- Automate evidence that repeats. Screenshots of the same settings every week are the first candidates for a tool, covered in the section on compliance automation below.
- Fix the highest risks first. Rate each gap by its impact and its likelihood, close the ones that score highest, and put the rest on a dated roadmap.
The guide to SOC 2 for SaaS companies covers the same planning for a software business, from the timeline to the control areas that matter most.
How Long SOC 2 Takes and What It Costs a Startup
How long SOC 2 takes depends on how many controls already run, how much sits in scope, and whether you need a Type 2 period. The work runs in this order:
Table 3. The phases of a first SOC 2 report
| Phase | What happens | What sets its length |
|---|---|---|
| Readiness assessment | Scoping and the gap analysis | The size of the scope |
| Remediation | Policies written, controls put in place | How many gaps the assessment found |
| Type 2 period | Controls operate while evidence is collected | The period set when you scope the examination |
| Fieldwork | The CPA firm tests the controls | The number of controls and how ready the evidence is |
| Report | The firm issues its report and opinion | The firm's review process |
Source: 2017 Trust Services Criteria, .16, for the Type 2 period (3); read October 2026.
A Type 1 skips the period row, so the quicker path is a Type 1 on a narrow scope, then a Type 2 once the controls have run.
The price follows the same scope. The cost drivers are:
- The systems and locations inside the scope
- The categories you add beyond security
- The report type and the length of the period
- How much remediation your controls need
- Whether evidence collection is already tooled
Readiness consulting and the examination are billed separately, so ask for both prices before comparing offers. Treat a published price range as one vendor's estimate: the drivers above decide your quote, and the SOC 2 cost breakdown walks through each one.
Startup SOC 2 Pentest: Is a Penetration Test Required?
No trust services criterion makes a penetration test mandatory for SOC 2. The criteria list penetration testing among the evaluations management may use, depending on its objectives (3). If a buyer's questionnaire or your CPA firm asks for one, ask what scope they expect, then check the report against the list below.
What the Trust Services Criteria Say About Penetration Tests
The mention sits in a point of focus under CC4.1, the criterion on monitoring controls:
"Depending on the entity's objectives, such risk and control evaluations may include first- and second-line monitoring and control testing, internal audit assessments, compliance assessments, resilience assessments, vulnerability scans, security assessment, penetration testing, and third-party assessments."
The same document adds:
- Points of focus are not a checklist. Using the criteria "does not require an assessment of whether each point of focus is addressed" (3).
- Scans have their own point of focus. Under CC7.1, vulnerability scans run "on a periodic basis and after significant changes are made to the environment" (3).
A scan and a pentest are different security testing methods. NIST SP 800-115 says vulnerability scanning "can help identify outdated software versions, missing patches, and misconfigurations" (5). In a penetration test, by its definition, "assessors mimic real-world attacks to identify methods for circumventing the security features" of the system under test (5).
What a Pentest Report Needs to Show
When a buyer or CPA firm asks for a pentest, read the report against the SOC 2 scope before you hand it over. A useful report shows:
- A scope that matches the system boundary: the web application, the API, and the cloud infrastructure the service runs on.
- Test dates: early enough that you can fix the findings before the CPA firm's fieldwork.
- Findings ranked by risk: the most serious security risks first, so the team knows what to fix first.
- Remediation evidence: what changed for each finding, and a retest that confirms the fix.
Penetration testing at CyberCrest includes web application, API, and cloud security testing among its six test areas, with manual testing backed by automated scanning. The guide to vulnerability assessment vs penetration testing compares the two methods in depth.
How to Choose SOC 2 Assessment Partners for Startups
A first report can involve three kinds of partner, and only a CPA firm signs the report:
- Readiness consultants run readiness assessments, which end in a gap assessment report and a remediation plan, and guide the remediation.
- Licensed CPA firms examine your controls under the AICPA's attestation standards and issue the SOC 2 report (2).
- Compliance automation platforms collect evidence and monitor controls; the next section covers when one is worth buying.
The firm that examines you must not take on your management responsibilities. The AICPA Code of Professional Conduct counts "accepting responsibility for designing, implementing, or maintaining internal control" among them (6). A CPA who takes one on impairs independence. The internal controls stay yours to design and run, whoever helps with readiness.
The AICPA's Journal of Accountancy lists what clients should check before engaging a firm (2); questions 1 to 4 below build on it. Before you sign with a CPA firm, ask:
- What is your size and capacity, and which clients can we speak to as references?
- Which SOC 2 auditors will staff our engagement, what are their qualifications and experience, and what did your last peer review find? The AICPA Peer Review Program runs a public file search (7).
- What is the scope of the examination, and which sampling procedures will you use to test our controls?
- How does your firm maintain its independence?
- Have you examined SaaS companies or other startups at our stage, with a system like ours?
- What will this year's report cost, what will next year's cost, and what exactly does that scope include?
- If your timeline or price is well below the other quotes we have, what explains the gap?
Then judge each offer against the journal's test: whether it is "unrealistically fast, easy, or cheap" (2). In May 2026 the AICPA guided its peer reviewers to look at "the reasonableness of SOC 2 engagement timelines" (8). Its SOC page also carries a notice that it "is looking into allegations published anonymously about the business practices of a compliance vendor that offers Systems and Organization Control (SOC) services" (1). Ask the audit firms on your shortlist how long the audit process for your engagement will take and why, and whether the report will be written for your system.
Our comparison of the best SOC 2 compliance companies profiles ten consultants and CPA firms, plus six compliance automation platforms.
Is a SOC 2 Compliance Automation Platform Worth It for a Startup?
A compliance automation platform is worth it when the same evidence has to be captured every week and nobody on the team has the hours to do it by hand. The AICPA's Journal of Accountancy describes such tools connecting to a client's systems to "automatically pull data and evidence into a central, real-time dashboard" (2). A platform can:
- Pull evidence from your cloud, code, and identity systems on a schedule.
- Track policies with their acknowledgments and training records.
- Run continuous monitoring and flag a control that drifts out of its setting.
A platform cannot issue the report. In the journal's words, "Because most of the new tool providers are not CPA firms, they cannot attest that the controls in place are effective and appropriate" (2). A platform keeps you audit ready; the opinion that makes you SOC 2 compliant in a buyer's eyes still comes from the CPA firm.
If you buy a compliance platform, check these first:
- Integrations: it connects to the stack you run today.
- Your CPA firm: the firm can work from the platform's evidence exports.
- The second-year price: what renewal costs once the first report is out.
Common SOC 2 Mistakes Startups Make
These mistakes add cost or delay to a first SOC 2 report, and each has a fix:
- Scoping more than the buyer asked for. Adding categories or systems nobody requested adds controls, evidence, and fees. Scope to the request; see the small-team section.
- Writing policies that describe practices nobody follows. The CPA firm tests what the policy says. Write each policy from what the team already does; see Step 3.
- Starting evidence collection late. A Type 2 needs evidence for the whole period, and evidence for months already past is hard to produce afterward. Start on the first day of the period; see Step 4.
- Treating a vulnerability scan as a penetration test. A scan finds known weaknesses; a pentest tries to get around your security features. Ask which one a buyer means before you order either; see the pentest section.
- Buying the fastest, cheapest report. A report a buyer rejects is wasted money. Vet every firm before you sign, with the questions in the section on choosing assessment partners.
Prepare for SOC 2 Compliance with CyberCrest
Our SOC 2 compliance services cover the work around the examination: readiness, guidance on the remediation your team carries out, and preparing you for the fieldwork and supporting you through it. Work on SOC 2 compliance for startups starts with a scoping call around the report your first enterprise buyer asked for.
Talk to an expert about your buyer's SOC 2 request.
Sources
- AICPA & CIMA, System and Organization Controls: SOC Suite of Services. https://www.aicpa-cima.com/resources/landing/system-and-organization-controls-soc-suite-of-services
- Journal of Accountancy (AICPA & CIMA), Promises of "fast and easy" threaten SOC credibility, February 1, 2026. https://www.journalofaccountancy.com/issues/2026/feb/promises-of-fast-and-easy-threaten-soc-credibility/
- AICPA & CIMA, 2017 Trust Services Criteria (With Revised Points of Focus, 2022), TSP section 100. https://www.aicpa-cima.com/resources/download/2017-trust-services-criteria-with-revised-points-of-focus-2022
- AICPA & CIMA, SOC 3: SOC for Service Organizations: Trust Services Criteria for General Use Report. https://www.aicpa-cima.com/topic/audit-assurance/audit-and-assurance-greater-than-soc-3
- NIST, SP 800-115, Technical Guide to Information Security Testing and Assessment, sections 4.3 and 5.2. https://csrc.nist.gov/pubs/sp/800/115/final
- AICPA & CIMA, AICPA Code of Professional Conduct, ET section 1.295.030, Management Responsibilities. https://pub.aicpa.org/codeofconduct/ethicsresources/et-cod.pdf
- AICPA & CIMA, AICPA Peer Review Program: Public File Search. https://peerreview.aicpa.org/public_file_search.html
- Journal of Accountancy (AICPA & CIMA), AICPA guides peer reviewers to address SOC 2 risks, May 14, 2026. https://www.journalofaccountancy.com/issues/2026/may/aicpa-guides-peer-reviewers-to-address-soc-2-risks/
- ISO, ISO/IEC 27001:2022, Information security management systems. https://www.iso.org/standard/27001




FAQ
Is SOC 2 legally required?

CyberCrest's position is that no law requires a SOC 2 report. The report comes from an examination a company commissions: SOC reports are "examinations performed by CPAs in accordance with the AICPA's Statements on Standards for Attestation Engagements" (2). In SOC 2 for startups, the request comes in an enterprise buyer's security questionnaire or contract.
How hard is it to get SOC 2?
It is manageable for a small team that scopes narrowly. The hard part is time: controls have to be designed, put in place, and, for a Type 2, operated through a specified period while you collect the evidence. A Type 1 carries no opinion on operating effectiveness (3), so it has no period of operation to test, which makes it the easier first report.
Does a startup need all five trust services criteria?
No. The criteria may be used for a category "either individually or in combination with controls in other categories" (3). Security is addressed in most SOC 2 examinations, and the common criteria apply to every category you include, even in the uncommon report that leaves security out. The other four categories, availability, processing integrity, confidentiality, and privacy, are added when customers need assurance over them.
What happens if a startup fails a SOC 2 audit?
A SOC 2 audit does not end in a pass or a fail mark. It ends in the CPA firm's opinion, and a Type 2 report also includes "a detailed description of tests of controls performed by the service auditor and the results of those tests" (3). Buyers read those results, so fix what the tests found and plan the next period with the controls in place.
How long is a SOC 2 report valid?
A Type 2 report covers its stated period and has no expiry date of its own. CyberCrest's view is that customers usually want one whose period ended within the last year: in October 2026, a report whose period ended in December 2025 is inside that window, and one whose period ended in June 2025 is not. To cover the gap until the next report, management can give customers a bridge letter, a management statement with no CPA opinion.
What is the difference between SOC 2 and ISO 27001?
SOC 2 ends in a CPA firm's attestation report on the controls that protect your customers' data (2). ISO/IEC 27001 sets the requirements for an information security management system: how a company manages risks to its data and keeps improving that system (9). Certification to the standard is "one way to demonstrate to stakeholders and customers" that a company is committed and able to manage information securely (9). The SOC 2 vs ISO 27001 comparison sets them side by side, and CyberCrest's ISO 27001 compliance services cover preparing for certification.
About the author

Ron Gupta
—
Senior Director: Governance, Risk and Compliance
Getting his start in tech as an analyst and founder at Via Digital ID, Ron brings to the table a unique approach to cyber security. With over a decade of experience in GRC, Ron has developed and honed a skillset rich in combined audit and assessment as well as risk management and mitigation.
Ron’s ability to convey critical information, results and plans of action to executive leadership is a key skill that allows him to propel the clients he engages with to success. Ron is adept at taking target frameworks, implementing them within environments while reducing overall risk to organizations.