HIPAA Violation Fines and Penalties: How Much Can a Violation Really Cost?
Published on
July 23, 2025
/
updated on
October 21, 2026
Civil penalties of $145 to $2,190,294 per violation under HIPAA in 2026, prison terms of up to 10 years, and 6 recent OCR cases.
The Department of Health and Human Services (HHS) sets civil HIPAA violation fines and penalties at $145 to $2,190,294 per violation, in the 45 CFR 102.3 table amended on 28 January 2026 (1, 2). The criminal maximum is a $250,000 fine and 10 years in prison, for intent to sell or harm (3).
This guide is for privacy officers and practice administrators at clinics, health plans, and vendors facing a complaint, a breach report, or a data request from the HHS Office for Civil Rights (OCR). The inflation-adjusted amounts appear in 45 CFR Part 102, which 45 CFR 160.404 says is updated annually, so older figures elsewhere may be outdated (4). A violation means failing a requirement of the HIPAA Administrative Simplification Rules, such as the Privacy, Security, or Breach Notification Rule; the Enforcement Rule sets the penalties (5). Filing a complaint is covered in how to report a HIPAA violation.
HIPAA Violation Penalties: Civil and Criminal
HIPAA civil and criminal penalties come from two different sections of federal law. On the civil side, OCR investigates, and under 42 U.S.C. 1320d-5 the covered entity or business associate pays a settlement or a civil money penalty (6, 7, 8). Under 42 U.S.C. 1320d-6, a knowing violation is a crime (3) that the Department of Justice (DOJ) investigates when OCR refers the complaint (9). Figure 1 shows both tracks.

Civil Penalties for HIPAA Violations
A civil penalty for violating HIPAA is imposed on a covered entity or business associate that the Secretary of HHS determines has violated an administrative simplification provision, meaning a requirement of the HIPAA rules. The covered entity is also liable for violations by its agents, including workforce members and business associates acting within the scope of the agency (7). When more than one organization is responsible, each one is penalized.
The amount depends on culpability. The regulation defines reasonable diligence as "the business care and prudence expected from a person seeking to satisfy a legal requirement under similar circumstances" (10), and two more terms set the tier:
- Reasonable cause: the organization knew, or by exercising reasonable diligence would have known, that it was violating a provision, but did not act with willful neglect.
- Willful neglect: a "conscious, intentional failure or reckless indifference to the obligation to comply."
The HIPAA civil penalties for each tier are in Table 2.
Criminal Penalties for HIPAA Violations
HIPAA criminal penalties apply to a person who knowingly obtains or discloses individually identifiable health information in violation of HIPAA. In 2005, DOJ's Office of Legal Counsel concluded that "knowingly" refers "only to knowledge of the facts that constitute the offense," not to knowing that the act broke HIPAA (11). Since the HITECH Act of 2009, the statute names "an employee or other individual" among those who can unlawfully obtain or disclose a covered entity's information (3).
The statute sets three levels, each with a maximum and no minimum (3):
- Knowing violation: a fine of up to $50,000, up to 1 year in prison, or both.
- False pretenses: a fine of up to $100,000, up to 5 years in prison, or both.
- Intent to sell or harm: a fine of up to $250,000, up to 10 years in prison, or both, when the person intends to sell, transfer, or use the information for commercial advantage, personal gain, or malicious harm.
Table 1 sums up the three levels.
Table 1. HIPAA criminal penalty levels (42 U.S.C. 1320d-6)
| Level | Condition | Maximum fine | Maximum prison term |
|---|---|---|---|
| 1 | Knowingly obtaining or disclosing in violation of HIPAA | $50,000 | 1 year |
| 2 | Committed under false pretenses | $100,000 | 5 years |
| 3 | Intent to sell, transfer, or use for commercial advantage, personal gain, or malicious harm | $250,000 | 10 years |
Source: 42 U.S.C. 1320d-6(b) (3); read October 2026.
The Office of Legal Counsel noted that people outside the direct reach of section 1320d-6 can still be charged as aiders and abettors, whom federal law punishes "as a principal" (11, 12). Conspiracy carries up to five years in prison, or no more than the offense's own maximum when that offense is a misdemeanor (13).
How Much Is a HIPAA Violation?
Per violation, a civil money penalty runs from $145 to $2,190,294, depending on the tier OCR assigns under the 45 CFR 102.3 table in force since 28 January 2026 (2). When a case ends in a settlement instead, the resolution agreement sets any payment (8).
What Are the Fines for HIPAA Violations?
Table 2 sets out the four HIPAA penalty tiers and the HIPAA fines per violation in each (2).
Table 2. HIPAA civil penalty tiers in force since 28 January 2026
| Tier | Culpability | Minimum per violation | Maximum per violation | Calendar-year cap |
|---|---|---|---|---|
| 1 | Did not know | $145 | $73,011 | $2,190,294 |
| 2 | Reasonable cause | $1,461 | $73,011 | $2,190,294 |
| 3 | Corrected willful neglect (within 30 days) | $14,602 | $73,011 | $2,190,294 |
| 4 | Uncorrected willful neglect | $73,011 | $2,190,294 | $2,190,294 |
Source: the 45 CFR 102.3 penalty table, as amended on 28 January 2026 (1, 2); read October 2026.
Note. HHS's 2019 enforcement discretion sets lower yearly caps for tiers 1 to 3 (14); see "What Is the Maximum Penalty for a HIPAA Violation?"
Each tier has its own test:
- Did not know (Tier 1): the organization was unaware of the violation and, exercising reasonable diligence, would not have known. The range is $145 to $73,011 per violation, and OCR can still use corrective action without any penalty in this tier (6).
- Reasonable cause (Tier 2): the organization knew, or with reasonable diligence would have known, that the act or omission violated a provision, but it did not act with willful neglect (10). Penalties run from $1,461 to $73,011 per violation. OCR placed each of the three Warby Parker violations in this tier in its 2024 notice (15).
- Corrected willful neglect (Tier 3): a conscious failure or reckless indifference to the obligation, corrected within 30 days of when the organization knew or should have known of it (10). Here the minimum rises to $14,602, with the same $73,011 maximum.
- Uncorrected willful neglect (Tier 4): the same neglect, not corrected in that 30-day period. The minimum is $73,011, and one violation can reach $2,190,294. The statute requires a penalty for willful neglect and a formal investigation of a complaint that points to it (6).
HHS has not amended the table since 28 January 2026, as of October 2026 (2).
What Does a HIPAA Violation Cost Besides the Penalty?
Besides the payment, the cost of a HIPAA violation includes the obligations a resolution agreement imposes: the organization performs them and reports to HHS, generally for three years, while HHS monitors compliance (8). The settlements OCR announced in 2026 with Ambry Genetics, MMG Fusion, OSF Healthcare System, and Regional Women's Health Group carry corrective action plans of two or three years (16, 17, 18, 19). Under the OSF agreement, each party also bears its own legal and other costs.
A breach adds notice duties toward individuals, HHS, and in larger breaches the media (20, 21, 22). A state attorney general can also sue on behalf of residents (6).
What Is the Maximum Penalty for a HIPAA Violation?
There are two yearly caps: the legal calendar-year cap of $2,190,294 in Table 2, the same for every tier under 45 CFR 102.3 (2), and the lower caps HHS set for tiers 1 to 3 by enforcement discretion in 2019 (14).
Per violation, the ceiling is $73,011 in the first three tiers and $2,190,294 in the fourth, in the 45 CFR 102.3 table in force since 28 January 2026 (2). The regulation's text still prints the older base amounts: a $1,500,000 yearly cap for every tier, and $50,000 per violation, the maximum in the first three tiers and the minimum in the fourth (4).
The maximum HIPAA fine in a year can be lower in those tiers. In a 2019 Notification of Enforcement Discretion, HHS set one annual limit per tier, applied "as adjusted for inflation" until further notice. The base amounts it set in 2019 are (14):
- Did not know: $25,000 a year.
- Reasonable cause: $100,000 a year.
- Corrected willful neglect: $250,000 a year.
- Uncorrected willful neglect: $1,500,000 a year, the same base as the regulation's own cap, so the fourth tier is not lowered.
The 2019 caps work in practice, though they are not law:
- Legal weight: the notification "creates no legal obligations and no legal rights" (14), yet OCR applied its per-tier caps in its 2024 penalty notices to Warby Parker and Oregon Health & Science University (15, 23). Both notices capped reasonable cause at $100,000 a year, the 2019 base amount itself; the 102.3 table has no inflation-adjusted version of these limits.
- Counting: HHS counts violations by the nature of the obligation the provision sets, and a continuing violation is a separate violation for each day it lasts (24).
- Time limit: OCR has six years from the violation to start a penalty action (25).
The Warby Parker notice shows how the caps cut a daily count. OCR counted the missing risk analysis at $1,424 a day from 3 October 2018 to 1 October 2024 (15), the tier 2 minimum in the 2024 table then in force; it has since been raised to $1,461 (2). Table 3 shows the result.
Table 3. How the yearly caps reduced the Warby Parker penalty
| Violation | Total before caps | After yearly caps |
|---|---|---|
| No accurate and thorough risk analysis | $3,119,984 | $700,000 |
| Security measures insufficient to reduce risks | $1,987,904 | $500,000 |
| No regular review of information system activity | $837,312 | $300,000 |
| Total | $5,945,200 | $1,500,000 |
Source: OCR Notice of Proposed Determination, Warby Parker, Inc., 5 September 2024 (15).
HIPAA Penalties for Non-Compliance: How OCR Decides the Outcome
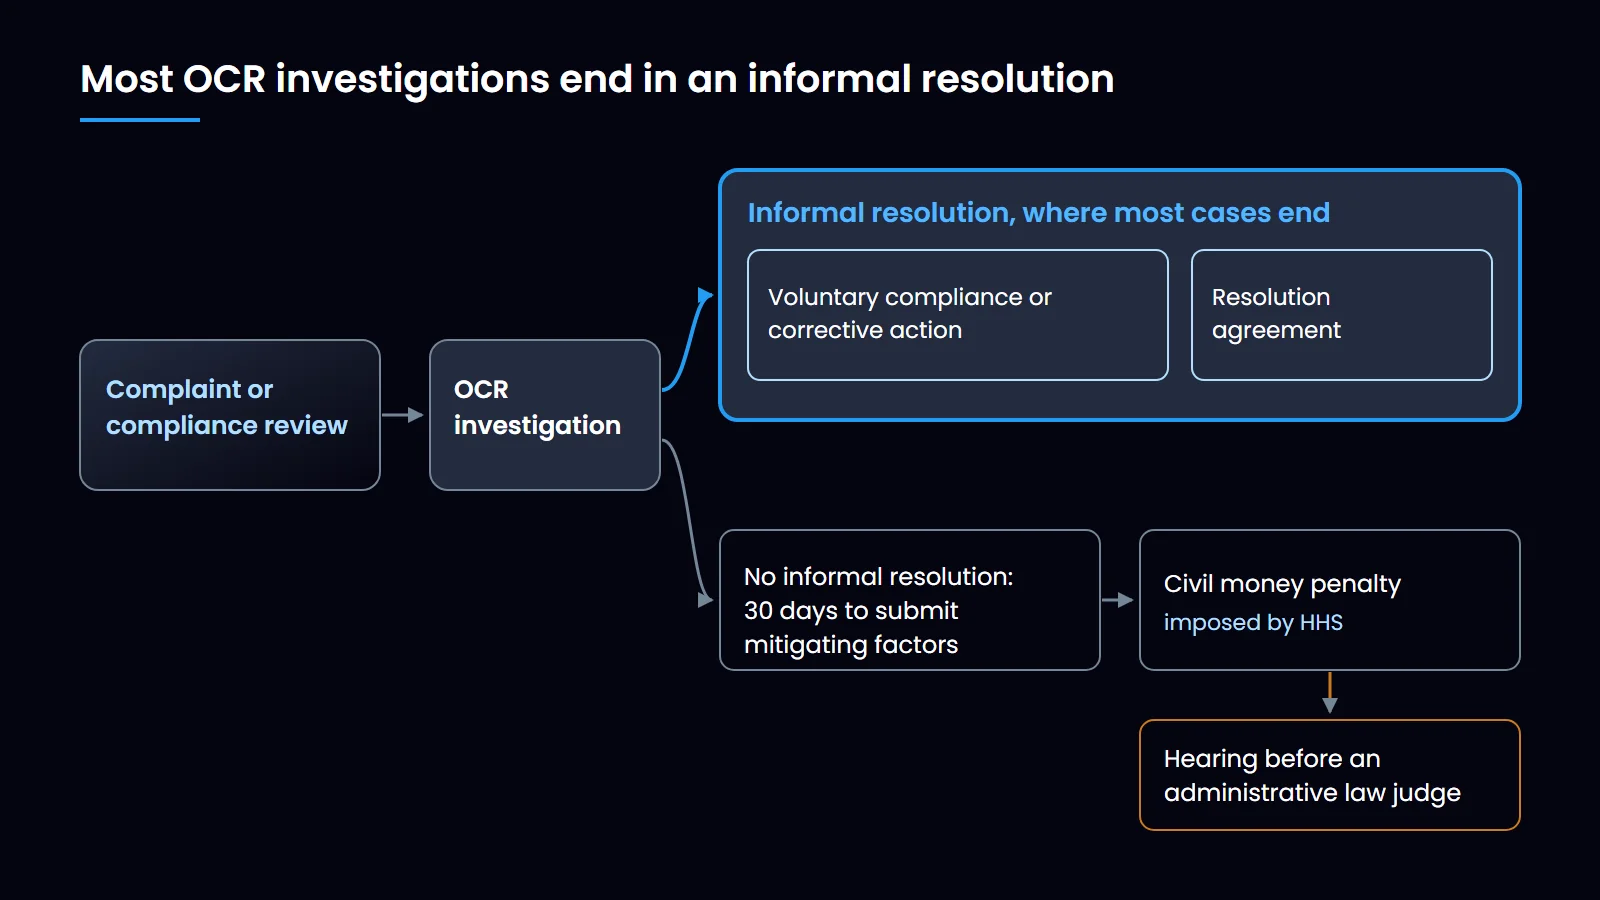
The HIPAA Enforcement Rule governs penalties for violating HIPAA regulations, from investigations to civil money penalties and hearings (5). OCR investigates complaints and conducts compliance reviews (26), and it must review a case where the facts point to possible willful neglect (27). Most investigations close through an informal resolution (9), and penalties for non-compliance with HIPAA come when none is reached (8). Figure 2 shows the path.
Types of Penalties for HIPAA Non-Compliance
HIPAA penalties and sanctions can include these outcomes, from mildest to most severe:
- Voluntary compliance or corrective action: demonstrated compliance or a completed corrective action plan closes the matter (28). HHS may also give technical assistance where an organization failed to comply because it was unable to (6).
- Resolution agreement: a settlement in which the organization agrees to obligations and reports to HHS, generally for three years (8), and which may include a payment. It is the last of the informal outcomes.
- Civil money penalty: HHS may impose these HIPAA non-compliance penalties when no satisfactory informal resolution is reached, after the organization has had 30 days to submit mitigating factors (28), and the organization can request a hearing before an administrative law judge (9). Their amounts are the HIPAA non-compliance fines in Table 2.
- Criminal referral or state action: OCR may refer a possible criminal violation to DOJ (9), and a state attorney general can sue in federal court (6).
Factors That Decide the Penalty Amount
Within a tier, HHS weighs five factors, each of which can lower or raise the amount (29):
- Nature and extent of the violation: the number of individuals affected and how long the violation lasted.
- Harm: physical, financial, or reputational harm, and whether the violation hindered access to health care.
- History of prior compliance: earlier non-compliance and the response to technical assistance and complaints.
- Financial condition: financial difficulties that affected compliance, and the organization's size.
- Other matters as justice may require.
When MMG Fusion paid $10,000 to settle in March 2026, OCR said, "In reaching this settlement, OCR considered the financial condition of MMG" (17). HHS may also waive a penalty in whole or in part for a violation that was not due to willful neglect and was not corrected within the 30 days or any longer period HHS allowed, when paying it would be excessive relative to the violation (30, 31).
The 30-Day Correction Window
HHS may not impose a civil money penalty for a violation that was not due to willful neglect and was corrected within 30 days, if the organization establishes both to HHS's satisfaction. The 30 days start on the first date the organization knew of the violation or would have known with reasonable diligence, and HHS can allow a longer period.
In the Oregon Health & Science University (OHSU) right-of-access case, OCR sent OHSU a technical-assistance letter on 2 September 2020 (23). OHSU did not correct the violation within 30 days, so OCR counted the violation from the 31st day after that letter and found that the 30-day defense did not apply. The university did not provide all the requested records until August 2021 (32). Its civil money penalty was $200,000, announced in March 2025.
Recognized Security Practices
Since an amendment to the HITECH Act in January 2021, HHS must consider recognized security practices an organization had in place for at least the previous 12 months when it sets fines and settlement remedies (33). The statute gives HHS no authority to increase a fine because these practices are missing. On 12 January 2024, OCR gave Warby Parker the opportunity to demonstrate its practices and then applied no reduction (15).
HIPAA Breach Penalties and Notification Deadlines
A breach can lead to penalties through the failures an investigation finds behind it and through late or missing notice, which OCR can cite as a violation of its own. After a breach of unsecured protected health information (PHI), the Breach Notification Rule sets four deadlines (20):
- Individuals: a covered entity notifies them without unreasonable delay and no later than 60 calendar days after discovery.
- Media: for a breach involving more than 500 residents of a state or jurisdiction, the covered entity notifies prominent media outlets serving that area (21).
- HHS: for 500 or more individuals, notice goes to HHS at the same time as the notice to individuals; smaller breaches go into a log due within 60 days after the end of the calendar year (22).
- Business associates: a business associate tells the covered entity no later than 60 calendar days after discovering a breach (34).
The organization carries the burden of showing that every notice was made (35).
How a Breach Turns Into a Penalty
"Hacking and ransomware are the most frequent type of large breach reported to OCR," OCR Director Paula M. Stannard said on 23 April 2026 (19). OCR investigates all breaches that affect 500 or more individuals (36), and violating HIPAA can result in findings beyond the breach itself:
- Missing risk analysis: in each of the four ransomware settlements announced that day, OCR found that the organization had not conducted an accurate and thorough risk analysis; the four paid a total of $1,165,000.
- Late notice: the covered conduct in OSF Healthcare System's 2026 agreement includes late notice to affected individuals and to HHS (18).
HIPAA breach fines, when OCR imposes a civil money penalty rather than settling, come from the tiers in Table 2 (2).
Recent OCR Settlements and Penalties: Cases Resolved From 2024 to 2026
OCR closed the six cases below from 2024 to 2026, each over violations that began in earlier years. HIPAA fines and penalties in the strict sense, meaning civil money penalties, appear once among them, for Warby Parker (37); the other five are settlements. A settlement records a payment, and the OSF and Montefiore agreements state that they are not an admission of liability (18, 38). For scale, HHS called Anthem's $16 million settlement in 2018 a "record HIPAA settlement" (39), and no larger amount has appeared in OCR's announcements since, as of October 2026 (8).
A civil money penalty can also be overturned: in 2021 the Fifth Circuit vacated a $4,348,000 penalty against M.D. Anderson as "arbitrary, capricious, and contrary to law" (40). Enforcement totals across all cases are collected in the cybersecurity compliance statistics for 2026.
Ambry Genetics: $700,000 Settlement After a Phishing Attack
In January 2020, Ambry Genetics, a genetic testing company, discovered that a phishing attack had compromised an employee's email account (16), and the PHI of 225,370 individuals was potentially exfiltrated. OCR's release lists potential Security Rule violations: no accurate and thorough risk analysis, no procedures to end access to electronic PHI (ePHI) when a workforce member leaves, and no unique user identification. Ambry paid $700,000 in September 2026 under a corrective action plan that OCR will monitor for two years.
OSF Healthcare System: $552,250 Settlement Including Late Breach Notice
OSF discovered ransomware on its systems on 23 April 2021, determined on 24 August 2021 that attackers had stolen the PHI of 53,907 patients, and notified the patients and HHS on 1 October 2021 (18). The covered conduct in the resolution agreement includes a failure to meet the risk analysis requirement and late notice to individuals and to HHS. OSF paid $552,250 under a two-year corrective action plan.
Regional Women's Health Group: $320,000 Settlement After Ransomware
Regional Women's Health Group, which does business as Axia Women's Health, reported in December 2020 that an unauthorized third party had gained access to its network (19). The ransomware breach affected 37,989 individuals, and OCR's investigation found that the group had not conducted an accurate and thorough risk analysis. It paid $320,000 as one of the four ransomware settlements OCR announced on 23 April 2026 (its agreement is dated 28 August 2025 on OCR's list), each with two years of OCR monitoring (8).
MMG Fusion: $10,000 Settlement for a Business Associate
MMG Fusion, a software company acting as a business associate, came under investigation in March 2023 after a complaint about an unreported security incident and PHI posted on the dark web (17). OCR's release lists potential violations including the impermissible disclosure of the PHI of approximately 15 million individuals, no risk analysis, and no breach notice to the covered entities affected. MMG paid $10,000 under a corrective action plan that OCR will monitor for three years.
Warby Parker: $1,500,000 Civil Money Penalty for Three Security Rule Violations
Between 25 September and 30 November 2018, unauthorized third parties entered Warby Parker customer accounts using usernames and passwords obtained from other websites (37), and the company later put the number affected at 197,986. OCR found evidence of three Security Rule violations: no accurate and thorough risk analysis, security measures insufficient to reduce risks to a reasonable and appropriate level, and no regular review of information system activity. Warby Parker waived its right to a hearing, and OCR imposed a $1,500,000 civil money penalty in December 2024.
Montefiore Medical Center: $4,750,000 Settlement After a Malicious Insider
From January to June 2013, a Montefiore employee accessed the records of 12,517 patients and sold patient information to an identity theft ring (38). The resolution agreement lists potential violations of the risk analysis, information system activity review, and audit control requirements. Montefiore paid $4,750,000 under a two-year corrective action plan, and OCR listed the settlement in February 2024 as a malicious insider investigation.
HIPAA Violation Consequences: Monitoring, Lawsuits, and Employees
HIPAA violations can result in consequences that outlast the payment: years of reporting to HHS, lawsuits by state attorneys general, and sanctions for the people involved. For consequences under other regulations, see the consequences of non-compliance.
What Are the Consequences of Violating HIPAA for an Organization?
Two consequences for HIPAA violations reach past the payment:
- Monitoring: HHS monitors compliance with a resolution agreement and the reports it requires, generally over three years (8). Ambry's corrective action plan, for example, commits it to a new risk analysis, a risk management plan, revised Security Rule policies, unique user identification, and workforce training (16).
- State lawsuits: a state attorney general can sue in federal court on behalf of residents (6), for damages of up to $100 per violation and at most $25,000 a calendar year for identical violations, and the court may award costs and attorney fees. The state must give HHS prior written notice where that is feasible.
Civil money penalties are deposited in the U.S. Treasury, and complainants receive no portion of them (9).
What Happens if You Violate HIPAA as an Employee?
An employee who violates HIPAA faces the employer's sanctions; OCR's civil money penalties are imposed on the organization, and criminal charges require knowing conduct. Three provisions set this out:
- Employer sanctions: a covered entity must have and apply appropriate sanctions against workforce members who fail to comply with its privacy policies, and document them (41); the Security Rule requires a sanction policy as well (42).
- Civil penalties: OCR's civil money penalties are imposed on covered entities and business associates (7), and the covered entity is liable for violations by its workforce members acting within the scope of the agency.
- Criminal liability: the statute covers "an employee or other individual" who obtains or discloses a covered entity's information without authorization (3), when the person acts knowingly.
An accidental slip, such as handing a patient another patient's discharge papers, falls under the employer's sanctions policy. HHS may not impose a civil money penalty for it if the organization shows that the violation was not due to willful neglect and was corrected within 30 days (31). The disclosure may still be a breach that needs notice, unless a risk assessment shows a low probability that the information was compromised (43).
Can Patients Sue for a HIPAA Violation?
A federal appeals court has held that HIPAA gives patients no right to sue. In Acara v. Banks (2006), the Fifth Circuit held that "there is no private cause of action under HIPAA" (44).
A state attorney general can sue to obtain monetary damages for a HIPAA violation on behalf of the state's residents (as parens patriae), within the limits listed above. The HITECH Act told HHS to create a way for harmed individuals to receive a percentage of penalties or settlements. OCR asked for public comment on it in April 2022 (45), and the Federal Register lists no later document in that rulemaking as of October 2026 (46).
How to Reduce the Risk of an OCR Penalty
Lowering HIPAA fines for non-compliance starts with the failures OCR named in the cases above, and the steps below address them:
- Run an accurate and thorough risk analysis. The Security Rule requires one (42), and OCR cited the risk analysis requirement in each of the six cases above (16, 17, 18, 19, 37, 38). CyberCrest's cybersecurity risk assessment services cover this analysis. The five common HIPAA Security Rule deficiencies start with an incomplete risk analysis.
- Document recognized security practices for 12 months. HHS must consider them when it sets fines and settlement remedies (33), so documentation kept over the previous 12 months is worth having before OCR asks.
- Rehearse the breach notice clocks. A covered entity must notify individuals no later than 60 calendar days after discovery, and HHS at the same time for a breach of 500 or more (20, 22).
- Fix and document within 30 days. Under 45 CFR 160.410, a violation that is corrected within 30 days and was not due to willful neglect draws no civil money penalty when the organization can show both (31).
OCR proposed stricter Security Rule requirements in a notice published on 6 January 2025, including a more specific risk analysis (47); the Federal Register lists no final rule as of October 2026, so they are not yet requirements (48).
Find Your HIPAA Gaps Before OCR Does
Our HIPAA compliance services are four offerings, bought alone or together: HIPAA Risk Analysis and Gap Assessment, Remediation of Identified Gaps, HIPAA Evaluation and Attestation, and Ongoing HIPAA Compliance Support. We assess the risks to your ePHI and name the gaps, specify what each fix must achieve while your team implements it, and review the result against the Security Rule. Talk to an expert before OCR's first data request arrives.
Sources
- HHS, Annual Civil Monetary Penalties Inflation Adjustment, 91 FR 3665, 28 January 2026. https://www.federalregister.gov/documents/2026/01/28/2026-01688/annual-civil-monetary-penalties-inflation-adjustment
- eCFR, 45 CFR 102.3, Penalty adjustment and table (the regulation's civil monetary penalty adjustment table), as amended on 28 January 2026. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-A/part-102/section-102.3
- U.S. Code, 42 U.S.C. 1320d-6, Wrongful disclosure of individually identifiable health information. https://www.govinfo.gov/content/pkg/USCODE-2024-title42/html/USCODE-2024-title42-chap7-subchapXI-partC-sec1320d-6.htm
- eCFR, 45 CFR 160.404, Amount of a civil money penalty. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.404
- HHS Office for Civil Rights, The HIPAA Enforcement Rule. https://www.hhs.gov/hipaa/for-professionals/special-topics/enforcement-rule/index.html
- U.S. Code, 42 U.S.C. 1320d-5, General penalty for failure to comply with requirements and standards. https://www.govinfo.gov/content/pkg/USCODE-2024-title42/html/USCODE-2024-title42-chap7-subchapXI-partC-sec1320d-5.htm
- eCFR, 45 CFR 160.402, Basis for a civil money penalty. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.402
- HHS Office for Civil Rights, Resolution Agreements and Civil Money Penalties. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/agreements/index.html
- HHS Office for Civil Rights, How OCR Enforces the HIPAA Privacy & Security Rules. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/examples/how-ocr-enforces-the-hipaa-privacy-and-security-rules/index.html
- eCFR, 45 CFR 160.401, Definitions (reasonable cause, reasonable diligence, willful neglect). https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.401
- U.S. Department of Justice, Office of Legal Counsel, Scope of Criminal Enforcement Under 42 U.S.C. 1320d-6, 1 June 2005. https://www.justice.gov/olc/opinion/scope-criminal-enforcement-under-42-usc-1320d-6
- U.S. Code, 18 U.S.C. 2, Principals. https://www.govinfo.gov/content/pkg/USCODE-2023-title18/html/USCODE-2023-title18-partI-chap1-sec2.htm
- U.S. Code, 18 U.S.C. 371, Conspiracy to commit offense or to defraud United States. https://www.govinfo.gov/content/pkg/USCODE-2024-title18/pdf/USCODE-2024-title18-partI-chap19-sec371.pdf
- HHS, Notification of Enforcement Discretion Regarding HIPAA Civil Money Penalties, 84 FR 18151, 30 April 2019. https://www.federalregister.gov/documents/2019/04/30/2019-08530/notification-of-enforcement-discretion-regarding-hipaa-civil-money-penalties
- HHS Office for Civil Rights, Notice of Proposed Determination, Warby Parker, Inc., 5 September 2024. https://www.hhs.gov/sites/default/files/ocr-warby-parker-npd.pdf
- HHS, HHS' Office for Civil Rights Settles HIPAA Investigation of Ambry Genetics Phishing Attack Affecting 225,000 Individuals, 17 September 2026. https://www.hhs.gov/press-room/hhs-office-civil-rights-settles-hipaa-investigation-ambry-genetics-phishing-attack-affecting-225000-individuals.html
- HHS, HHS' Office for Civil Rights Settles HIPAA Investigation of MMG Fusion, LLC Breach Affecting 15 Million Individuals, 5 March 2026. https://www.hhs.gov/press-room/ocr-mmg-fusion-hipaa-agreement.html
- HHS Office for Civil Rights, OSF Healthcare System Resolution Agreement and Corrective Action Plan. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/agreements/ra-cap-with-osf-healthcare-system/index.html
- HHS, HHS' Office for Civil Rights Settles Four HIPAA Security Rule Ransomware Investigations, 23 April 2026. https://www.hhs.gov/press-room/ocr-settles-four-ransomware-investigations.html
- eCFR, 45 CFR 164.404, Notification to individuals. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.404
- eCFR, 45 CFR 164.406, Notification to the media. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.406
- eCFR, 45 CFR 164.408, Notification to the Secretary. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.408
- HHS Office for Civil Rights, Notice of Proposed Determination, Oregon Health & Science University, 9 September 2024. https://www.hhs.gov/sites/default/files/oregon-health-science-university-npd.pdf
- eCFR, 45 CFR 160.406, Violations of an identical requirement or prohibition. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.406
- eCFR, 45 CFR 160.414, Limitations. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.414
- HHS Office for Civil Rights, Enforcement Process. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/enforcement-process/index.html
- eCFR, 45 CFR 160.308, Compliance reviews. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-C/section-160.308
- eCFR, 45 CFR 160.312, Secretarial action regarding complaints and compliance reviews. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-C/section-160.312
- eCFR, 45 CFR 160.408, Factors considered in determining the amount of a civil money penalty. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.408
- eCFR, 45 CFR 160.412, Waiver. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.412
- eCFR, 45 CFR 160.410, Affirmative defenses. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.410
- HHS, HHS Office for Civil Rights Imposes a $200,000 Penalty Against Oregon Health & Science University for Failure to Provide Timely Access to Patient Records, 6 March 2025. https://www.hhs.gov/press-room/penalty-against-or-health-science-university.html
- U.S. Code, 42 U.S.C. 17941, Recognition of security practices. https://www.govinfo.gov/content/pkg/USCODE-2024-title42/html/USCODE-2024-title42-chap156-subchapIII-partA-sec17941.htm
- eCFR, 45 CFR 164.410, Notification by a business associate. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.410
- eCFR, 45 CFR 164.414, Administrative requirements and burden of proof. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.414
- HHS Office for Civil Rights, Breach Portal. https://ocrportal.hhs.gov/ocr/breach/breach_frontpage.jsf
- HHS, HHS Office for Civil Rights Imposes a $1,500,000 Civil Money Penalty Against Warby Parker in HIPAA Cybersecurity Hacking Investigation, 20 February 2025. https://www.hhs.gov/press-room/penalty-against-warby-parker.html
- HHS Office for Civil Rights, Voluntary Resolution Agreement with Montefiore Medical Center. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/agreements/montiefore/index.html
- HHS Office for Civil Rights, Anthem pays OCR $16 Million in record HIPAA settlement following largest health data breach in history, 15 October 2018. https://www.hhs.gov/hipaa/for-professionals/compliance-enforcement/agreements/anthem/index.html
- U.S. Court of Appeals for the Fifth Circuit, University of Texas M.D. Anderson Cancer Center v. HHS, No. 19-60226, 14 January 2021. https://www.ca5.uscourts.gov/opinions/pub/19/19-60226-CV0.pdf
- eCFR, 45 CFR 164.530, Administrative requirements. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-E/section-164.530
- eCFR, 45 CFR 164.308, Administrative safeguards. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-C/section-164.308
- eCFR, 45 CFR 164.402, Definitions (breach). https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.402
- U.S. Court of Appeals for the Fifth Circuit, Acara v. Banks, No. 06-30356, 13 November 2006. https://www.ca5.uscourts.gov/opinions/pub/06/06-30356-CV0.wpd.pdf
- HHS Office for Civil Rights, Considerations for Implementing the HITECH Act, as Amended (request for information), 87 FR 19833, 6 April 2022. https://www.federalregister.gov/documents/2022/04/06/2022-07210/considerations-for-implementing-the-health-information-technology-for-economic-and-clinical-health
- Federal Register, documents under RIN 0945-AA04, Distribution of a Percentage of Civil Money Penalties or Monetary Settlements to Harmed Individuals (read 15 October 2026). https://www.federalregister.gov/api/v1/documents.json?conditions%5Bregulation_id_number%5D=0945-AA04
- HHS Office for Civil Rights, HIPAA Security Rule To Strengthen the Cybersecurity of Electronic Protected Health Information (proposed rule), 90 FR 898, 6 January 2025. https://www.federalregister.gov/documents/2025/01/06/2024-30983/hipaa-security-rule-to-strengthen-the-cybersecurity-of-electronic-protected-health-information
- Federal Register, documents under RIN 0945-AA22, Proposed Modifications to the HIPAA Security Rule (read 15 October 2026). https://www.federalregister.gov/api/v1/documents.json?conditions%5Bregulation_id_number%5D=0945-AA22
- U.S. Code, 18 U.S.C. 3559, Sentencing classification of offenses. https://www.govinfo.gov/content/pkg/USCODE-2024-title18/html/USCODE-2024-title18-partII-chap227-subchapA-sec3559.htm




FAQ
What are the penalties for HIPAA violations?

Civil money penalties run from $145 to $73,011 per violation in the first three tiers and from $73,011 to $2,190,294 for willful neglect not corrected within 30 days, under the 45 CFR 102.3 table as amended on 28 January 2026 (1, 2). Criminal penalties reach a $250,000 fine and 10 years in prison (3). A settlement instead of a penalty can carry a payment and years of reporting to HHS (8).
What is the fine for a HIPAA violation?
It depends on culpability. In the penalty table HHS amended in January 2026 (45 CFR 102.3), the minimum is $145 per violation when the organization did not know and could not have known, and $73,011 when willful neglect was not corrected within 30 days (1, 2). Each civil penalty is set per violation, and a continuing violation counts once for each day (24).
Are HIPAA violations criminal?
Some are. OCR resolves most investigations as civil matters, through voluntary compliance, corrective action, or a resolution agreement (9). Under 42 U.S.C. 1320d-6, a violation becomes a crime when a person knowingly obtains or discloses individually identifiable health information in violation of HIPAA (3). OCR may refer such a complaint to the Department of Justice.
Is violating HIPAA a felony?
It can be. Prison is possible when a person acts knowingly. The statute sets HIPAA violation jail time by level, at up to 1, 5, or 10 years (3). Federal law classifies an offense by its maximum prison term, so level 1 is a Class A misdemeanor, and levels 2 and 3 are Class D and Class C felonies (49). The punishment for a HIPAA violation at each level can be a fine, prison, or both.
What happens if HIPAA is violated?
A violation of HIPAA can result in an investigation that ends with the organization demonstrating compliance, a corrective action plan, a resolution agreement with a payment, or a civil money penalty (8, 28). When someone acted knowingly, OCR may refer the complaint to the Department of Justice (9).
What is the maximum penalty for violating HIPAA?
The civil maximum is $2,190,294 per violation, with a calendar-year cap of $2,190,294 for identical violations, in the current 45 CFR 102.3 table, amended on 28 January 2026 (1, 2). HHS's 2019 enforcement discretion sets lower yearly caps for the first three tiers (14). On the criminal side, the ceiling is $250,000 and 10 years (3).
What are the consequences of HIPAA violations?
An organization can face a settlement payment or a civil money penalty, plus reports to HHS under a resolution agreement, generally for three years (8). A state attorney general can also sue it (6). A workforce member can face sanctions by the employer (41) and, for a knowing violation, criminal prosecution (3).
What happens if you violate HIPAA accidentally?
If the violation was not due to willful neglect and the organization shows that it corrected it within 30 days of when it knew or should have known, HHS may not impose a civil money penalty (31). Where the organization did not know of the violation and could not have known with reasonable diligence, OCR can still use corrective action without a penalty (6). The employee involved faces the employer's sanctions policy (41); criminal liability requires knowing conduct (3).
Who enforces HIPAA?
OCR at HHS enforces the Privacy and Security Rules through complaint investigations, compliance reviews, and education and outreach (26). The Department of Justice handles criminal cases, which OCR may refer to it (9), and state attorneys general can bring civil actions in federal district court for state residents (6).
About the author
Arti Shala
—
ISO 27001:2022 Lead Auditor, HITRUST CCSFP & CHQP
Arti is an experienced cybersecurity and compliance professional with over five years of hands-on experience across IT, security, and GRC. He has worked with clients of all sizes — from startups to Fortune 500s—delivering solutions that improve security posture and ensure compliance.
He began his career supporting healthcare providers with managed IT and security services before transitioning to consulting, where he helps organizations identify risks and strengthen their security programs. Arti is especially skilled at bridging technical depth with executive communication.
His expertise spans risk assessments, compliance audits, and advisory across frameworks including HITRUST, HIPAA, NIST CSF, NIST 800-53, FedRAMP, and ISO 27001. With a focus on healthcare and a strong understanding of cloud, hybrid networks, and DevOps, Arti delivers value to organizations navigating today’s evolving threat landscape.