The Real Consequences of Non-Compliance: Risks, Fines & Examples
Published on
June 24, 2025
/
updated on
October 19, 2026

Non-compliance can cost a company regulatory fines, legal action that may reach officers and employees personally, lost contracts and contract eligibility, years of corrective work under a regulator's eye, failed audits, and reputational and operational damage. In the recent HIPAA cases, two of these consequences of non-compliance arrived together: a penalty and a remediation plan the regulator monitors. For government contractors, the contract itself is also at stake.
The stakes rose fast for anyone who sells to the government. The Department of Justice recovered "over $52 million in nine cybersecurity fraud settlements" in fiscal year 2025, and civil cybersecurity fraud settlements "have more than tripled in each of the past two years" (1). HHS kept settling HIPAA breach investigations through 2026 (2, 3), and the €1.2 billion GDPR fine against Meta Ireland shows how high privacy penalties can go (4).
This guide is for the people who have to explain that exposure to leadership: compliance and security leads at SaaS companies, healthcare organizations and their business associates, defense contractors, merchants that take card payments, and public companies.
What Is Regulatory Non-Compliance?
An organization is out of regulatory compliance when it fails a requirement set by laws and regulations and enforced by regulatory bodies. For HIPAA that body is the Office for Civil Rights (OCR) at the Department of Health and Human Services (HHS); for the GDPR, a data protection authority; for contract cybersecurity clauses, the Department of Defense. Internal policies are a governance matter. Regulatory requirements are a legal one: compliance obligations with a named enforcer and penalties set in statute.
Recent enforcement cases turn on three kinds of gap, each admitted by the company, alleged by the United States, or found by OCR:
- A self-assessment score the systems did not support, as in the MORSECORP case below (5).
- A system security plan that, the United States alleged, did not exist at Raytheon or, until at least February 2020, at a Georgia Tech lab (6, 7).
- A risk analysis that OCR found was not accurate and thorough, in its 2026 HIPAA settlements (2, 8).
In three of the False Claims Act cases below, the government also pointed to a score or a certification the company had submitted.
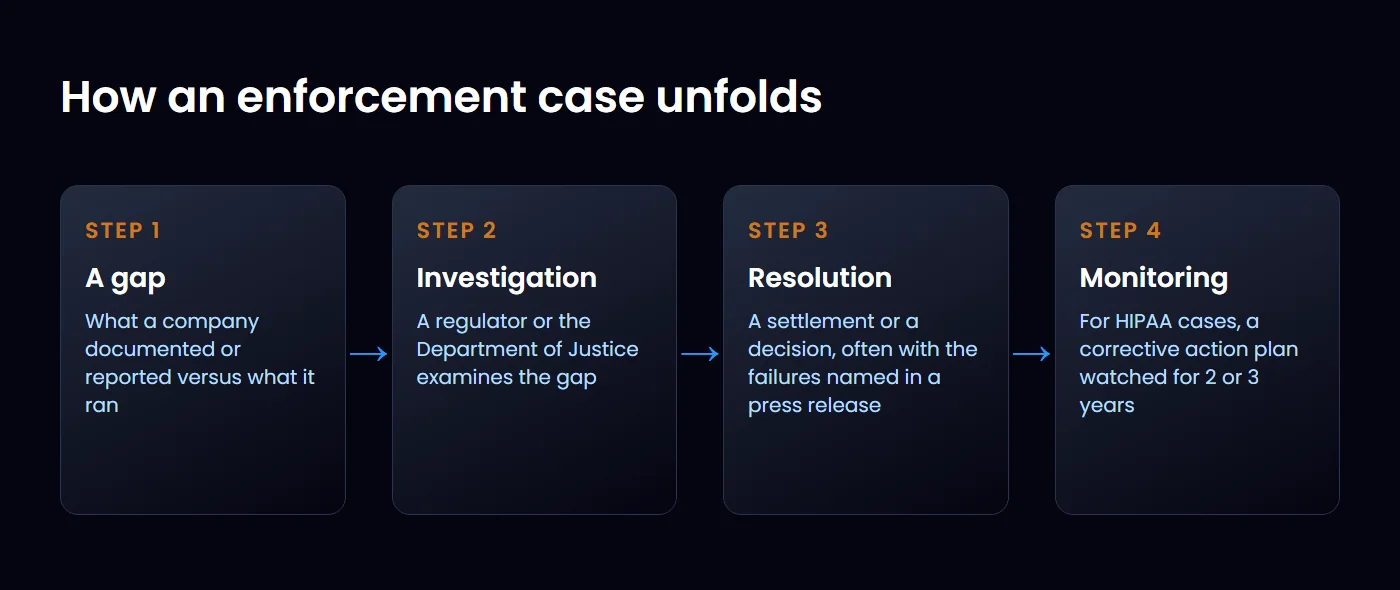
A gap like these becomes an enforcement case in the four steps of Figure 1, which in the HIPAA cases end with a corrective action plan monitored for two or three years (2, 3).
Adapted from: HHS Office for Civil Rights releases.
Types of Non-Compliance
Non-compliance occurs in four kinds of situation, and the consequences differ with each.
- Regulatory: A law or regulation is broken: HIPAA, the GDPR, the CCPA, OSHA rules. A government agency investigates and penalties are set in statute.
- Contractual: A clause the company signed is broken: a Department of Defense cybersecurity clause, a HIPAA business associate agreement, the card-brand rules for accepting payment cards. Where a Department of Defense solicitation sets a CMMC level, the clause decides whether the contract can be awarded (9).
- Standards-based: A framework the company chose, or its customers demanded, is not met: a SOC 2 examination with exceptions, a lapsed ISO 27001 certificate. Missing a voluntary or customer-required standard does not by itself bring a regulatory fine, but it can affect contract commitments, procurement eligibility and customer trust.
- Internal policy: The company's own rules are not followed. On its own this is a governance problem, but it is usually how the other three start.
What Are Some of the Consequences for Non-Compliance?
The cases below sort into seven groups of non-compliance consequences. Figure 2 shows all seven, numbered as in the sections that follow, and most cases combine several of them.

1. Financial Penalties and Fines
Civil money penalties are set per violation and scale with culpability, which is why the same failure can cost very different amounts.
- HIPAA: OCR applies four tiers, from a violation the organization "did not know" about to willful neglect that "was not corrected during the 30-day period" after the organization knew or should have known (10). The top tier reaches $2,190,294 a year for identical violations (11).
- GDPR: Fines reach €20 million or 4% of total worldwide annual turnover, whichever is higher, for the most serious infringements (12).
- CCPA: California's administrative fine is set per violation, with a higher amount for intentional violations and for violations involving consumers the business knows are under 16 (13).
Business impact: these figures are statutory maximums, and each regime counts them differently: HIPAA adds a yearly cap of $2,190,294 for identical violations (11), while GDPR fines can be based on worldwide annual turnover (12). What a company pays depends on the rules and the facts, and a settlement can be far lower, as the cases below show.
2. Legal Action and Criminal Liability
Some regimes reach people as well as companies, and some bring criminal charges.
- Officers: Under Section 906 of the Sarbanes-Oxley Act, an officer who certifies a periodic report "knowing that the periodic report accompanying the statement does not comport with all the requirements" faces personal criminal penalties; the amounts are in Table 1 (14).
- Anyone who misuses health information: HIPAA's criminal provision reaches employees and other individuals as well as the organization; its three penalty tiers are listed in the chapter on employees below (15).
- Companies: The legal consequences usually arrive as a civil action. One is a False Claims Act suit when the government paid for compliance it did not get, with penalties per false claim plus three times the government's damages (16). Another is a private lawsuit where a statute allows one, as the CCPA does after a data breach (13).
Business impact: an officer's exposure is personal, so certifications slow down while managers confirm each control, and any civil action brings counsel and discovery costs whatever the outcome.
3. Lost Contracts and Contract Eligibility
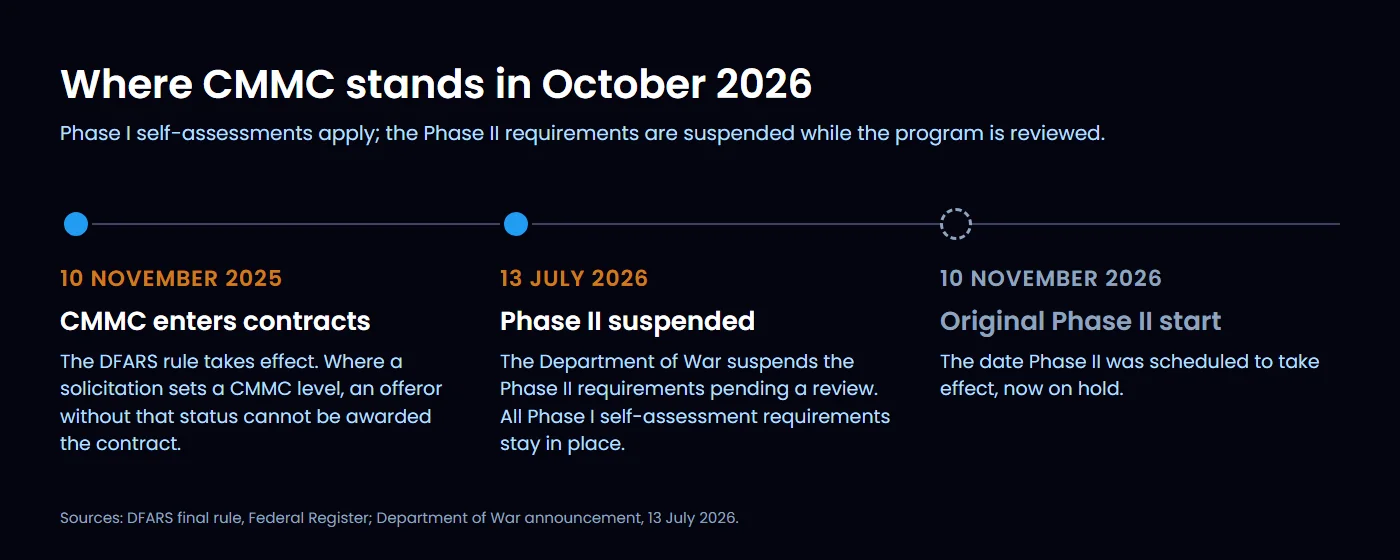
For defense contractors this can be the consequence that matters most. The DFARS rule that writes CMMC into contracts took effect on 10 November 2025 (17). Where a solicitation sets a CMMC level, contracting officers "shall not award" a contract "to an offeror that does not have a current CMMC status at the CMMC level required by the solicitation" (9). During the phase-in, the clause appears when the program office decides to apply a CMMC requirement (17).
The timeline moved in 2026. The Department of Defense now also uses the name Department of War, and on 13 July 2026 it announced "the immediate suspension" of the CMMC Phase II requirements, originally due to take effect on 10 November 2026. It said that "All Phase I self-assessment requirements remain firmly in place" while it reviews the program (18).
Figure 3 shows where CMMC stands in October 2026: the award rule applies, and Phase II is on hold (17, 18).
Adapted from: the DFARS final rule in the Federal Register and the Department of War announcement of 13 July 2026.
The suspension does not lift the duty to protect contract data: in the interim the Department said it "will enforce cybersecurity compliance with the NIST SP 800-171 Rev 2 standard through self-assessments and select government-led assessments," and contractors "remain contractually obligated to safeguard covered defense information in accordance with DFARS clause 252.204-7012" (18).
A CMMC compliance gap assessment shows which requirements a contractor still has to meet.
Federal acquisition rules also require disclosure and allow debarment:
- Mandatory disclosure: Federal contractors under FAR 52.203-13 "shall timely disclose, in writing," to the agency's Office of the Inspector General credible evidence of certain federal crimes or of "a violation of the civil False Claims Act" connected with the contract (19).
- Debarment: The Federal Acquisition Regulation lists "willful failure to perform in accordance with the terms of one or more contracts" among the causes for debarment (20).
Business impact: a contractor that cannot show the required status loses the bid before price is discussed, and a debarred one is "excluded from receiving contracts" (21) for the debarment period, which generally should not exceed three years (22).
4. Failed Audits and Lost Certifications
SOC 2 and ISO 27001 are not laws, so falling short of them does not by itself bring a regulatory fine; depending on the facts, the same gap can also breach a contract or a separate legal duty. The first consequence usually comes from customers, whose security teams read the result before they sign:
- A SOC 2 report with exceptions tells the buyer which controls did not work during the period.
- A qualified opinion tells the buyer the auditor could not give a clean result.
- A lapsed ISO 27001 certificate removes the proof many procurement teams require.
A weak result stalls or ends the deal. For a SaaS vendor, this consequence can arrive long before any regulator does. A SOC 2 compliance readiness assessment or an ISO 27001 certification gap review finds those gaps before the formal examination does.
Business impact: longer sales cycles, lost renewals, and a remediation project on the customer's timeline.
5. Corrective Action Under Regulatory Scrutiny
In the 2026 HIPAA settlements below, the payment was not the end. OCR monitors each corrective action plan for two or three years, and the MMG Fusion and Ambry plans share the same core items (2, 3, 8):
- conduct "an accurate and thorough risk analysis";
- implement a risk management plan for the risks it finds;
- revise written policies and procedures under the HIPAA Rules;
- train all workforce members on those policies and procedures.
A breach of unsecured protected health information also triggers a duty to notify each affected individual "without unreasonable delay and in no case later than 60 calendar days after discovery of a breach" (23).
Business impact: the company staffs every plan item itself while OCR monitors it, on top of fixing whatever caused the breach.
6. Reputational Damage
Enforcement is public. Regulators announce their settlements in press releases that name the organization, describe what failed and state what it paid, and those releases are what prospects find when they search the company. The damage reaches customers, partners, and employees:
- Customers run vendor reviews and ask harder questions at renewal.
- Partners in regulated industries reassess whether they can keep sharing data with you.
- Employees who learn about a failure from the news ask whether leadership knew.
Business impact: for a business that sells on trust, such as a SaaS vendor answering security questionnaires or a clinic asking patients for their records, the reputational risks and the financial losses that follow outlast the fine.
7. Operational Disruption
A regulator can change how you operate as well as what you pay. When the Irish Data Protection Commission fined Meta Ireland for EU-to-US data transfers, it also ordered the company "to suspend any future transfer of personal data to the US within the period of five months" (4). Corrective action plans, debarment, and lost certifications disrupt operations in the same way: teams rebuild processes on the regulator's timeline, not their own.
Business impact: projects stop while people are pulled into remediation, and a suspended data flow or a lost contract can stop a product line entirely.
Penalties for Non-Compliance by Regulation
What you pay as a penalty for non-compliance depends on the regulation, on the regulator's view of intent, and, for US federal penalties, on an annual inflation adjustment. Table 1 shows the current fines and penalties, what else each regime can trigger, and the date each amount took effect.
Table 1. Penalties for non-compliance by regulation
| Regulation | Enforced by | Maximum penalty | What else it can trigger | Amount in force since |
|---|---|---|---|---|
| HIPAA | HHS Office for Civil Rights | $145 to $73,011 per violation in the lower three tiers; $73,011 to $2,190,294 per violation for uncorrected willful neglect; $2,190,294 a year for identical violations (10, 11) | A monitored corrective action plan (2 or 3 years in the 2026 OCR cases below); breach notification; criminal penalties for individuals (2, 3, 15) | 2025 adjustment, published 28 January 2026 (24) |
| GDPR | EU and EEA data protection authorities | Up to €20 million or 4% of total worldwide annual turnover, whichever is higher; up to €10 million or 2% for the lower tier (12) | Orders to suspend processing or transfers (4) | Regulation (EU) 2016/679 |
| CCPA | California Privacy Protection Agency | Up to $2,663 per violation or $7,988 per intentional violation (13) | Data breach lawsuits with $107 to $799 per consumer per incident, or actual damages if greater (13) | 1 January 2025 |
| Sarbanes-Oxley, Section 906 | Department of Justice | Up to $1,000,000 and 10 years for a knowing false certification; up to $5,000,000 and 20 years if willful (14) | Personal criminal liability for the certifying officer | Statute |
| FTC Act | Federal Trade Commission | $53,088 per violation (25) | n/a | Penalties assessed after 17 January 2025; 2025 amounts, kept for 2026 (26) |
| OSHA | Occupational Safety and Health Administration | $11,823 to $165,514 per willful violation; up to $16,550 per serious violation (27) | Up to $16,550 a day for failing to correct; criminal penalties if a willful violation causes a death (27, 28) | Penalties proposed after 15 January 2025; 2025 amounts, kept for 2026 (29) |
| False Claims Act | Department of Justice | $14,308 to $28,619 per false claim, plus three times the government's damages (16) | Whistleblower suits; debarment (20, 30) | 2025 amounts, kept for 2026 (31) |
| PCI DSS | Each payment card brand | Not set by the PCI Security Standards Council (32) | Terms set by each card brand | n/a |
| SOC 2 and ISO 27001 | No regulator | No fine | A report with exceptions or a lost certificate; stalled deals | n/a |
Note. The PCI Security Standards Council states that any fines for non-compliance "are defined by each of the payment card brands" (32).
None of the federal agency amounts in Table 1 received a 2026 inflation adjustment. The Office of Management and Budget canceled the 2026 adjustment for all agencies because the October 2025 consumer price index was never published, and told agencies to keep using their 2025 amounts (29):
- HHS (HIPAA): its 2025 adjustment, published on 28 January 2026 before the cancellation, is still the current table; HHS has published no 2026 adjustment.
- Justice (False Claims Act) and the FTC: each published a 2026 notice keeping its 2025 levels.
- Labor (OSHA): its 2026 notice canceled the adjustment, so the amounts in force since January 2025 still apply.
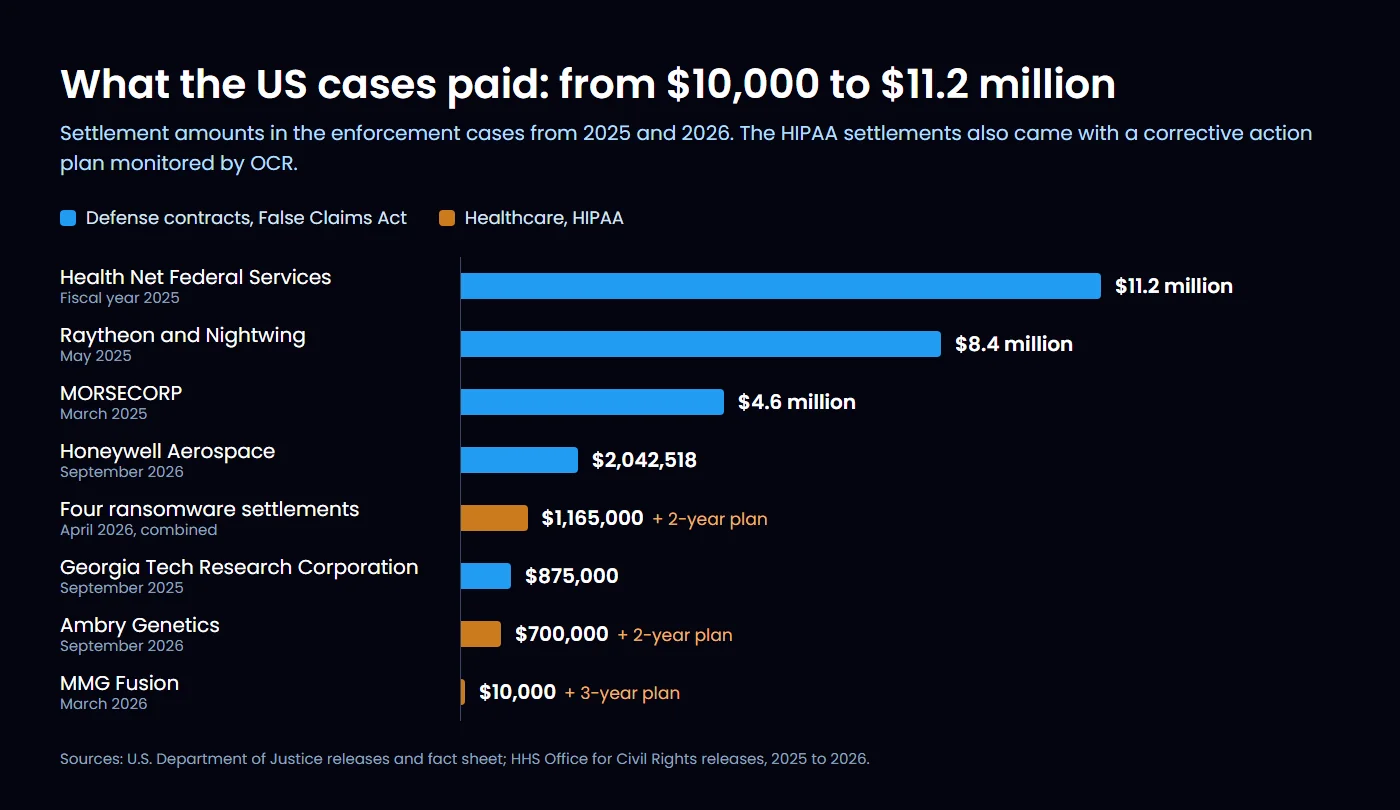
These amounts are ceilings. Actual settlements depend on the facts of each case and can reflect the organization's ability to pay, as MMG Fusion's did (2). Figure 4 shows what each US case below paid, from MMG Fusion's $10,000 to Health Net's $11.2 million (1, 2).
Adapted from: U.S. Department of Justice releases and its FY2025 False Claims Act fact sheet, and HHS Office for Civil Rights releases.
For the HIPAA tiers in detail, see HIPAA fines and penalties explained. Card-brand non-compliance fines and the monthly fees acquirers add are covered in what PCI DSS non-compliance could cost your business.
The Hidden Impact of Non-Compliance on a Business
The cost of non-compliance goes beyond the fine, into hidden costs that no penalty table lists:
- Legal fees and advisory costs: Counsel during the investigation, the settlement negotiation, and any parallel lawsuit, plus forensic and technical advisers to establish what happened. These fees accrue whether the case ends in a large payment or a small one.
- The remediation program a settlement imposes: OCR's plans with MMG Fusion and Ambry run for three years and two years (2, 3). The company staffs them itself while OCR monitors them.
- Revenue loss: Deals stall when a buyer finds the enforcement release or a weak SOC 2 report, and a defense contractor that loses its eligibility loses the contract with it, as described under lost contracts above.
- Business disruption: Teams rebuild processes on the regulator's schedule instead of their own roadmap, and an order to suspend processing or transfers can stop a product from working (4). Planned projects wait while the same engineers handle remediation.
- Management attention: Executives spend months on regulators, lawyers, board updates, and customer reassurance instead of growth. Where officers certify the company's reports, they also carry the personal exposure described under legal action above.
For the wider numbers behind breach and compliance costs, see the cybersecurity compliance statistics for 2026.
Compliance vs. Non-Compliance: Which Costs More?
Non-compliance usually costs more, because it does not save the cost of compliance. The same control work still has to be done later on someone else's terms, and the penalties and lost revenue in Table 2 come on top. The cost of compliance is a program you plan: you choose the scope, the order of the work, and the budget.
Table 2. The same controls, planned or imposed
| Compliance program | After a finding or a breach | |
|---|---|---|
| Who sets the scope | You | The regulator, the customer, or the contract |
| Timing | Your roadmap | The regulator's deadline, such as 60 days to notify individuals of a HIPAA breach (23) |
| Oversight | Your own or your auditor's | Monitored by the regulator |
| Penalties | None | Per violation, as in Table 1 |
| Revenue | Deals proceed | Deals stall; contracts may not be awarded (9) |
| Example cost | Your planned budget | MMG Fusion: $10,000 and a three-year plan; Ambry: $700,000 and a two-year plan (2, 3) |
A company that runs a gap assessment and fixes what it finds spends on its own schedule. A company that waits for a breach or a whistleblower spends on the regulator's schedule and pays the penalty on top.
The MMG Fusion and Ambry corrective action plans still require the core items listed under corrective action above (2, 3). The company pays for the controls either way, and after a finding or a breach it also pays for everything else.
Risk of Non-Compliance by Industry
The same weak control draws a different regulator, and a different penalty, depending on whose data or money is involved, so compliance risks are industry specific.
SaaS and Technology Companies
The commercial risk comes first: enterprise buyers ask for a SOC 2 report, an ISO 27001 certificate or a completed security questionnaire before they sign, and a weak answer ends the deal. The regulatory risk follows the data. Data privacy and data security failures can draw fines under the CCPA in California (13), penalties under the GDPR for EU personal data (12) and civil penalties under the FTC Act (25). For a vendor with California or EU users, CCPA compliance and GDPR compliance are where the privacy work starts.
The closest case below is MMG Fusion, a software vendor that handles patients' information for healthcare customers (2).
Healthcare Organizations and Business Associates
Hospitals, clinics, health plans, and the vendors that serve them answer to HIPAA, and ignoring it can bring civil penalties, a monitored remediation plan, and, for individuals, criminal liability (2, 11, 15).
HIPAA violations reach covered entities such as Ambry Genetics, a genetic testing company, and business associates such as MMG Fusion (2, 3). Each of the 2026 OCR cases below followed a breach (2, 3, 8), so the 60-day notification clock, for covered entities and business associates alike, had already started (2, 23). See how HIPAA compliance support works, and for the numbers behind healthcare breaches, the data breach statistics.
Defense Contractors
Defense contractors face the contract consequences set out under lost contracts above: the CMMC award rule and the Phase II suspension of July 2026 (9, 18). A false statement about cybersecurity can also draw False Claims Act liability; in the MORSECORP and Georgia Tech cases below, the reported NIST SP 800-171 score did not match the systems, as MORSECORP accepted and as the United States alleged against Georgia Tech (5, 7). NIST 800-171 compliance is the control set behind those scores, and the CMMC compliance guide explains what the requirements involve in practice.
Public Companies
Financial reporting and the internal controls behind it fall under Sarbanes-Oxley. Each periodic report with financial statements must be accompanied by a written statement from the chief executive officer and the chief financial officer, and that certification is personal: an officer who certifies a report knowing it does not comply faces criminal penalties (14). A common weak point is a control the documentation describes but nobody tests, so the certification rests on assurance that was never checked.
Merchants and Payment Providers
PCI DSS is one of the industry standards enforced through the payment card brands rather than by a government regulator. The PCI Security Standards Council writes the standard, but fines and penalties "are defined by each of the payment card brands" (32). For a merchant, that means the card brand's own program decides what non-compliance costs, so the first step is knowing which brand rules apply. A PCI DSS compliance readiness assessment shows where a merchant stands against the standard.
Every Employer
Workplace safety violations fall under OSHA, with willful violations at $11,823 to $165,514 each and serious violations at up to $16,550, and a cited hazard also has to be fixed: failing to correct a violation adds up to $16,550 a day (27). OSHA can also make non-compliance a crime: for a willful violation that causes an employee's death, the OSH Act sets a fine of up to $10,000, up to 6 months in prison, or both, on a first conviction (28).
Consequences of Non-Compliance for Employees and Individuals
Several laws reach the people inside a company: officers who certify reports, employees who misuse health information, and, as whistleblowers, employees who report the failure.
Officers Who Certify
Under Sarbanes-Oxley Section 906, the chief executive officer and chief financial officer who certify a periodic report carry personal criminal exposure, with the fines and prison terms shown in Table 1 (14). Signing is not a formality, which is why many companies ask the managers who own each control to confirm it in writing before the officers sign.
Employees Who Handle Protected Information
HIPAA's criminal provision applies to "a person (including an employee or other individual)" who knowingly obtains or discloses individually identifiable health information in violation of the law. The penalties rise with intent (15):
- Knowing misuse: up to $50,000 and 1 year.
- Under false pretenses: up to $100,000 and 5 years.
- With intent to sell, transfer or use the information for commercial advantage, personal gain, or malicious harm: up to $250,000 and 10 years.
Staff Under Workplace Rules
OSHA's penalties fall on the employer, as set out under Every Employer above. Internal policies often carry a regulatory requirement into daily work, such as who may open patient records or approve a vendor, so a breach of policy can also be a breach of the law. For staff, breaking internal policies can end in discipline under the company's own rules, and in regulated work a single unreported shortcut can become the regulator's finding.
Employees as Whistleblowers
In three of the cases below, the Justice Department's release names a former employee as the whistleblower:
- Georgia Tech: two former members of its cybersecurity team, under the whistleblower provisions of the False Claims Act (7).
- Raytheon: a former Director of Engineering, whose share is $1,512,000 (6).
- Honeywell: a former employee, whose share under the settlement is $375,823 (33).
A fourth case, MORSECORP, also pays a whistleblower share, $851,000 (5). The law generally gives a whistleblower at least 15% and up to 25% of the recovery when the government joins the case, and protects an employee who is "discharged, demoted, suspended, threatened, harassed" for lawful acts in furtherance of such a case (30).
That is the practical reason to fix a known gap: the people who know about it can report it, and the law rewards and protects them for doing so.
Non-Compliance Examples: Recent Enforcement Cases
These enforcement actions from 2023 to 2026 show what non-compliance looks like once a regulator writes it down.
Defense Contractors and the False Claims Act
The defense cases share one pattern: the United States alleged that the company was liable under the False Claims Act because it did not meet the cybersecurity requirements in its federal contracts.
MORSECORP, 26 March 2025
- Who: a defense contractor holding contracts with the Departments of the Army and Air Force.
- What MORSECORP admitted: in January 2021 it submitted a NIST SP 800-171 score of 104, "near the top of the possible score range from -203 to 110." A third-party consultant told it in July 2022 that the score was -142, and the reported score was not updated until June 2023. It also had a third party host its email without requiring the provider to meet the contract's security requirements (5).
- Paid: a $4.6 million False Claims Act settlement, including an $851,000 share for the whistleblower (5).
- Lesson: a self-assessment score is a statement to the government; update it as soon as an outside review contradicts it.
Raytheon Companies and Nightwing, 1 May 2025
- Who: Raytheon and its then-subsidiary Raytheon Cyber Solutions, Inc.; Nightwing, which acquired the business in 2024, is also a party to the settlement.
- What the United States alleged: an internal development system used for unclassified defense work had no system security plan, which DoD cybersecurity regulations require, and did not meet other requirements of DFARS 252.204-7012 and FAR 52.204-21, from 2015 to 2021 (6).
- Paid: $8.4 million, with a $1,512,000 share for the whistleblower, a former Director of Engineering (6).
- Lesson: document the controls of every system that touches contract work, internal development systems included.
Georgia Tech Research Corporation, 30 September 2025
- Who: Georgia Tech Research Corporation and the Georgia Institute of Technology; most of the allegations concern a lab doing sensitive cyber-defense research for the Department of Defense.
- What the United States alleged: the lab ran without anti-virus or anti-malware tools until December 2021 and had no system security plan until at least February 2020, and the summary score of 98 submitted to the Department of Defense for the whole campus was false because it described a "fictitious" or "virtual" environment rather than a real system (7).
- Paid: an $875,000 settlement of a case brought by two former members of Georgia Tech's cybersecurity team (7).
- Lesson: a reported score has to describe the systems that handle the contract's information.
Health Net Federal Services, Fiscal Year 2025
- Who: Health Net Federal Services and its parent, Centene.
- What the United States alleged: the company "falsely certified compliance with cybersecurity requirements", failed to timely scan for known vulnerabilities and "ignored reports from third-party security auditors and its internal audit department of cybersecurity risks" (1).
- Paid: $11.2 million to resolve the allegations (1).
- Lesson: close every audit finding, or accept it formally, with a named owner and a date.
Honeywell Aerospace, 1 September 2026
- Who: Honeywell Aerospace, a business segment of Honeywell International until it became a standalone public company on 29 June 2026.
- What the United States alleged: from April 2020 through December 2023 the business unit "submitted false claims for payment by failing to comply with cybersecurity requirements" in a Department of Defense contract (33).
- Paid: a $2,042,518 False Claims Act settlement, with a $375,823 share for the whistleblower, a former employee (33).
- Lesson: every claim for payment under a contract carries the contract's cybersecurity requirements with it.
Healthcare Organizations and HIPAA
Each of the 2026 OCR cases below followed a breach, and each left the organization with a corrective action plan that runs for years after the payment.
MMG Fusion, 5 March 2026
- Who: a Maryland software company and HIPAA business associate.
- What OCR found: MMG had potentially violated HIPAA rules, including by impermissibly disclosing the protected health information of approximately 15 million individuals and failing to notify the covered entities affected (2).
- Paid: $10,000, set after OCR "considered the financial condition" of the company, in OCR's 12th enforcement action under its Risk Analysis Initiative (2).
- Also required: a corrective action plan monitored for three years (2).
- Lesson: a small payment can still come with a long obligation.
Four Ransomware Settlements, 23 April 2026
- Who: four HIPAA-regulated organizations, among them a network of women's health providers.
- What OCR found: ransomware attacks affected over 427,000 individuals, and each of the four had failed to conduct an accurate and thorough risk analysis (8).
- Paid: $1,165,000 in total, $320,000 of it from the women's health network (8).
- Also required: corrective action plans monitored by OCR for two years (8).
- Lesson: keep the risk analysis accurate, complete and current before an attack, not after it.
Ambry Genetics, 17 September 2026
- Who: a genetic testing company and HIPAA covered entity.
- What happened: a phishing attack compromised an employee's email account, and the protected health information of 225,370 individuals was potentially exfiltrated (3).
- Paid: $700,000 (3).
- Also required: a corrective action plan monitored for two years (3).
- Lesson: one compromised mailbox can become a HIPAA Security Rule case.
Data Protection and GDPR Fines
Meta Ireland, 22 May 2023
- Who: Meta Ireland, in an inquiry by the Irish Data Protection Commission.
- What the Commission found: Meta Ireland continued transferring personal data from the EU to the US after the EU Court of Justice's judgment in the Schrems case, in breach of GDPR Article 46(1) (4).
- Penalty: a €1.2 billion fine (4).
- Also required: suspend future transfers within five months, and stop within six months the unlawful processing, including storage, in the US of personal data of EU/EEA users transferred in violation of the GDPR (4).
- Lesson: GDPR fines scale with global turnover (12), and the orders can matter as much as the fine: a company can be told both to stop a data flow and to stop holding what it moved unlawfully.
Why Non-Compliance Happens
The enforcement record points to five compliance failures, and day-to-day practice adds two more:
- A self-assessment that did not hold: the MORSECORP and Georgia Tech scores in the cases above (5, 7). A score that only the team that wrote it has checked is untested.
- An unvetted third party: MORSECORP's email host from January 2018 to September 2022 (5). Third parties can add compliance exposure, so the contract should set their security responsibilities, someone should verify their controls, and each party should know which legal duties apply to it.
- Documentation that did not exist: the system security plans alleged missing in the Raytheon and Georgia Tech cases (6, 7). Without documentation, a company cannot show what it implemented.
- A skipped risk analysis: OCR runs a Risk Analysis Initiative, and its 2026 settlements keep finding the required risk analysis missing or incomplete (2, 8).
- Findings left without action: Health Net was alleged to have ignored its own internal audit and outside auditors (1). A finding with no owner and no date stays open.
- Controls without an owner: internal controls without a named owner drift, because running and testing them is no one's job.
- Monitoring only at audit time: a gap found once a year may be open for months before anyone looks at it.
Practical Steps to Avoid Regulatory Non-Compliance
Prevention starts with a gap assessment, and each step after it answers a failure in at least one of the settlements above.
1. Start with a Gap Assessment
Measure your environment against the compliance requirements of your framework, one requirement at a time, before an outside party does it for you. A gap assessment turns "we think we are compliant" into a list of compliance gaps with owners. Start with the regimes that carry the largest consequence for your business: CMMC for a defense contractor, HIPAA for a healthcare vendor, SOC 2 for a SaaS company selling to enterprises.
2. Document What You Actually Run
Write down the controls you have, not the ones you plan: policies and procedures, the system security plan, the network boundaries and the data flows. A missing system security plan was among the allegations in both the Raytheon and Georgia Tech cases (6, 7). Documentation is also what audit readiness depends on: it lets you prove compliance quickly when a customer or regulator asks.
3. Keep Self-Assessments Honest
A cybersecurity score submitted to a customer or a government agency can carry contract or legal consequences if it is inaccurate or unsupported. Score conservatively, keep the evidence behind each answer, and update the score when your security posture changes or an outside review finds a different number, the step MORSECORP delayed for almost a year (5).
4. Perform a Risk Analysis and Keep It Current
Identify where sensitive data lives, what threatens it and which safeguards are missing, then keep a risk management plan that tracks the fixes. It is the first item in the MMG Fusion and Ambry corrective action plans (2, 3). A risk assessment starts there, and the guide to preventing data breaches covers the technical controls that follow.
5. Hold Third Parties to Your Requirements
Put your security measures into vendor contracts and check that vendors meet them before they handle your data, then again at renewal. A hosting provider, a managed service provider or a software vendor can bring you into non-compliance, as MORSECORP's case shows (5). Keep a list of which vendors touch regulated data, so you know whose controls you depend on.
6. Assign Owners and Accountability
Give every control and every open finding a named owner and a date, and review the open items with leadership on a fixed schedule. The Health Net allegations show the gap this closes: findings from outside auditors and the internal audit department that were allegedly ignored (1). Someone should also own regulatory changes: the suspension of the CMMC Phase II requirements in July 2026 changed what defense contractors had to prepare for (18).
7. Build a Culture of Compliance
Training, leadership, and incentives decide whether rules are followed between audits. The Department of Justice evaluates a company's compliance program with three "fundamental questions": whether it is well designed, whether it is "adequately resourced and empowered to function effectively," and whether it works in practice (34). Compliance efforts built on one onboarding session do little to answer them; regular employee training tied to the work people do, and leaders who act on reported problems, speak to all three.
How to Resolve Non-Compliance When You Find It
To resolve non-compliance, contain the damage first, then fix the cause behind it and prove the fix held. A repeatable process turns non-compliance issues into closed items.
- Contain first. If data is exposed or a control has failed, stop the damage before you investigate why.
- Find the root cause. Ask whether the control had an owner, whether the process could be followed as written, whether people were trained and whether anything verified the control was working.
- Assign an owner and a date. Write a corrective action plan with one name and one deadline per item, and track it where leadership can see it.
- Fix the process behind the instance. After correcting a missed access review, change how reviews are triggered and evidenced.
- Notify and disclose where the law requires it. Check the legal requirements for notification at once: HIPAA requires notice to affected individuals within 60 days of discovering a breach (23), and federal contractors under FAR 52.203-13 must disclose in writing credible evidence of certain federal crimes or civil False Claims Act violations connected with the contract (19).
- Verify that the fix held. Re-test after a set interval and keep the evidence, so the same gap does not return before the next audit.
Find Your Compliance Gaps Before a Regulator Does
In the defense cases above, the government's allegations turned on a gap between the cybersecurity requirements in a contract and what a company ran in practice. We help you find that gap before a regulator or a customer does:
- Readiness and gap assessments against HIPAA, CMMC, PCI DSS, SOC 2, GDPR, and other frameworks, with a prioritized remediation plan.
- Risk analysis and remediation support, including the documentation that settlements keep finding missing.
- Preparation for the formal assessment, so the score you report is the score you have.
Talk to us about where your gaps are.
Sources
- U.S. Department of Justice, Fact Sheet: False Claims Act Settlements and Judgments, FY2025. https://www.justice.gov/opa/media/1424126/dl
- U.S. Department of Health and Human Services, HHS' Office for Civil Rights Settles HIPAA Investigation of MMG Fusion, LLC Breach Affecting 15 Million Individuals, 5 March 2026. https://www.hhs.gov/press-room/ocr-mmg-fusion-hipaa-agreement.html
- U.S. Department of Health and Human Services, HHS' Office for Civil Rights Settles HIPAA Investigation of Ambry Genetics Phishing Attack Affecting 225,000 Individuals, 17 September 2026. https://www.hhs.gov/press-room/hhs-office-civil-rights-settles-hipaa-investigation-ambry-genetics-phishing-attack-affecting-225000-individuals.html
- Data Protection Commission (Ireland), Data Protection Commission announces conclusion of inquiry into Meta Ireland, 22 May 2023. https://www.dataprotection.ie/en/news-media/press-releases/Data-Protection-Commission-announces-conclusion-of-inquiry-into-Meta-Ireland
- U.S. Department of Justice, Defense Contractor MORSECORP Inc. Agrees to Pay $4.6 Million to Settle Cybersecurity Fraud Allegations, 26 March 2025. https://www.justice.gov/opa/pr/defense-contractor-morsecorp-inc-agrees-pay-46-million-settle-cybersecurity-fraud
- U.S. Department of Justice, Raytheon Companies and Nightwing Group to Pay $8.4M to Resolve False Claims Act Allegations Relating to Non-Compliance with Cybersecurity Requirements in Federal Contracts, 1 May 2025. https://www.justice.gov/opa/pr/raytheon-companies-and-nightwing-group-pay-84m-resolve-false-claims-act-allegations-relating
- U.S. Department of Justice, Georgia Tech Research Corporation Agrees to Pay $875,000 to Resolve Civil Cyber-Fraud Litigation, 30 September 2025. https://www.justice.gov/opa/pr/georgia-tech-research-corporation-agrees-pay-875000-resolve-civil-cyber-fraud-litigation
- U.S. Department of Health and Human Services, HHS' Office for Civil Rights Settles Four HIPAA Security Rule Ransomware Investigations, 23 April 2026. https://www.hhs.gov/press-room/ocr-settles-four-ransomware-investigations.html
- Department of Defense, DFARS 204.7502, Policy (CMMC award eligibility). https://www.ecfr.gov/current/title-48/chapter-2/subchapter-A/part-204/subpart-204.75/section-204.7502
- U.S. Department of Health and Human Services, 45 CFR 160.404, Amount of a civil money penalty. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-160/subpart-D/section-160.404
- U.S. Department of Health and Human Services, 45 CFR 102.3, Penalty adjustment and table. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-A/part-102/section-102.3
- European Union, Regulation (EU) 2016/679 (General Data Protection Regulation), Article 83. https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32016R0679
- California Privacy Protection Agency, Updated Monetary Thresholds in CCPA, effective 1 January 2025. https://www.cppa.ca.gov/regulations/cpi_adjustment.html
- U.S. Code, 18 U.S.C. 1350, Failure of corporate officers to certify financial reports (Sarbanes-Oxley Act, Section 906). https://www.govinfo.gov/content/pkg/USCODE-2024-title18/html/USCODE-2024-title18-partI-chap63-sec1350.htm
- U.S. Code, 42 U.S.C. 1320d-6, Wrongful disclosure of individually identifiable health information. https://www.govinfo.gov/content/pkg/USCODE-2024-title42/html/USCODE-2024-title42-chap7-subchapXI-partC-sec1320d-6.htm
- U.S. Department of Justice, 28 CFR 85.5, Adjustments to penalties. https://www.ecfr.gov/current/title-28/chapter-I/part-85/section-85.5
- Department of Defense, Defense Federal Acquisition Regulation Supplement: Assessing Contractor Implementation of Cybersecurity Requirements, final rule, effective 10 November 2025. https://www.federalregister.gov/documents/2025/09/10/2025-17359/defense-federal-acquisition-regulation-supplement-assessing-contractor-implementation-of
- Department of War, Forging the Arsenal of Freedom: Department of War Suspends CMMC Phase II Requirements, 13 July 2026. https://www.war.gov/News/Releases/Release/Article/4542329/forging-the-arsenal-of-freedom-department-of-war-suspends-cmmc-phase-ii-require/
- Federal Acquisition Regulation, FAR 52.203-13, Contractor Code of Business Ethics and Conduct. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-H/part-52/subpart-52.2/section-52.203-13
- Federal Acquisition Regulation, FAR 9.406-2, Causes for debarment. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-B/part-9/subpart-9.4/section-9.406-2
- Federal Acquisition Regulation, FAR 9.405, Effect of listing. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-B/part-9/subpart-9.4/section-9.405
- Federal Acquisition Regulation, FAR 9.406-4, Period of debarment. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-B/part-9/subpart-9.4/section-9.406-4
- U.S. Department of Health and Human Services, 45 CFR 164.404, Notification to individuals. https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-D/section-164.404
- U.S. Department of Health and Human Services, Annual Civil Monetary Penalties Inflation Adjustment, 91 FR 3665, 28 January 2026. https://www.federalregister.gov/documents/2026/01/28/2026-01688/annual-civil-monetary-penalties-inflation-adjustment
- Federal Trade Commission, 16 CFR 1.98, Adjustment of civil monetary penalty amounts. https://www.ecfr.gov/current/title-16/chapter-I/subchapter-A/part-1/subpart-L/section-1.98
- Federal Trade Commission, Civil Penalty Inflation Adjustments, effective 15 September 2026. https://www.federalregister.gov/documents/2026/09/15/2026-18853/civil-penalty-inflation-adjustments
- Occupational Safety and Health Administration, 29 CFR 1903.15, Proposed penalties. https://www.ecfr.gov/current/title-29/subtitle-B/chapter-XVII/part-1903/section-1903.15
- U.S. Code, 29 U.S.C. 666, Civil and criminal penalties (Occupational Safety and Health Act). https://www.govinfo.gov/content/pkg/USCODE-2024-title29/html/USCODE-2024-title29-chap15-sec666.htm
- U.S. Department of Labor, Federal Civil Penalties Inflation Adjustment Act Annual Adjustments for 2026, effective 27 May 2026. https://www.federalregister.gov/documents/2026/05/27/2026-10456/department-of-labor-federal-civil-penalties-inflation-adjustment-act-annual-adjustments-for-2026
- U.S. Code, 31 U.S.C. 3730, Civil actions for false claims. https://www.govinfo.gov/content/pkg/USCODE-2024-title31/html/USCODE-2024-title31-subtitleIII-chap37-subchapIII-sec3730.htm
- U.S. Department of Justice, Civil Monetary Penalties Inflation Adjustments for 2026. https://www.federalregister.gov/documents/2026/07/15/2026-14236/civil-monetary-penalties-inflation-adjustments-for-2026
- PCI Security Standards Council, FAQ: What are the fines and penalties assessed to companies for non-compliance with the PCI DSS? https://www.pcisecuritystandards.org/faqs/what-are-the-fines-and-penalties-assessed-to-companies-for-non-compliance-with-the-pci-dss/
- U.S. Department of Justice, Honeywell Aerospace Inc. Agrees to Pay Over $2M to Settle False Claims Act Allegations of Failing to Comply with Cybersecurity Requirements in a U.S. Department of Defense Contract, 1 September 2026. https://www.justice.gov/opa/pr/honeywell-aerospace-inc-agrees-pay-over-2m-settle-false-claims-act-allegations-failing
- U.S. Department of Justice, Criminal Division, Evaluation of Corporate Compliance Programs, updated September 2024. https://www.justice.gov/criminal/criminal-fraud/page/file/937501/dl




FAQ
Is non-compliance a criminal offense?

Usually it is a civil matter, but some statutes make it criminal. Under Sarbanes-Oxley Section 906, an officer who knowingly certifies a non-conforming report faces up to $1,000,000 and 10 years (14), and HIPAA's criminal provision reaches employees who knowingly misuse health information (15). For most companies, the legal risks are civil penalties and lawsuits.
What are the penalties for non-compliance?
They depend on the regulation. HIPAA penalties reach $2,190,294 a year for identical violations (11), GDPR fines reach €20 million or 4% of worldwide turnover (12), and False Claims Act penalties reach $28,619 per false claim plus three times the government's damages (16). OCR's 2026 settlements with MMG Fusion and Ambry also imposed monitored remediation plans of three and two years (2, 3).
What are 3 consequences of non-compliance?
First, a financial penalty. Second, a corrective action plan the regulator monitors for years (2, 3). Third, lost business: a customer who walks away, or a contract you can no longer win.
What are examples of non-compliance?
Recent settlements name the same few failures. One contractor was alleged to have no system security plan (6). MORSECORP accepted responsibility for facts showing a reported score its systems did not support and an email host it did not require to meet the contract's security requirements (5). OCR found that four healthcare organizations failed to conduct an accurate and thorough risk analysis (8), and a defense lab was alleged to have run without anti-virus (7).
What are the costs of non-compliance in SaaS?
For a SaaS company the first cost can be a stalled or lost enterprise deal, before any regulator acts. The regulatory costs follow the data. CCPA fines reach $2,663 per violation or $7,988 per intentional one (13), and GDPR fines reach €20 million or 4% of worldwide annual turnover, whichever is higher (12). Civil penalties under the FTC Act reach up to $53,088 per violation (25).
What are the consequences of non-compliance in the workplace?
In the workplace, the consequences are mostly safety consequences under OSHA. The employer faces civil penalties per violation, set out in Table 1, and criminal prosecution if a willful violation causes a worker's death (27, 28). For staff, a broken internal policy can end in discipline; the chapter on employees covers the rest.
About the author
Ron Gupta
—
Senior Director: Governance, Risk and Compliance
Getting his start in tech as an analyst and founder at Via Digital ID, Ron brings to the table a unique approach to cyber security. With over a decade of experience in GRC, Ron has developed and honed a skillset rich in combined audit and assessment as well as risk management and mitigation.
Ron’s ability to convey critical information, results and plans of action to executive leadership is a key skill that allows him to propel the clients he engages with to success. Ron is adept at taking target frameworks, implementing them within environments while reducing overall risk to organizations.