CMMC Controls List: Full List of Requirements by Level and Domain
Published on
March 24, 2026
/
updated on
November 2, 2026
Every CMMC requirement in official wording: 15 at Level 1, 110 at Level 2, 24 at Level 3, with score weights and POA&M rules.
The CMMC controls list has 15 security requirements at Level 1, 110 at Level 2, and 24 more at Level 3, each with an identifier and official wording. The solicitation names the level your contract requires, and a contracting officer may not award to an offeror without it.
Older lists carry other numbers, such as the "17 practices" the 2021 CMMC 2.0 overview counted at Level 1. At Level 1, which allows no plan of action and milestones (POA&M), a requirement missing from your list stays unmet. If you run IT or compliance for a machine shop, engineering firm, software vendor, or other defense supplier that handles FCI or CUI, these are your lists.
On 13 July 2026 the Department of War, a name open to the Department of Defense (DoD) since a September 2025 executive order, suspended CMMC Phase II and kept Phase I self-assessment requirements. The lists remain those of 32 CFR 170.14. For the program, see the CMMC compliance guide.
Download the full CMMC controls list
The spreadsheet and checklist has one row per requirement at Levels 1, 2, and 3. Its columns are Level, Domain, CMMC ID, Requirement (official wording), Points, POA&M, and Also at Level 1, plus empty Status and Evidence location columns for your own checklist. No form is required.
Download the spreadsheetCMMC 2.0 Controls Explained
CMMC security controls are the requirements a defense contractor must meet, at the level its contract names, on each information system that handles the contract's data. Two kinds of data set the level:
- Federal contract information (FCI) is information "not intended for public release" that is provided by or generated for the Government under a contract, other than information the Government provides to the public or simple transactional information, such as what is needed to process payments.
- Controlled unclassified information (CUI), as 32 CFR 2002.4 defines it, is information that a law, regulation, or Government-wide policy "requires or permits an agency to handle using safeguarding or dissemination controls".
The CMMC requirements come from FAR 52.204-21 for Level 1, NIST SP 800-171 Rev 2 for Level 2, and selected requirements of NIST SP 800-172 for Level 3, all made part of the CMMC rule, 32 CFR part 170.
The rule calls them "security requirements". FAR 52.204-21 calls its items "security controls", and the 2021 guides called them "practices", so this CMMC 2.0 controls list uses the three words for the same thing.
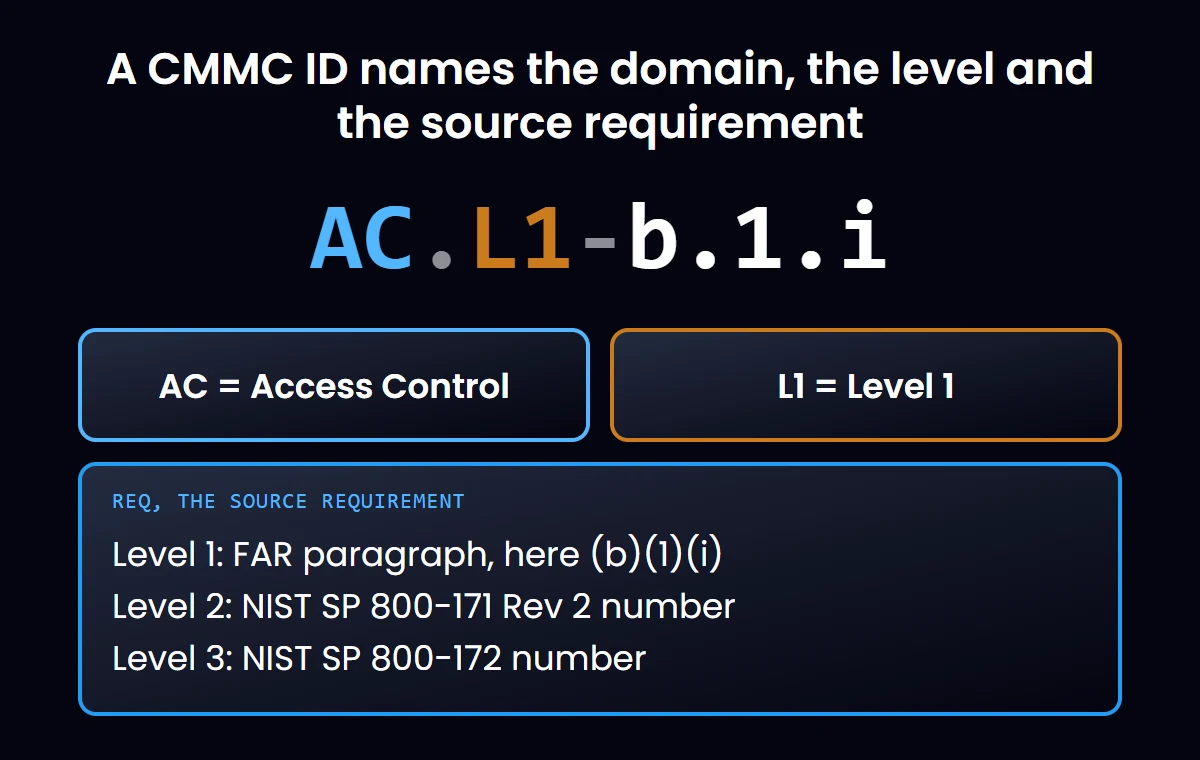
Every requirement carries an identifier in the format DD.L#-REQ that the rule defines. Figure 1 takes one Level 1 ID apart and shows what REQ stands for at each level.
CMMC Control Areas at a Glance
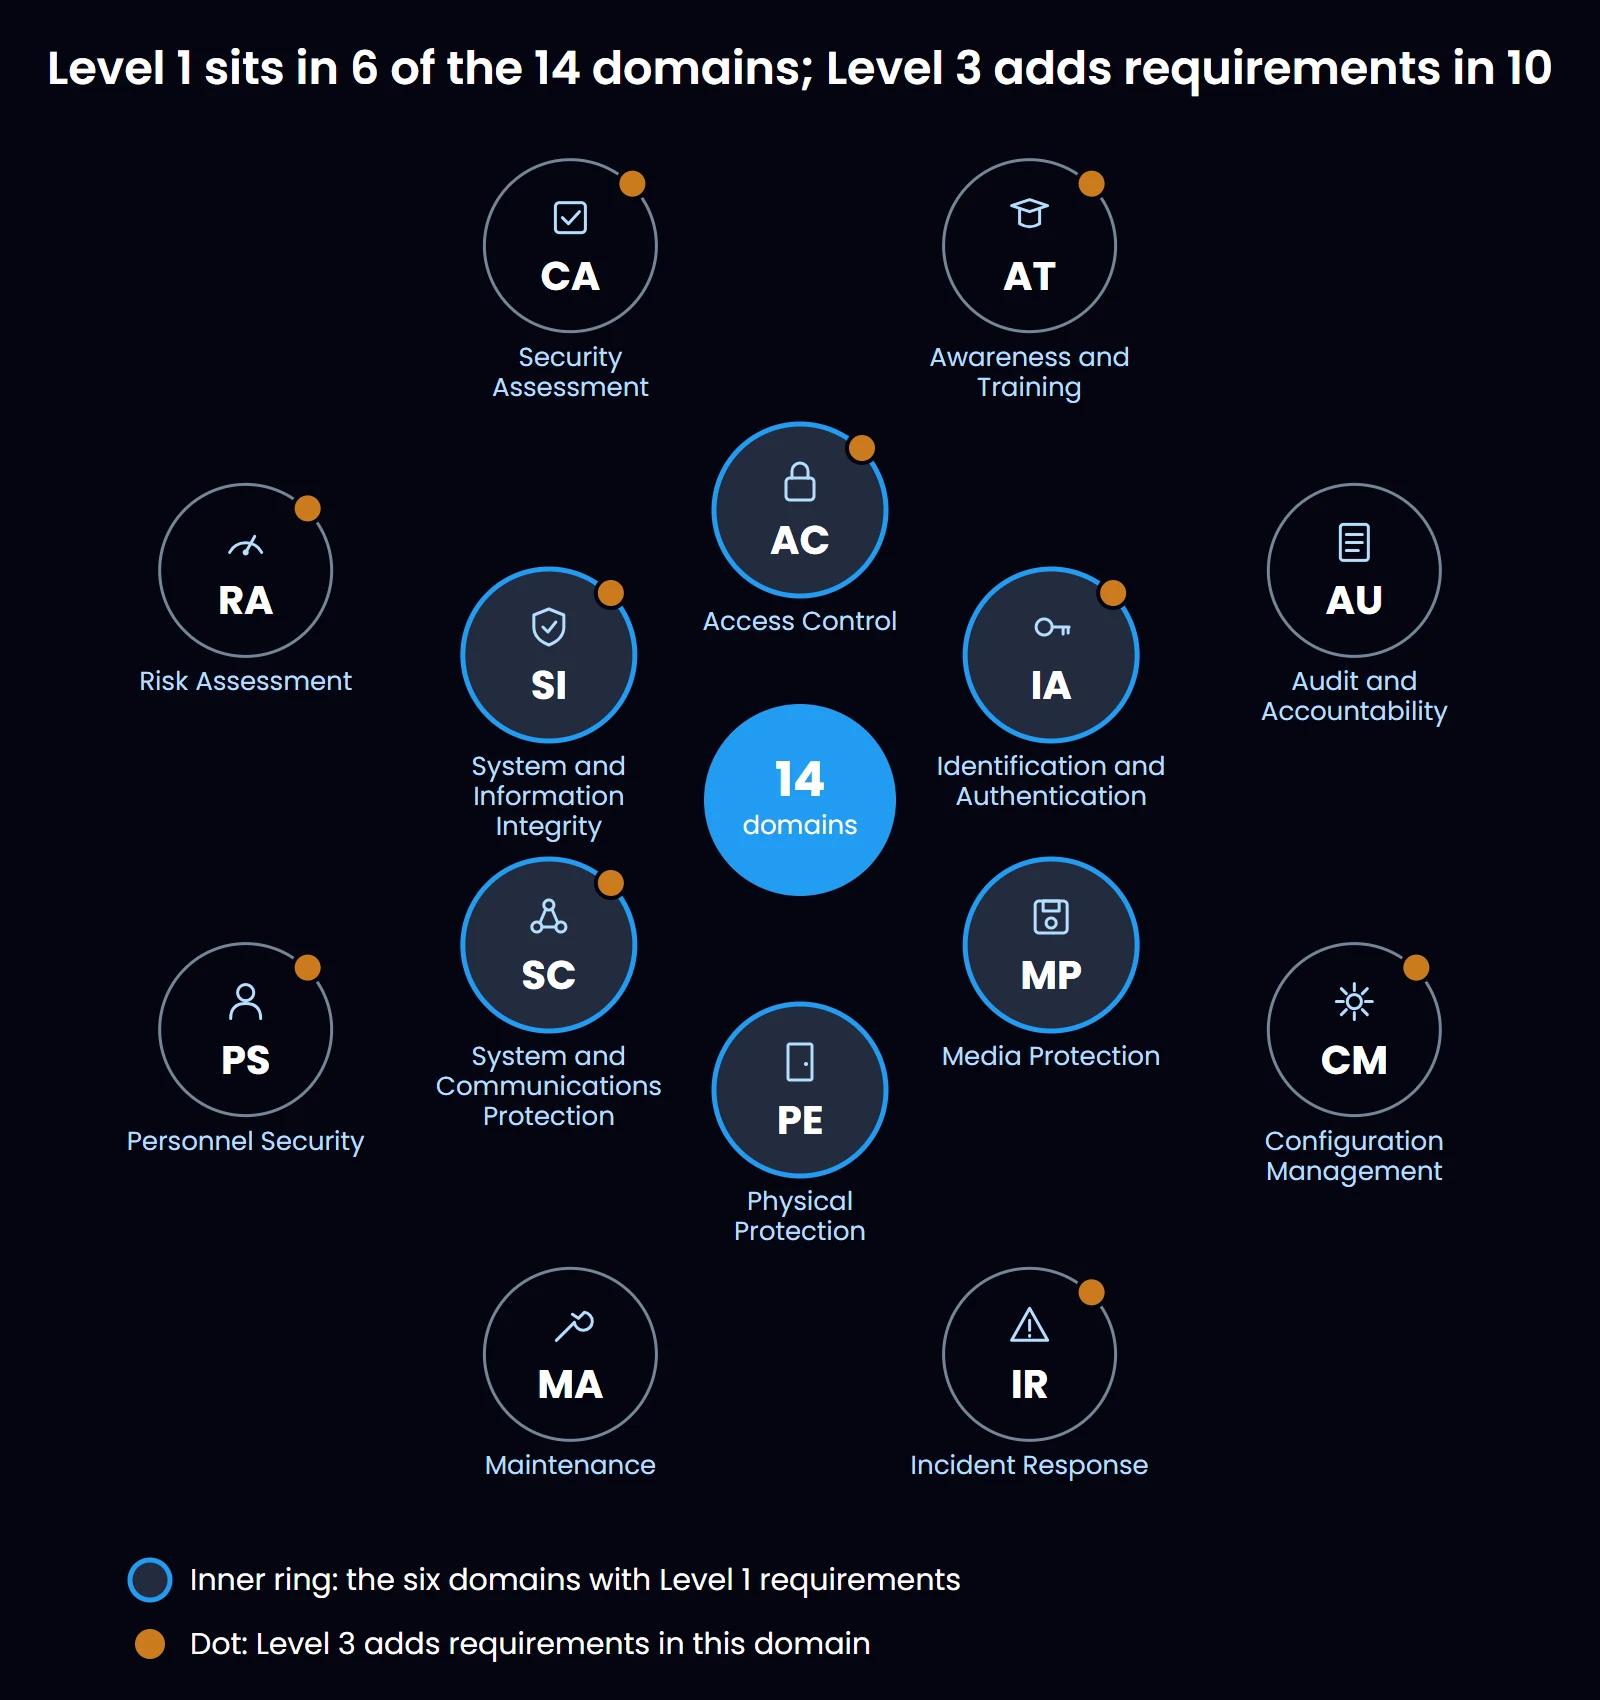
Every requirement on the list sits in one of 14 domains, the CMMC control families, which map to the requirement families of NIST SP 800-171 Rev 2. Table 1 shows what each domain covers and how many requirements it holds at each level; each domain's Level 2 requirements follow in its own table below.
Table 1. The 14 CMMC domains and their requirement counts
| Domain | What it covers | Level 1 (FAR clause) | Level 2 (all 110) | Level 3 (on top of Level 2) | NIST SP 800-171 section |
|---|---|---|---|---|---|
| Access Control (AC) | Who may use systems and what they may do; remote, wireless, and mobile access; CUI flow | 4 | 22 | 2 | 3.1 |
| Awareness and Training (AT) | Security awareness and role training for users, managers, and administrators | 0 | 3 | 2 | 3.2 |
| Audit and Accountability (AU) | Creating, protecting, and reviewing audit logs of system activity | 0 | 9 | 0 | 3.3 |
| Configuration Management (CM) | Baselines, inventories, change control, and least functionality | 0 | 9 | 3 | 3.4 |
| Identification and Authentication (IA) | Identifying users and devices; authenticators, multifactor authentication, and passwords | 2 | 11 | 2 | 3.5 |
| Incident Response (IR) | Handling, tracking, reporting, and testing the response to incidents | 0 | 3 | 2 | 3.6 |
| Maintenance (MA) | Performing and controlling maintenance, its tools, and remote maintenance | 0 | 6 | 0 | 3.7 |
| Media Protection (MP) | Protecting, marking, transporting, and sanitizing media that holds CUI | 1 | 9 | 0 | 3.8 |
| Personnel Security (PS) | Screening people before access; protecting systems through transfers and terminations | 0 | 2 | 1 | 3.9 |
| Physical Protection (PE) | Physical access to systems and facilities, visitors, access logs, and access devices | 2 | 6 | 0 | 3.10 |
| Risk Assessment (RA) | Periodic risk assessments, vulnerability scanning, and remediation | 0 | 3 | 7 | 3.11 |
| Security Assessment (CA) | Assessing controls, plans of action, ongoing monitoring, and the system security plan | 0 | 4 | 1 | 3.12 |
| System and Communications Protection (SC) | Boundary protection, network separation, encryption, and session security | 2 | 16 | 1 | 3.13 |
| System and Information Integrity (SI) | Flaw remediation, malicious code protection, and system monitoring | 4 | 7 | 3 | 3.14 |
| Total | 15 | 110 | 24 |
Sources: NIST SP 800-171 Rev 2 (3); Level 1 guide (2); Table 1 to 32 CFR 170.14(c)(4) (1); read October 2026.
Note. Each Level 1 requirement corresponds to one or more Level 2 requirements in the Level 1 guide, so the columns are not added together.
Figure 2 draws the same 14 domains as two rings, with the six that hold Level 1 requirements in the middle and a dot where Level 3 adds requirements.
CMMC Control Count by Level
Table 2 sets the CMMC controls by level beside the data each level protects and how it is assessed. How many controls are in CMMC Level 1? 32 CFR 170.14(c)(2) points to FAR 52.204-21(b)(1)(i) through (xv), which puts the CMMC Level 1 number of controls at 15.
How many controls are in CMMC Level 2? Level 2 has 110, the number of security requirements in NIST SP 800-171 Rev 2, because the rule makes its requirements "identical" to those. The CMMC Level 2 number of controls was already 110 in the 2021 overview, and nothing since has changed how many controls are in CMMC 2.0 Level 2.
Table 2. CMMC levels and what each one requires
| Level | Name in the 2021 model | Information protected | Requirements | Source document | Assessment and cadence | POA&M allowed | Results recorded |
|---|---|---|---|---|---|---|---|
| Level 1 | Foundational | FCI | 15 | FAR 52.204-21(b)(1)(i) to (xv) | Self-assessment every year | No | SPRS, with an annual affirmation |
| Level 2 | Advanced | CUI | 110 | NIST SP 800-171 Rev 2 | Self-assessment, or a certification assessment by a C3PAO, as the contract names; every three years | Yes, within the limits of 32 CFR 170.21 | SPRS, with an annual affirmation |
| Level 3 | Expert | CUI | 24, on top of Level 2 | NIST SP 800-172, as selected in Table 1 to 32 CFR 170.14(c)(4) | Certification assessment by DCMA DIBCAC every three years, after a Final Level 2 (C3PAO) status | Yes, within the limits of 32 CFR 170.21 | SPRS, with an annual affirmation |
Sources: 32 CFR 170.14 (1), 170.15 (4), 170.16 (5), 170.17 (6), 170.18 (7), 170.21 (8), 170.22 (9); names from the 2021 overview (10); read October 2026.
Note. C3PAO is a CMMC Third-Party Assessment Organization, SPRS the Supplier Performance Risk System, and DCMA DIBCAC the Defense Contract Management Agency's Defense Industrial Base Cybersecurity Assessment Center.
Figure 3 shows how the five levels of CMMC 1.0 became these three.

To find your row, read the level the contract names; it follows the type of data, so FCI alone means Level 1 and CUI means Level 2 or 3. Table 2 describes the rule; the suspension that began on 13 July 2026 limits what new contracts may name, as the FAQ below explains. A subcontractor needs a CMMC status of its own under 32 CFR 170.23 when it will process, store, or transmit FCI or CUI on its information systems under the subcontract. The prime contractor must flow the requirements down to it.
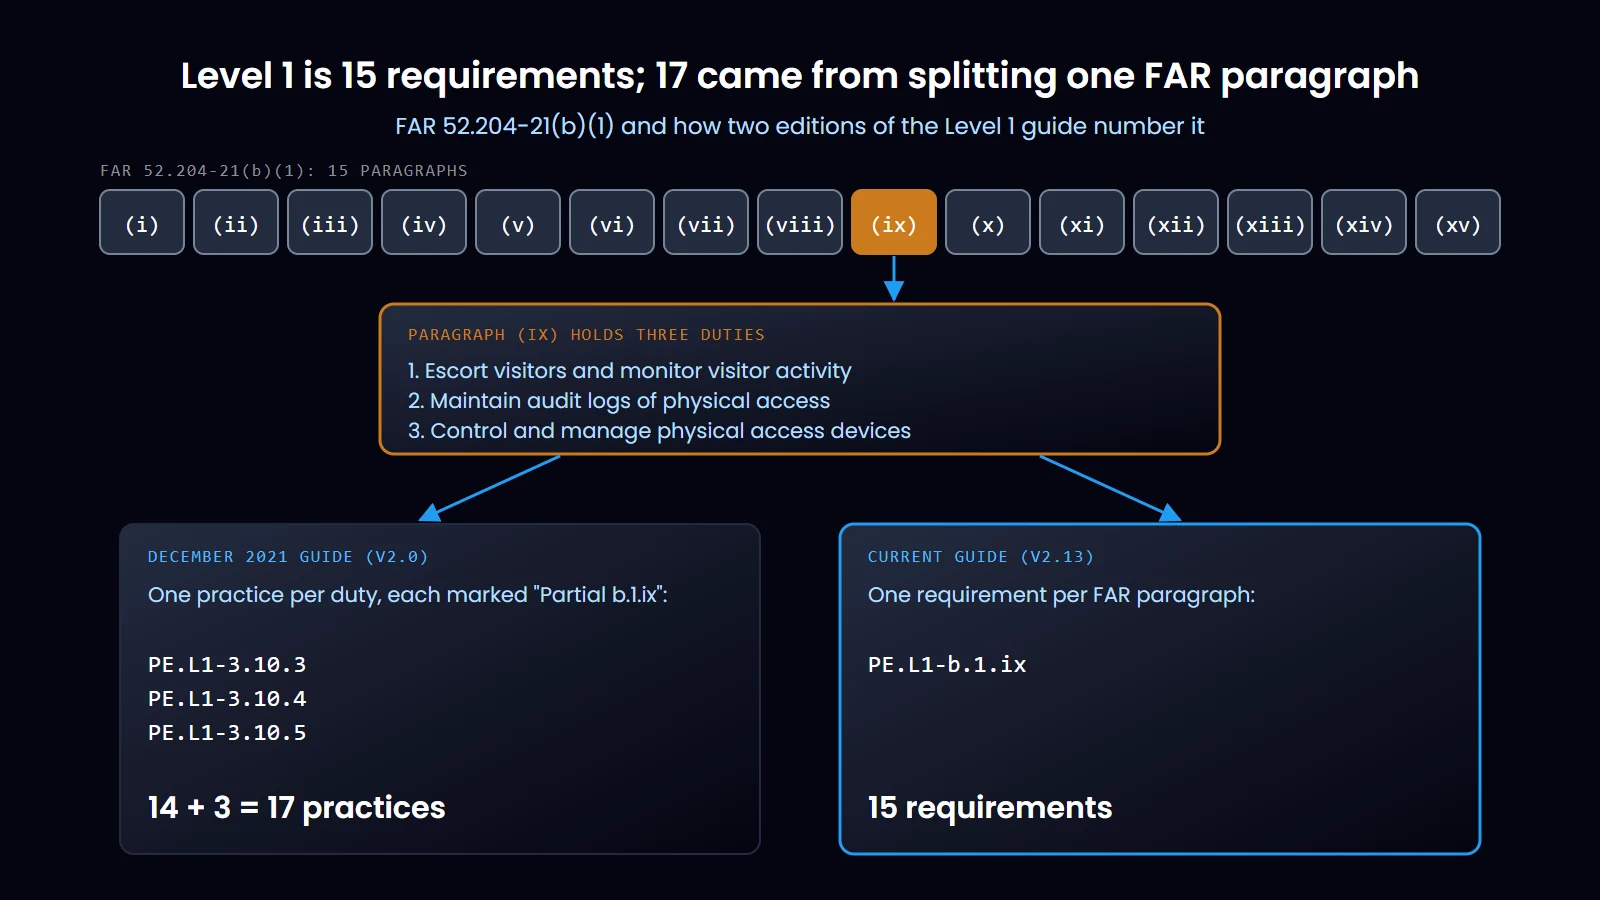
Some lists still count 17 at Level 1 because of one FAR paragraph. Paragraph (b)(1)(ix) holds three duties: "Escort visitors and monitor visitor activity; maintain audit logs of physical access; and control and manage physical access devices". The December 2021 Level 1 guide split it into PE.L1-3.10.3, PE.L1-3.10.4 and PE.L1-3.10.5, each marked "Partial b.1.ix"; the current guide numbers by FAR paragraph, which gives 15. CMMC 1.0 vs 2.0 covers the earlier model.
Figure 4 follows the three duties of paragraph (b)(1)(ix) through both editions of the guide.
CMMC Level 1 Controls List
FAR 52.204-21 supplies the CMMC 2.0 Level 1 controls in 15 safeguarding requirements across six domains. In the 2021 guide the same requirements formed a CMMC 2.0 Level 1 practices list of 17 entries. Summarized from the FAR text, the six domains ask for the following:
- AC (Access Control): limit who gets access and what users may do, control connections to external systems, and control what is posted on publicly accessible systems.
- IA (Identification and Authentication): identify users, processes, and devices, and verify those identities before access.
- MP (Media Protection): sanitize or destroy media holding FCI before disposal or reuse.
- PE (Physical Protection): limit physical access to authorized individuals, escort visitors, keep audit logs of entry, and manage access devices.
- SC (System and Communications Protection): monitor and protect the system boundaries, and put publicly accessible components in separate subnetworks.
- SI (System and Information Integrity): correct flaws in time, protect against malicious code, update that protection, and scan systems and incoming files.
At Level 1 every requirement must be fully implemented to be MET, and no POA&M is permitted.
Table 3. The 15 CMMC Level 1 requirements
| CMMC ID | Requirement (FAR 52.204-21 wording) | Domain |
|---|---|---|
| AC.L1-b.1.i | Limit information system access to authorized users, processes acting on behalf of authorized users, or devices (including other information systems). | Access Control |
| AC.L1-b.1.ii | Limit information system access to the types of transactions and functions that authorized users are permitted to execute. | Access Control |
| AC.L1-b.1.iii | Verify and control/limit connections to and use of external information systems. | Access Control |
| AC.L1-b.1.iv | Control information posted or processed on publicly accessible information systems. | Access Control |
| IA.L1-b.1.v | Identify information system users, processes acting on behalf of users, or devices. | Identification and Authentication |
| IA.L1-b.1.vi | Authenticate (or verify) the identities of those users, processes, or devices, as a prerequisite to allowing access to organizational information systems. | Identification and Authentication |
| MP.L1-b.1.vii | Sanitize or destroy information system media containing Federal Contract Information before disposal or release for reuse. | Media Protection |
| PE.L1-b.1.viii | Limit physical access to organizational information systems, equipment, and the respective operating environments to authorized individuals. | Physical Protection |
| PE.L1-b.1.ix | Escort visitors and monitor visitor activity; maintain audit logs of physical access; and control and manage physical access devices. | Physical Protection |
| SC.L1-b.1.x | Monitor, control, and protect organizational communications (i.e., information transmitted or received by organizational information systems) at the external boundaries and key internal boundaries of the information systems. | System and Communications Protection |
| SC.L1-b.1.xi | Implement subnetworks for publicly accessible system components that are physically or logically separated from internal networks. | System and Communications Protection |
| SI.L1-b.1.xii | Identify, report, and correct information and information system flaws in a timely manner. | System and Information Integrity |
| SI.L1-b.1.xiii | Provide protection from malicious code at appropriate locations within organizational information systems. | System and Information Integrity |
| SI.L1-b.1.xiv | Update malicious code protection mechanisms when new releases are available. | System and Information Integrity |
| SI.L1-b.1.xv | Perform periodic scans of the information system and real-time scans of files from external sources as files are downloaded, opened, or executed. | System and Information Integrity |
Sources: FAR 52.204-21(b)(1) (12); identifiers from the Level 1 guide (2); read October 2026.
Note. The December 2021 guide numbered these by NIST SP 800-171, for example AC.L1-3.1.1.
CMMC Level 2 Controls List
32 CFR 170.14(c)(3) makes Level 2 identical to the 110 security requirements of NIST SP 800-171 Rev 2, so that publication is the CMMC 2.0 Level 2 controls list. In the 2021 overview, the CMMC 2.0 Level 2 practices list was "110 practices aligned with NIST SP 800-171". NIST SP 800-171 Rev 2 itself comes with two details:
- The revision: the rule incorporates Rev 2 by reference, although NIST withdrew Rev 2 on 14 May 2024 in favor of Rev 3.
- NFO controls: controls that NIST marks NFO in the tailoring appendix of Rev 2 are not among the 110.
The count per domain is in Table 1; the 14 tables below give every requirement with its points, whether it can go on a POA&M, and any Level 1 match. The domain tables follow in the order of the NIST families, from Access Control to System and Information Integrity.
CMMC vs NIST 800-171 compares the two programs, and CyberCrest's NIST 800-171 compliance services support work on the same 110 requirements.
The 14 CMMC Domains, Requirement by Requirement
Here is the full list of CMMC controls at Level 2, domain by domain. Each table gives every requirement in the wording of NIST SP 800-171 Rev 2, its points under 32 CFR 170.24, and whether 32 CFR 170.21 lets it sit on a POA&M. The records and people named above each table come from the examine and interview lists of the Level 2 assessment guide.
The last column names the Level 1 requirement that the Level 1 guide maps to each of 17 Level 2 requirements. Three of them, PE.L2-3.10.3 to PE.L2-3.10.5, each match one of the three duties in FAR paragraph (b)(1)(ix), so they are marked (part).
Access Control (AC)
Access Control holds 22 requirements. For most of them the guide has the assessor examine the access control policy, the system security plan, configuration settings, and audit logs.
Table 4. Access Control (AC) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| AC.L2-3.1.1 | Limit system access to authorized users, processes acting on behalf of authorized users, and devices (including other systems). | 5 | No | AC.L1-b.1.i |
| AC.L2-3.1.2 | Limit system access to the types of transactions and functions that authorized users are permitted to execute. | 5 | No | AC.L1-b.1.ii |
| AC.L2-3.1.3 | Control the flow of CUI in accordance with approved authorizations. | 1 | Yes | No |
| AC.L2-3.1.4 | Separate the duties of individuals to reduce the risk of malevolent activity without collusion. | 1 | Yes | No |
| AC.L2-3.1.5 | Employ the principle of least privilege, including for specific security functions and privileged accounts. | 3 | No | No |
| AC.L2-3.1.6 | Use non-privileged accounts or roles when accessing nonsecurity functions | 1 | Yes | No |
| AC.L2-3.1.7 | Prevent non-privileged users from executing privileged functions and capture the execution of such functions in audit logs. | 1 | Yes | No |
| AC.L2-3.1.8 | Limit unsuccessful logon attempts. | 1 | Yes | No |
| AC.L2-3.1.9 | Provide privacy and security notices consistent with applicable CUI rules. | 1 | Yes | No |
| AC.L2-3.1.10 | Use session lock with pattern-hiding displays to prevent access and viewing of data after a period of inactivity | 1 | Yes | No |
| AC.L2-3.1.11 | Terminate (automatically) a user session after a defined condition. | 1 | Yes | No |
| AC.L2-3.1.12 | Monitor and control remote access sessions. | 5 | No | No |
| AC.L2-3.1.13 | Employ cryptographic mechanisms to protect the confidentiality of remote access sessions. | 5 | No | No |
| AC.L2-3.1.14 | Route remote access via managed access control points. | 1 | Yes | No |
| AC.L2-3.1.15 | Authorize remote execution of privileged commands and remote access to security-relevant information. | 1 | Yes | No |
| AC.L2-3.1.16 | Authorize wireless access prior to allowing such connections | 5 | No | No |
| AC.L2-3.1.17 | Protect wireless access using authentication and encryption | 5 | No | No |
| AC.L2-3.1.18 | Control connection of mobile devices. | 5 | No | No |
| AC.L2-3.1.19 | Encrypt CUI on mobile devices and mobile computing platforms. | 3 | No | No |
| AC.L2-3.1.20 | Verify and control/limit connections to and use of external systems. | 1 | No | AC.L1-b.1.iii |
| AC.L2-3.1.21 | Limit use of portable storage devices on external systems. | 1 | Yes | No |
| AC.L2-3.1.22 | Control CUI posted or processed on publicly accessible systems. | 1 | No | AC.L1-b.1.iv |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Awareness and Training (AT)
Awareness and Training holds three requirements. Expect the assessor to ask for the training policy, the curriculum, and the training records, and to interview the people responsible for security awareness training. AT.L2-3.2.1 and AT.L2-3.2.2 are worth 5 points each.
Table 5. Awareness and Training (AT) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| AT.L2-3.2.1 | Ensure that managers, systems administrators, and users of organizational systems are made aware of the security risks associated with their activities and of the applicable policies, standards, and procedures related to the security of those systems. | 5 | No | No |
| AT.L2-3.2.2 | Ensure that personnel are trained to carry out their assigned information security-related duties and responsibilities. | 5 | No | No |
| AT.L2-3.2.3 | Provide security awareness training on recognizing and reporting potential indicators of insider threat. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Audit and Accountability (AU)
Audit and Accountability has nine requirements. AU.L2-3.3.1 and AU.L2-3.3.5, which create the logs and correlate their review, carry 5 points. Besides the logs themselves, the guide lists system incident reports among the records to examine.
Table 6. Audit and Accountability (AU) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| AU.L2-3.3.1 | Create and retain system audit logs and records to the extent needed to enable the monitoring, analysis, investigation, and reporting of unlawful or unauthorized system activity | 5 | No | No |
| AU.L2-3.3.2 | Ensure that the actions of individual system users can be uniquely traced to those users, so they can be held accountable for their actions. | 3 | No | No |
| AU.L2-3.3.3 | Review and update logged events. | 1 | Yes | No |
| AU.L2-3.3.4 | Alert in the event of an audit logging process failure. | 1 | Yes | No |
| AU.L2-3.3.5 | Correlate audit record review, analysis, and reporting processes for investigation and response to indications of unlawful, unauthorized, suspicious, or unusual activity. | 5 | No | No |
| AU.L2-3.3.6 | Provide audit record reduction and report generation to support on-demand analysis and reporting. | 1 | Yes | No |
| AU.L2-3.3.7 | Provide a system capability that compares and synchronizes internal system clocks with an authoritative source to generate time stamps for audit records | 1 | Yes | No |
| AU.L2-3.3.8 | Protect audit information and audit logging tools from unauthorized access, modification, and deletion. | 1 | Yes | No |
| AU.L2-3.3.9 | Limit management of audit logging functionality to a subset of privileged users. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Configuration Management (CM)
Configuration Management holds nine requirements. The assessor looks for the configuration management plan, change control records, and the security configuration checklists your team works from. CM.L2-3.4.1, CM.L2-3.4.2 and CM.L2-3.4.5 through CM.L2-3.4.8 carry 5 points each.
Table 7. Configuration Management (CM) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| CM.L2-3.4.1 | Establish and maintain baseline configurations and inventories of organizational systems (including hardware, software, firmware, and documentation) throughout the respective system development life cycles. | 5 | No | No |
| CM.L2-3.4.2 | Establish and enforce security configuration settings for information technology products employed in organizational systems. | 5 | No | No |
| CM.L2-3.4.3 | Track, review, approve or disapprove, and log changes to organizational systems. | 1 | Yes | No |
| CM.L2-3.4.4 | Analyze the security impact of changes prior to implementation. | 1 | Yes | No |
| CM.L2-3.4.5 | Define, document, approve, and enforce physical and logical access restrictions associated with changes to organizational systems. | 5 | No | No |
| CM.L2-3.4.6 | Employ the principle of least functionality by configuring organizational systems to provide only essential capabilities. | 5 | No | No |
| CM.L2-3.4.7 | Restrict, disable, or prevent the use of nonessential programs, functions, ports, protocols, and services. | 5 | No | No |
| CM.L2-3.4.8 | Apply deny-by-exception (blacklisting) policy to prevent the use of unauthorized software or deny-all, permit-by-exception (whitelisting) policy to allow the execution of authorized software. | 5 | No | No |
| CM.L2-3.4.9 | Control and monitor user-installed software. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Identification and Authentication (IA)
Identification and Authentication holds 11 requirements. If multifactor authentication, IA.L2-3.5.3, covers only remote and privileged users, the score loses 3 points, and it loses 5 if it covers no users. Evidence starts with the identification and authentication policy and the list of system accounts.
Table 8. Identification and Authentication (IA) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| IA.L2-3.5.1 | Identify system users, processes acting on behalf of users, and devices. | 5 | No | IA.L1-b.1.v |
| IA.L2-3.5.2 | Authenticate (or verify) the identities of users, processes, or devices, as a prerequisite to allowing access to organizational systems. | 5 | No | IA.L1-b.1.vi |
| IA.L2-3.5.3 | Use multifactor authentication for local and network access to privileged accounts and for network access to non-privileged accounts. | 3 or 5 | No | No |
| IA.L2-3.5.4 | Employ replay-resistant authentication mechanisms for network access to privileged and non-privileged accounts. | 1 | Yes | No |
| IA.L2-3.5.5 | Prevent reuse of identifiers for a defined period. | 1 | Yes | No |
| IA.L2-3.5.6 | Disable identifiers after a defined period of inactivity. | 1 | Yes | No |
| IA.L2-3.5.7 | Enforce a minimum password complexity and change of characters when new passwords are created. | 1 | Yes | No |
| IA.L2-3.5.8 | Prohibit password reuse for a specified number of generations. | 1 | Yes | No |
| IA.L2-3.5.9 | Allow temporary password use for system logons with an immediate change to a permanent password. | 1 | Yes | No |
| IA.L2-3.5.10 | Store and transmit only cryptographically-protected passwords. | 5 | No | No |
| IA.L2-3.5.11 | Obscure feedback of authentication information | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Incident Response (IR)
Incident Response has three requirements. The examine lists center on the incident response policy and plan. Handling and reporting, IR.L2-3.6.1 and IR.L2-3.6.2, are worth 5 points each, and testing, IR.L2-3.6.3, is worth 1.
Table 9. Incident Response (IR) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| IR.L2-3.6.1 | Establish an operational incident-handling capability for organizational systems that includes preparation, detection, analysis, containment, recovery, and user response activities. | 5 | No | No |
| IR.L2-3.6.2 | Track, document, and report incidents to designated officials and/or authorities both internal and external to the organization. | 5 | No | No |
| IR.L2-3.6.3 | Test the organizational incident response capability. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Maintenance (MA)
Maintenance holds six requirements. All six name maintenance records among the records an assessor will examine. MA.L2-3.7.2 on controlling maintenance and MA.L2-3.7.5 on multifactor authentication for nonlocal sessions carry 5 points.
Table 10. Maintenance (MA) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| MA.L2-3.7.1 | Perform maintenance on organizational systems. | 3 | No | No |
| MA.L2-3.7.2 | Provide controls on the tools, techniques, mechanisms, and personnel used to conduct system maintenance. | 5 | No | No |
| MA.L2-3.7.3 | Ensure equipment removed for off-site maintenance is sanitized of any CUI. | 1 | Yes | No |
| MA.L2-3.7.4 | Check media containing diagnostic and test programs for malicious code before the media are used in organizational systems. | 3 | No | No |
| MA.L2-3.7.5 | Require multifactor authentication to establish nonlocal maintenance sessions via external network connections and terminate such connections when nonlocal maintenance is complete. | 5 | No | No |
| MA.L2-3.7.6 | Supervise the maintenance activities of maintenance personnel without required access authorization. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Media Protection (MP)
Media Protection has nine requirements. The guide's examine lists start with the media protection policy and add records such as those of media sanitization. MP.L2-3.8.3 on sanitizing media and MP.L2-3.8.7 on removable media carry 5 points.
Table 11. Media Protection (MP) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| MP.L2-3.8.1 | Protect (i.e., physically control and securely store) system media containing CUI, both paper and digital. | 3 | No | No |
| MP.L2-3.8.2 | Limit access to CUI on system media to authorized users | 3 | No | No |
| MP.L2-3.8.3 | Sanitize or destroy system media containing CUI before disposal or release for reuse. | 5 | No | MP.L1-b.1.vii |
| MP.L2-3.8.4 | Mark media with necessary CUI markings and distribution limitations. | 1 | Yes | No |
| MP.L2-3.8.5 | Control access to media containing CUI and maintain accountability for media during transport outside of controlled areas. | 1 | Yes | No |
| MP.L2-3.8.6 | Implement cryptographic mechanisms to protect the confidentiality of CUI stored on digital media during transport unless otherwise protected by alternative physical safeguards. | 1 | Yes | No |
| MP.L2-3.8.7 | Control the use of removable media on system components. | 5 | No | No |
| MP.L2-3.8.8 | Prohibit the use of portable storage devices when such devices have no identifiable owner. | 3 | No | No |
| MP.L2-3.8.9 | Protect the confidentiality of backup CUI at storage locations. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Personnel Security (PS)
Personnel Security holds two requirements. Screening, PS.L2-3.9.1, is worth 3 points and personnel actions, PS.L2-3.9.2, 5 points. An assessor examines records of screened personnel and of terminated credentials.
Table 12. Personnel Security (PS) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| PS.L2-3.9.1 | Screen individuals prior to authorizing access to organizational systems containing CUI. | 3 | No | No |
| PS.L2-3.9.2 | Ensure that organizational systems containing CUI are protected during and after personnel actions such as terminations and transfers | 5 | No | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Physical Protection (PE)
Physical Protection holds six requirements. The three requirements on visitors and physical access (PE.L2-3.10.3 through PE.L2-3.10.5) map to FAR paragraph (b)(1)(ix). Assessors examine physical access logs, the inventory of access devices, and the entry and exit points.
Table 13. Physical Protection (PE) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| PE.L2-3.10.1 | Limit physical access to organizational systems, equipment, and the respective operating environments to authorized individuals. | 5 | No | PE.L1-b.1.viii |
| PE.L2-3.10.2 | Protect and monitor the physical facility and support infrastructure for organizational systems. | 5 | No | No |
| PE.L2-3.10.3 | Escort visitors and monitor visitor activity. | 1 | No | PE.L1-b.1.ix (part) |
| PE.L2-3.10.4 | Maintain audit logs of physical access. | 1 | No | PE.L1-b.1.ix (part) |
| PE.L2-3.10.5 | Control and manage physical access devices. | 1 | No | PE.L1-b.1.ix (part) |
| PE.L2-3.10.6 | Enforce safeguarding measures for CUI at alternate work sites. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Risk Assessment (RA)
Risk Assessment has three requirements. The assessor examines the risk assessment itself, the vulnerability scanning results, and the patch and vulnerability management records. Vulnerability scanning, RA.L2-3.11.2, carries 5 points, and the periodic risk assessment, RA.L2-3.11.1, carries 3.
Table 14. Risk Assessment (RA) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| RA.L2-3.11.1 | Periodically assess the risk to organizational operations (including mission, functions, image, or reputation), organizational assets, and individuals, resulting from the operation of organizational systems and the associated processing, storage, or transmission of CUI | 3 | No | No |
| RA.L2-3.11.2 | Scan for vulnerabilities in organizational systems and applications periodically and when new vulnerabilities affecting those systems and applications are identified. | 5 | No | No |
| RA.L2-3.11.3 | Remediate vulnerabilities in accordance with risk assessments. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
Security Assessment (CA)
Security Assessment counts the system security plan, CA.L2-3.12.4, among its four requirements. The rule lists no point value for it; without an up-to-date plan an assessment "could not be completed".
Table 15. Security Assessment (CA) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| CA.L2-3.12.1 | Periodically assess the security controls in organizational systems to determine if the controls are effective in their application. | 5 | No | No |
| CA.L2-3.12.2 | Develop and implement plans of action designed to correct deficiencies and reduce or eliminate vulnerabilities in organizational systems. | 3 | No | No |
| CA.L2-3.12.3 | Monitor security controls on an ongoing basis to ensure the continued effectiveness of the controls. | 5 | No | No |
| CA.L2-3.12.4 | Develop, document, and periodically update system security plans that describe system boundaries, system environments of operation, how security requirements are implemented, and the relationships with or connections to other systems. | None listed | No | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
System and Communications Protection (SC)
System and Communications Protection holds 16 requirements. If CUI encryption (SC.L2-3.13.11) is used but not FIPS-validated, the score loses 3 points; it loses 5 if encryption is not used, and only the 3-point case can go on a POA&M. Assessors examine boundary protection procedures and the list of key internal boundaries.
Table 16. System and Communications Protection (SC) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| SC.L2-3.13.1 | Monitor, control, and protect communications (i.e., information transmitted or received by organizational systems) at the external boundaries and key internal boundaries of organizational systems. | 5 | No | SC.L1-b.1.x |
| SC.L2-3.13.2 | Employ architectural designs, software development techniques, and systems engineering principles that promote effective information security within organizational systems. | 5 | No | No |
| SC.L2-3.13.3 | Separate user functionality from system management functionality. | 1 | Yes | No |
| SC.L2-3.13.4 | Prevent unauthorized and unintended information transfer via shared system resources. | 1 | Yes | No |
| SC.L2-3.13.5 | Implement subnetworks for publicly accessible system components that are physically or logically separated from internal networks. | 5 | No | SC.L1-b.1.xi |
| SC.L2-3.13.6 | Deny network communications traffic by default and allow network communications traffic by exception (i.e., deny all, permit by exception). | 5 | No | No |
| SC.L2-3.13.7 | Prevent remote devices from simultaneously establishing non-remote connections with organizational systems and communicating via some other connection to resources in external networks (i.e., split tunneling). | 1 | Yes | No |
| SC.L2-3.13.8 | Implement cryptographic mechanisms to prevent unauthorized disclosure of CUI during transmission unless otherwise protected by alternative physical safeguards. | 3 | No | No |
| SC.L2-3.13.9 | Terminate network connections associated with communications sessions at the end of the sessions or after a defined period of inactivity. | 1 | Yes | No |
| SC.L2-3.13.10 | Establish and manage cryptographic keys for cryptography employed in organizational systems. | 1 | Yes | No |
| SC.L2-3.13.11 | Employ FIPS-validated cryptography when used to protect the confidentiality of CUI. | 3 or 5 | Only at 3 points | No |
| SC.L2-3.13.12 | Prohibit remote activation of collaborative computing devices and provide indication of devices in use to users present at the device. | 1 | Yes | No |
| SC.L2-3.13.13 | Control and monitor the use of mobile code. | 1 | Yes | No |
| SC.L2-3.13.14 | Control and monitor the use of Voice over Internet Protocol (VoIP) technologies. | 1 | Yes | No |
| SC.L2-3.13.15 | Protect the authenticity of communications sessions. | 5 | No | No |
| SC.L2-3.13.16 | Protect the confidentiality of CUI at rest. | 1 | Yes | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
System and Information Integrity (SI)
Seven requirements make up System and Information Integrity. Each of them is worth 3 or 5 points. On the examine lists are malicious code protection mechanisms and the records of their updates.
Table 17. System and Information Integrity (SI) requirements
| CMMC ID | Requirement (NIST SP 800-171 Rev 2 wording) | Points | Can go on a POA&M | Also at Level 1 |
|---|---|---|---|---|
| SI.L2-3.14.1 | Identify, report, and correct system flaws in a timely manner. | 5 | No | SI.L1-b.1.xii |
| SI.L2-3.14.2 | Provide protection from malicious code at designated locations within organizational systems. | 5 | No | SI.L1-b.1.xiii |
| SI.L2-3.14.3 | Monitor system security alerts and advisories and take action in response. | 5 | No | No |
| SI.L2-3.14.4 | Update malicious code protection mechanisms when new releases are available. | 5 | No | SI.L1-b.1.xiv |
| SI.L2-3.14.5 | Perform periodic scans of organizational systems and real-time scans of files from external sources as files are downloaded, opened, or executed. | 3 | No | SI.L1-b.1.xv |
| SI.L2-3.14.6 | Monitor organizational systems, including inbound and outbound communications traffic, to detect attacks and indicators of potential attacks. | 5 | No | No |
| SI.L2-3.14.7 | Identify unauthorized use of organizational systems. | 3 | No | No |
Sources: NIST SP 800-171 Rev 2 (3); points, 32 CFR 170.24 (14); POA&M, 32 CFR 170.21 (8); Level 1 column, Level 1 guide (2); read October 2026.
CMMC Level 3 Controls List
CMMC Level 3 adds 24 requirements selected from NIST SP 800-172, a set of enhanced requirements for protecting CUI, with parameters the Department of Defense assigned. Under 32 CFR 170.18, only DCMA DIBCAC assesses Level 3, and only after the contractor holds a Final Level 2 (C3PAO) status for the systems in the Level 3 assessment scope.
The wording in Table 18 is that of Table 1 to 32 CFR 170.14(c)(4), where italics mark the DoD-assigned parameters, such as an incident response team deployable "within 24 hours". The Department of War CIO's FAQ calls them requirements "in addition to the 110" of Level 2. Each of the 24 is worth 1 point under 32 CFR 170.24, and seven of them may not go on a POA&M. Table 1 above shows how they spread across the domains.
Table 18. The 24 CMMC Level 3 requirements
| CMMC ID | Requirement (wording of Table 1 to 32 CFR 170.14(c)(4)) | Can go on a POA&M |
|---|---|---|
| AC.L3-3.1.2e | Restrict access to systems and system components to only those information resources that are owned, provisioned, or issued by the organization. | Yes |
| AC.L3-3.1.3e | Employ secure information transfer solutions to control information flows between security domains on connected systems. | Yes |
| AT.L3-3.2.1e | Provide awareness training upon initial hire, following a significant cyber event, and at least annually, focused on recognizing and responding to threats from social engineering, advanced persistent threat actors, breaches, and suspicious behaviors; update the training at least annually or when there are significant changes to the threat. | Yes |
| AT.L3-3.2.2e | Include practical exercises in awareness training for all users, tailored by roles, to include general users, users with specialized roles, and privileged users, that are aligned with current threat scenarios and provide feedback to individuals involved in the training and their supervisors. | Yes |
| CM.L3-3.4.1e | Establish and maintain an authoritative source and repository to provide a trusted source and accountability for approved and implemented system components. | Yes |
| CM.L3-3.4.2e | Employ automated mechanisms to detect misconfigured or unauthorized system components; after detection, remove the components or place the components in a quarantine or remediation network to facilitate patching, re-configuration, or other mitigations. | Yes |
| CM.L3-3.4.3e | Employ automated discovery and management tools to maintain an up-to-date, complete, accurate, and readily available inventory of system components. | Yes |
| IA.L3-3.5.1e | Identify and authenticate systems and system components, where possible, before establishing a network connection using bidirectional authentication that is cryptographically based and replay resistant. | Yes |
| IA.L3-3.5.3e | Employ automated or manual/procedural mechanisms to prohibit system components from connecting to organizational systems unless the components are known, authenticated, in a properly configured state, or in a trust profile. | Yes |
| IR.L3-3.6.1e | Establish and maintain a security operations center capability that operates 24/7, with allowance for remote/on-call staff. | No |
| IR.L3-3.6.2e | Establish and maintain a cyber-incident response team that can be deployed by the organization within 24 hours. | No |
| PS.L3-3.9.2e | Ensure that organizational systems are protected if adverse information develops or is obtained about individuals with access to CUI. | Yes |
| RA.L3-3.11.1e | Employ threat intelligence, at a minimum from open or commercial sources, and any DoD-provided sources, as part of a risk assessment to guide and inform the development of organizational systems, security architectures, selection of security solutions, monitoring, threat hunting, and response and recovery activities. | No |
| RA.L3-3.11.2e | Conduct cyber threat hunting activities on an on-going aperiodic basis or when indications warrant, to search for indicators of compromise in organizational systems and detect, track, and disrupt threats that evade existing controls. | Yes |
| RA.L3-3.11.3e | Employ advanced automation and analytics capabilities in support of analysts to predict and identify risks to organizations, systems, and system components. | Yes |
| RA.L3-3.11.4e | Document or reference in the system security plan the security solution selected, the rationale for the security solution, and the risk determination. | No |
| RA.L3-3.11.5e | Assess the effectiveness of security solutions at least annually or upon receipt of relevant cyber threat information, or in response to a relevant cyber incident, to address anticipated risk to organizational systems and the organization based on current and accumulated threat intelligence. | Yes |
| RA.L3-3.11.6e | Assess, respond to, and monitor supply chain risks associated with organizational systems and system components. | No |
| RA.L3-3.11.7e | Develop a plan for managing supply chain risks associated with organizational systems and system components; update the plan at least annually, and upon receipt of relevant cyber threat information, or in response to a relevant cyber incident. | No |
| CA.L3-3.12.1e | Conduct penetration testing at least annually or when significant security changes are made to the system, leveraging automated scanning tools and ad hoc tests using subject matter experts. | Yes |
| SC.L3-3.13.4e | Employ physical isolation techniques or logical isolation techniques or both in organizational systems and system components. | Yes |
| SI.L3-3.14.1e | Verify the integrity of security critical and essential software using root of trust mechanisms or cryptographic signatures. | Yes |
| SI.L3-3.14.3e | Ensure that specialized assets including IoT, IIoT, OT, GFE, Restricted Information Systems, and test equipment are included in the scope of the specified enhanced security requirements or are segregated in purpose-specific networks. | No |
| SI.L3-3.14.6e | Use threat indicator information and effective mitigations obtained from, at a minimum, open or commercial sources, and any DoD-provided sources, to guide and inform intrusion detection and threat hunting. | Yes |
Sources: Table 1 to 32 CFR 170.14(c)(4) (1); POA&M, 32 CFR 170.21(a)(3) (8); read October 2026.
How Assessors Check Each CMMC Control
Assessors check each requirement with its CMMC control procedures, the assessment procedures of NIST SP 800-171A, which the rule names for Level 2 self-assessments and C3PAO assessments alike. Each procedure pairs "an assessment objective and a set of potential assessment methods and assessment objects", and NIST SP 800-171A defines the three methods:
- Examine: "reviewing, inspecting, observing, studying, or analyzing" objects such as policies, plans, mechanisms, and activities.
- Interview: "holding discussions with individuals or groups" who run the requirement.
- Test: "exercising assessment objects (i.e., activities, mechanisms) under specified conditions to compare actual with expected behavior".
One requirement shows the method end to end. AC.L2-3.1.1 asks you to "Limit system access to authorized users, processes acting on behalf of authorized users, and devices (including other systems)". The Level 2 guide breaks it into objectives [a] through [f]. The first three ask whether authorized users, processes, and devices are identified; the last three ask whether system access is limited to each.
For evidence, the guide's examine list includes the access control policy and the list of active system accounts. Its interview list names people with account management responsibilities, and its test list names the processes for managing system accounts.
Figure 5 traces that requirement from its wording to the evidence an assessor asks for.
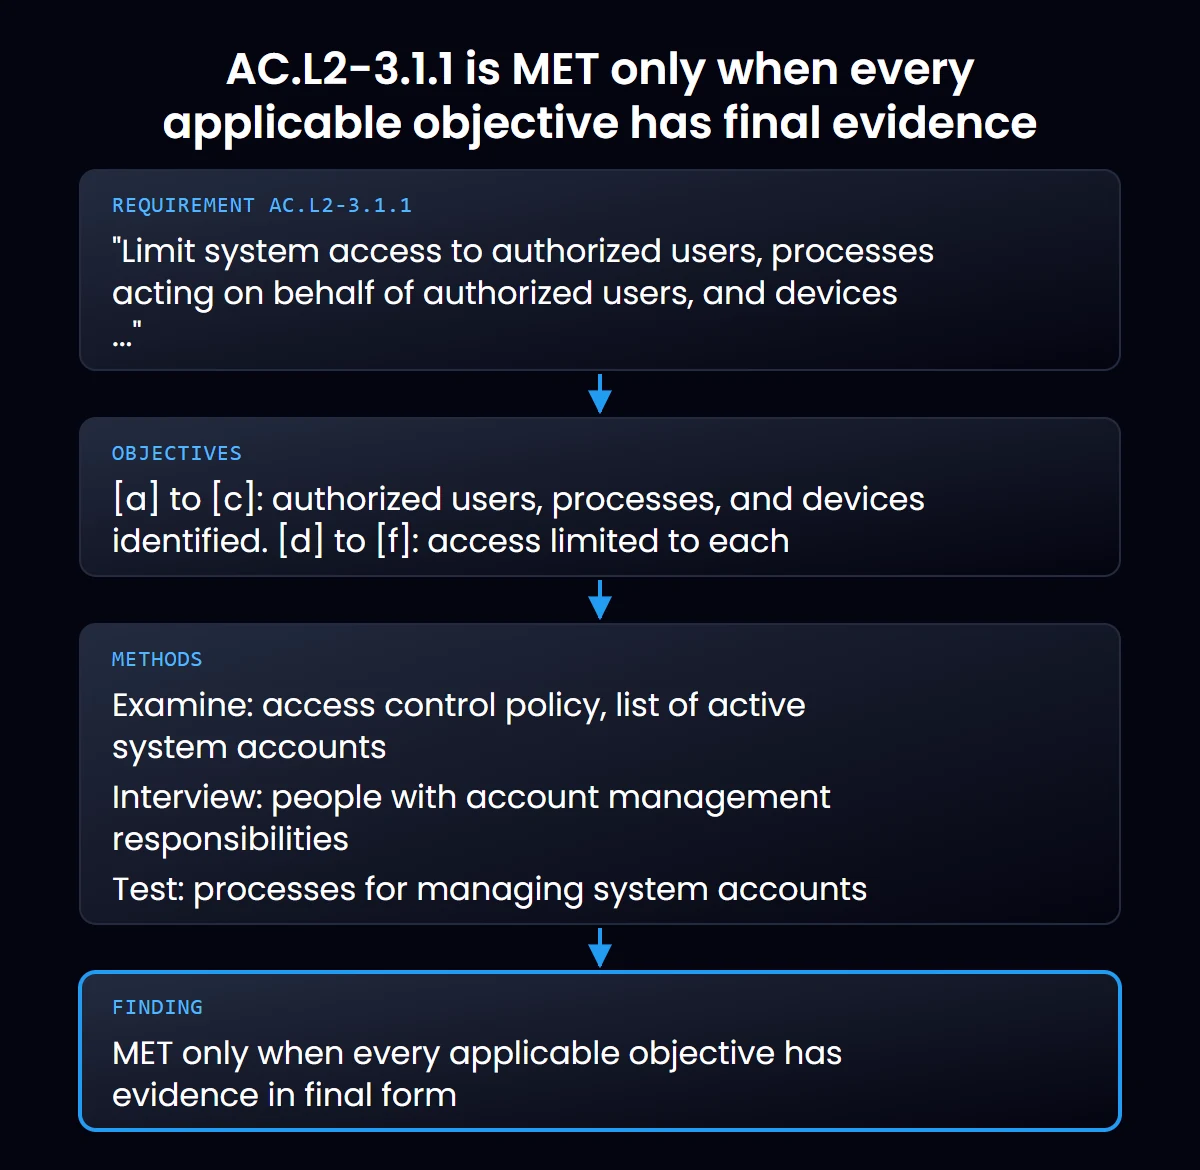
A requirement is MET only when every applicable objective is satisfied by evidence, and "All evidence must be in final form and not draft". Working papers, drafts, and unapproved policies do not count. NIST requirement 3.12.4 asks the system security plan to describe "how security requirements are implemented", and the Level 2 guide puts the plan on the examine list of almost every requirement. If you keep this CMMC controls list in your own tracker, one row per requirement with these fields keeps the evidence current:
- the requirement ID and the systems in scope;
- an owner and a backup owner;
- the procedure and where its evidence is stored;
- how often evidence is collected and reviewed;
- any open gap and what closes it.
At Level 2 the maximum score equals the number of requirements, and each requirement NOT MET subtracts its 1, 3, or 5 points. A Conditional status also needs a score of at least 0.8 of the maximum, and it expires unless its POA&M is closed out within 180 days. The Points and POA&M columns of the domain tables are those values; scoring as a whole is covered in the CMMC compliance guide.
Figure 6 follows a Level 2 score to the status it earns, Final only when every requirement is MET.
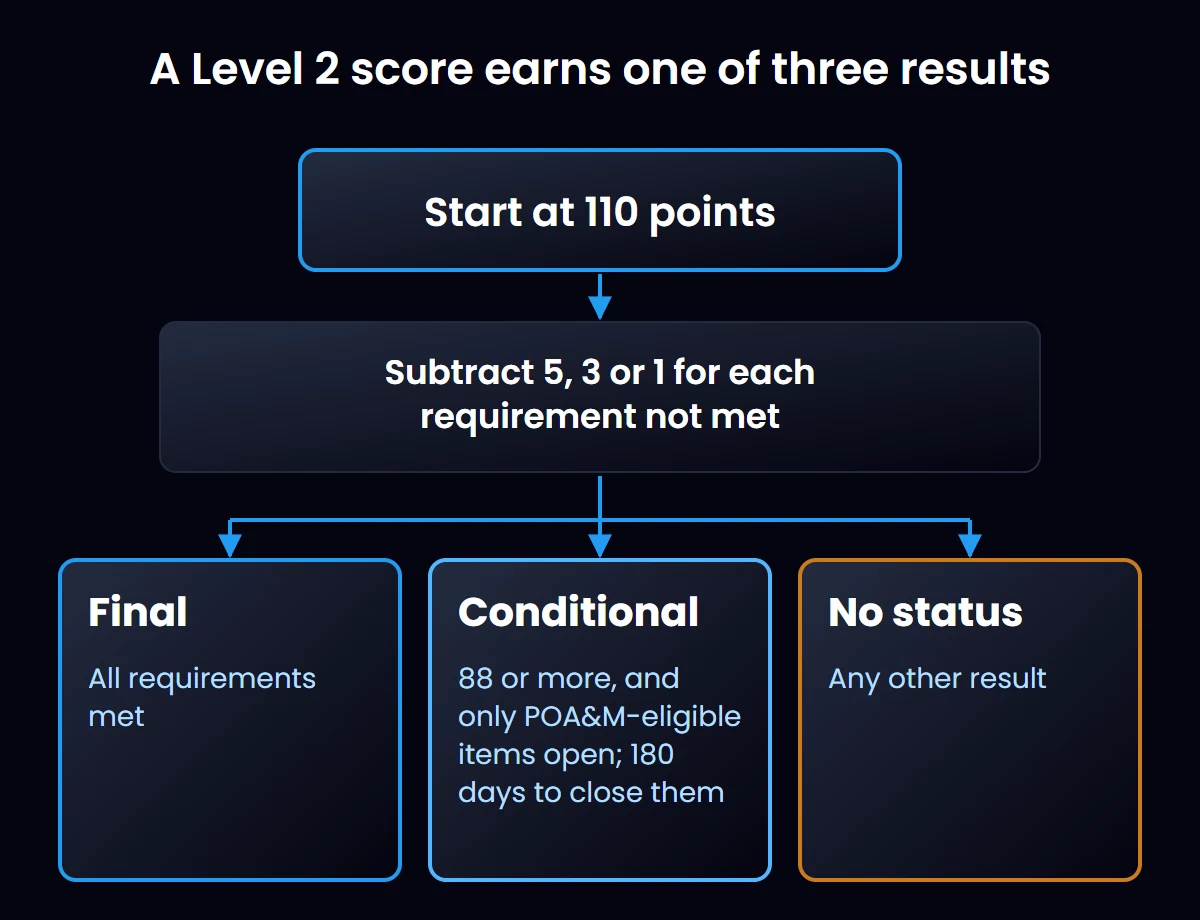
Exceptions have a rule of their own. An enduring exception, where full compliance is not feasible, is MET when the system security plan describes it with its mitigations. So is a temporary deficiency that arose after implementation and is addressed in an operational plan of action that shows deficiency reviews and progress toward the correction.
An adjudication by the DoD CIO, that a requirement is not applicable or that an alternative measure is equally effective, must be in the plan to be considered. A requirement adjudicated as equally effective is MET "if there have been no changes in the environment".
For what happens when the assessor arrives, read the CMMC assessment guide.
Common Challenges of CMMC Certification
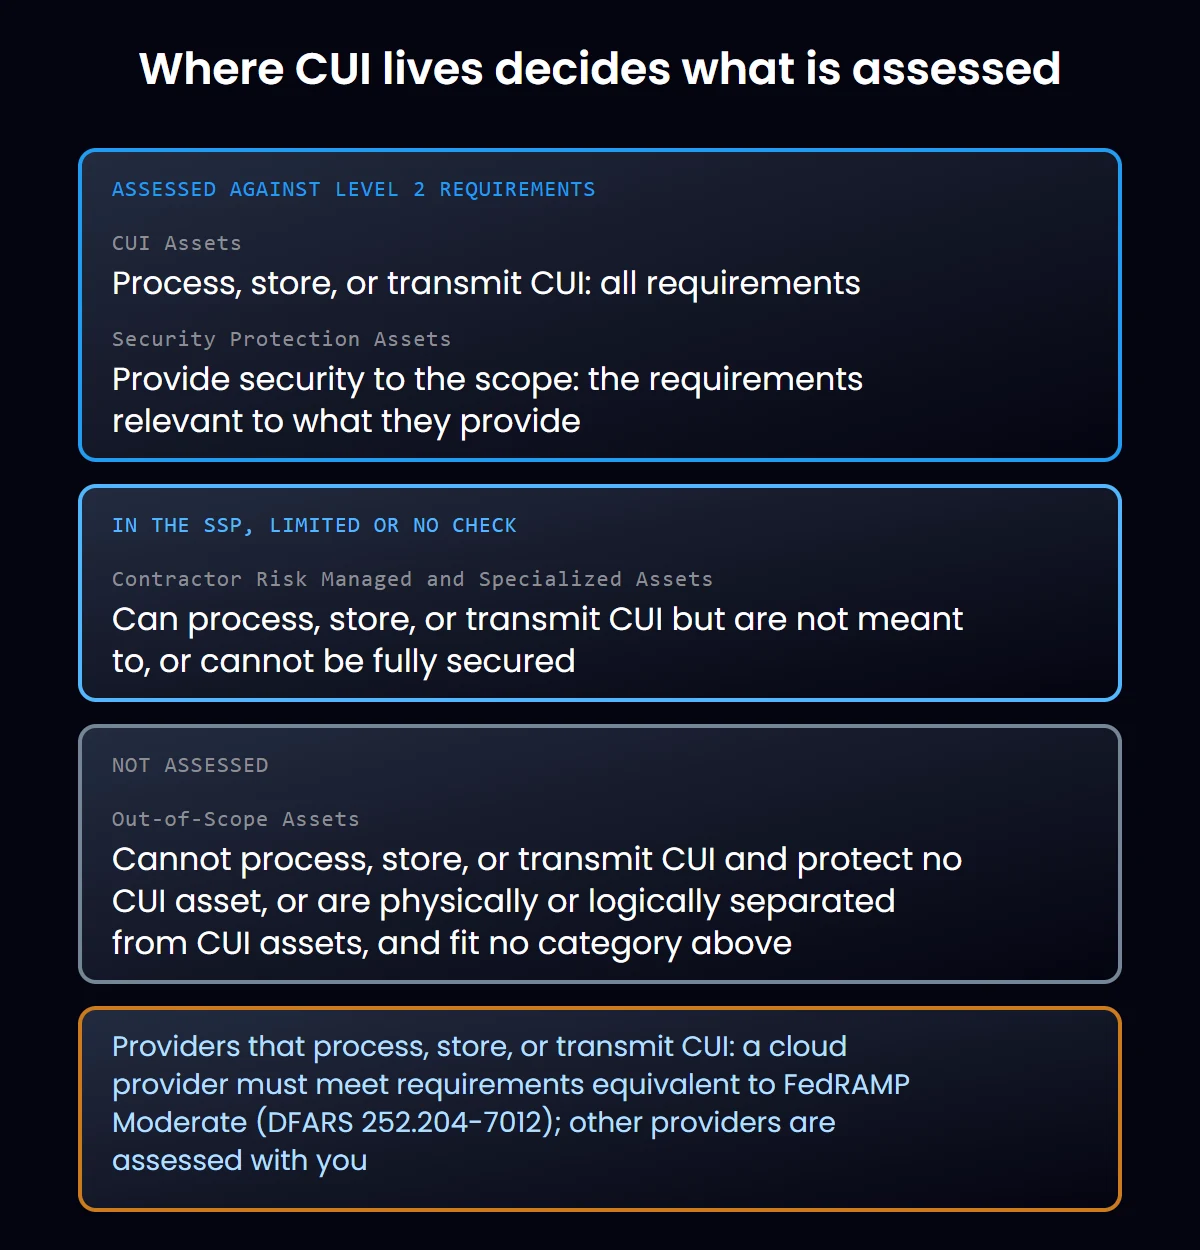
- Fixing where CUI lives: scope, data flows, and providers come before the list. Under 32 CFR 170.4, a provider is an external service provider when CUI or security protection data "must be processed, stored, or transmitted on the ESP assets", and 32 CFR 170.19(c)(2)(ii) has its services and responsibilities documented in your SSP and its customer responsibility matrix. Figure 7, below this list, maps the asset categories of the scope. The CMMC compliance guide covers scoping.
- Documentation that matches the environment: write the plan and procedures from what is configured, not from what was intended. An assessor reads them against configuration settings, logs, and records, so the documents and the systems have to agree.
- Evidence over time: some requirements describe an activity rather than a setting. AU.L2-3.3.5 asks for correlated "audit record review, analysis, and reporting", IR.L2-3.6.3 asks you to "Test the organizational incident response capability", and CA.L2-3.12.3 asks for monitoring "on an ongoing basis". Audit logs kept but not reviewed give an assessor no evidence of the review that AU.L2-3.3.5 asks for.
- What cannot wait for a POA&M: at Level 2 a POA&M may hold only 1-point requirements and SC.L2-3.13.11 at 3 points. The rule bars six by name: AC.L2-3.1.20, AC.L2-3.1.22, CA.L2-3.12.4, and PE.L2-3.10.3 through PE.L2-3.10.5. Level 1 allows none. Check the POA&M column before planning to defer anything.
- Small-team resources: the count is not the workload. All Level 2 requirements are assessed on every asset that handles CUI in the assessment scope, and security protection assets against those relevant to what they provide. A wide scope therefore multiplies the accounts, settings, and records each one touches, and a small IT team carries that beside its daily work. To budget a Level 2 program, read what CMMC certification costs.
- A cloud service used to handle CUI: DFARS 252.204-7012 requires you to ensure that a cloud provider holding covered defense information meets requirements "equivalent to" the FedRAMP Moderate baseline, and 32 CFR 170.19 applies that to a provider in your scope. Ask for that evidence before the data moves.
Common Mistakes When Using a CMMC Controls List
- Counting 17 at Level 1: the number of controls in CMMC Level 1 is 15 under 32 CFR 170.14(c)(2). A tracker built on the December 2021 guide carries 17 rows and IDs the current guide no longer uses; the count chapter above shows where the extra two came from.
- Using domains that are not in the model: the rule maps the CMMC domains to the 14 requirement families of NIST SP 800-171 Rev 2. A list with domains such as Asset Management (AM), Recovery (RE), or Situational Awareness (SA) is not built on those families; compare its headings with Table 1.
- Working from NIST SP 800-171 Rev 3: Rev 3, published in May 2024, organizes its requirements into 17 families. The rule names Rev 2 for Level 2, and the Department of War CIO's FAQ says assessments "will be conducted against Revision 2" until a separate class deviation to DFARS 252.204-7012, which keeps Revision 2, is withdrawn or superseded.
- Treating assessment objectives as controls: a requirement can have several objectives, [a] through [f] for AC.L2-3.1.1 alone. A tracker that gives each objective its own row no longer matches the 110 the rule scores, since a requirement is MET only when all its applicable objectives are satisfied.
Implement Your CMMC Controls with CyberCrest
CyberCrest is a CMMC Registered Practitioner Organization: we advise and prepare, and a formal Level 2 assessment is carried out by an accredited C3PAO. We work through the scope with you, run a gap assessment against the requirements of your level, and support your system security plan and POA&M. Talk to us about CMMC consulting for the list your contract names.
Sources
- Department of Defense, 32 CFR 170.14, CMMC Model. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.14
- Department of Defense Chief Information Officer, CMMC Assessment Guide, Level 1, Version 2.13, September 2024. https://dowcio.war.gov/Portals/0/Documents/CMMC/AssessmentGuideL1v2.pdf
- National Institute of Standards and Technology, SP 800-171 Rev. 2, Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations, February 2020 (updated January 2021). https://csrc.nist.gov/pubs/sp/800/171/r2/upd1/final
- Department of Defense, 32 CFR 170.15, CMMC Level 1 self-assessment and affirmation requirements. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.15
- Department of Defense, 32 CFR 170.16, CMMC Level 2 self-assessment and affirmation requirements. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.16
- Department of Defense, 32 CFR 170.17, CMMC Level 2 certification assessment and affirmation requirements. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.17
- Department of Defense, 32 CFR 170.18, CMMC Level 3 certification assessment and affirmation requirements. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.18
- Department of Defense, 32 CFR 170.21, Plan of Action and Milestones requirements. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.21
- Department of Defense, 32 CFR 170.22, Affirmation. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.22
- Department of Defense Chief Information Officer, CMMC Model Overview, Version 2.0, December 2021. https://dowcio.war.gov/Portals/0/Documents/CMMC/ModelOverview_V2.0_FINAL2_20211202_508.pdf
- Department of Defense, Cybersecurity Maturity Model Certification (CMMC) 2.0 Updates and Way Forward, 86 FR 64100, 17 November 2021. https://www.federalregister.gov/documents/2021/11/17/2021-24880/cybersecurity-maturity-model-certification-cmmc-20-updates-and-way-forward
- Federal Acquisition Regulation, FAR 52.204-21, Basic Safeguarding of Covered Contractor Information Systems. https://www.ecfr.gov/current/title-48/chapter-1/subchapter-H/part-52/subpart-52.2/section-52.204-21
- Department of Defense Chief Information Officer, CMMC Self-Assessment Guide, Level 1, Version 2.0, December 2021. https://dowcio.war.gov/Portals/0/Documents/CMMC/AG_Level1_V2.0_FinalDraft_20211210_508.pdf
- Department of Defense, 32 CFR 170.24, CMMC Scoring Methodology. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.24
- National Institute of Standards and Technology, SP 800-171A, Assessing Security Requirements for Controlled Unclassified Information, June 2018. https://csrc.nist.gov/pubs/sp/800/171/a/final
- Department of Defense Chief Information Officer, CMMC Assessment Guide, Level 2, Version 2.13, September 2024. https://dowcio.war.gov/Portals/0/Documents/CMMC/AssessmentGuideL2v2.pdf
- Department of Defense, 32 CFR 170.19, CMMC scoping. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.19
- Defense Federal Acquisition Regulation Supplement, DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-H/part-252/subpart-252.2/section-252.204-7012
- The White House, Executive Order, Restoring the United States Department of War, 5 September 2025. https://www.whitehouse.gov/presidential-actions/2025/09/restoring-the-united-states-department-of-war/
- Information Security Oversight Office, National Archives and Records Administration, 32 CFR 2002.4, Definitions. https://www.ecfr.gov/current/title-32/subtitle-B/chapter-XX/part-2002/subpart-A/section-2002.4
- Department of Defense, 32 CFR 170.23, Application to subcontractors. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-D/section-170.23
- National Institute of Standards and Technology, SP 800-172, Enhanced Security Requirements for Protecting Controlled Unclassified Information: A Supplement to NIST Special Publication 800-171, February 2021. https://csrc.nist.gov/pubs/sp/800/172/final
- Department of War Chief Information Officer, Cybersecurity Maturity Model Certification Program (CMMC) Frequently Asked Questions, Revision 2.3 (Excerpt), July 2026. https://dowcio.war.gov/Portals/0/Documents/CMMC/FAQsv6.pdf
- Department of Defense, 32 CFR 170.4, Acronyms and definitions. https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170/subpart-A/section-170.4
- National Institute of Standards and Technology, SP 800-171 Rev. 3, Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations, May 2024. https://csrc.nist.gov/pubs/sp/800/171/r3/final
- Department of War Chief Information Officer, Cybersecurity Maturity Model Certification Procedures, Attachment 1 to the memorandum Implementing Suspension of CMMC Phase II, 13 July 2026. https://dowcio.war.gov/Portals/0/Documents/Library/ImplementingSuspensionCMMC-PhaseII.pdf
- Department of War Chief Information Officer, Cybersecurity Maturity Model Certification (CMMC), read 21 October 2026. https://dowcio.war.gov/CMMC/
- Department of War, Forging the Arsenal of Freedom: Department of War Suspends CMMC Phase II Requirements, 13 July 2026. https://www.war.gov/News/Releases/Release/Article/4542329/forging-the-arsenal-of-freedom-department-of-war-suspends-cmmc-phase-ii-require/
- Defense Federal Acquisition Regulation Supplement, DFARS 252.204-7021, Contractor Compliance With the Cybersecurity Maturity Model Certification Level Requirements. https://www.ecfr.gov/current/title-48/chapter-2/subchapter-H/part-252/subpart-252.2/section-252.204-7021
- Department of War, Office of the Assistant Secretary of War for Acquisition and Sustainment, Class Deviation 2026-O0025, Revolutionary FAR Overhaul Part 40, DFARS Part 240, signed 18 December 2025, effective 1 February 2026 (DFARS 240.371-3, Award eligibility). https://www.acquisition.gov/sites/default/files/page_file_uploads/DoD_RFO_Deviation_Part-40.pdf




FAQ
Is CMMC Level 2 still required after the July 2026 suspension?

Yes, where the contract names it. On 13 July 2026 the Department of War suspended CMMC Phase II and said "All Phase I self-assessment requirements remain firmly in place". During the suspension, the Department of War CIO's implementing memo lets new procurement documents name only Level 1 (Self) or Level 2 (Self); a contract that already names Level 2 (C3PAO) or Level 3 (DIBCAC) keeps it until a modification removes it. The Department of War CIO's CMMC page listed no later change on 21 October 2026.
Does CMMC 2.0 replace DFARS 252.204-7012?
No. Where a contract includes DFARS 252.204-7012, the clause applies NIST SP 800-171 to the contractor's own systems that hold covered defense information and requires the contractor to report a cyber incident affecting such a system to DoD within 72 hours of discovery. The CMMC clause, DFARS 252.204-7021, requires a current CMMC status at the contract's level for the life of the contract. The July 2026 suspension notice said "All defense contractors and subcontractors remain contractually obligated" under 7012.
What are NFO controls as they relate to CMMC?
NFO is NIST's mark, in Appendix E of SP 800-171 Rev 2, for SP 800-53 controls "expected to be routinely satisfied by nonfederal organizations without specification". They were tailored out, so they are not among the 110 requirements that CMMC Level 2 copies. NIST notes that such controls "are often included as part of an organization's comprehensive security program".
Do CMMC Level 2 requirements apply to subcontractors?
They do when the subcontractor will process, store, or transmit CUI. 32 CFR 170.23 has the prime contractor require its subcontractors to comply and to flow the requirements down, so they apply at all tiers, and the data in the subcontract sets the level. FCI alone requires Level 1 (Self), and CUI requires at least Level 2 (Self). When the prime contract requires Level 2 (C3PAO) or Level 3 (DIBCAC), a CUI subcontractor needs at least Level 2 (C3PAO).
What are the penalties for non-compliance with CMMC Level 2?
The CMMC clauses tie the consequence to the contract. Under class deviation 2026-O0025, a contracting officer "must not award" a contract to an offeror without a current CMMC status at the level the solicitation requires, and DFARS 252.204-7021 requires that status for the life of the contract. A Conditional status whose POA&M is not closed out within 180 days expires. A senior official affirms compliance in SPRS after each assessment and every year.
About the author

Ron Gupta
—
Senior Director: Governance, Risk and Compliance
Getting his start in tech as an analyst and founder at Via Digital ID, Ron brings to the table a unique approach to cyber security. With over a decade of experience in GRC, Ron has developed and honed a skillset rich in combined audit and assessment as well as risk management and mitigation.
Ron’s ability to convey critical information, results and plans of action to executive leadership is a key skill that allows him to propel the clients he engages with to success. Ron is adept at taking target frameworks, implementing them within environments while reducing overall risk to organizations.