Best SOC 2 Compliance Companies in 2026: Consultants, CPA Firms and Software Platforms
Published on
October 19, 2026

A prospect's security questionnaire or contract clause has just asked your SaaS, fintech, health tech, or managed services company for a SOC 2 report, and the deal date will not wait. Two kinds of firm can help: readiness consultants, which prepare you for the examination, and licensed CPA firms, which examine your controls and issue the report. Software platforms, a third option, automate the evidence work. Some lists of SOC 2 compliance companies mix software, consultants, and auditors without saying who can sign the report. Hire only a consultant, and you still need a CPA firm to issue the report.
This is the CyberCrest blog, so we list ourselves first; we have run over 100 client engagements. For every CPA firm listed, we read the most recent accepted peer review in the AICPA Peer Review Program public file in October 2026 (1).
What Are the Best SOC 2 Compliance Companies?
The nine firms after us, all headquartered in the US, are ordered by how many lists and directories in Google's top 20 for the searches behind this article name them. Firms named equally often are not ranked against each other. The Big Four are not profiled; if a customer names one, ask it the same questions you will find under How to Choose below.
The right firm depends on three things: the report and deadline your customer sets, the other audits you face, and the peer review record of the firm that signs your report (1).
Here is the short answer, with each firm's role:
- CyberCrest (readiness consultant): we run your readiness assessment, guide the remediation, and stay with you through the fieldwork; the report is issued by Cyber Crest CPA Services.
- A-LIGN (licensed CPA firm): SOC 2 alongside ISO 27001, FedRAMP, CMMC, PCI, and HITRUST audits from one provider, with evidence shared across SOC 2, SOC 1, ISO 27001, and HIPAA in its A-SCEND platform.
- Schellman (licensed CPA firm): a SOC audit specialist that issues more than 2,000 SOC reports a year and also runs FedRAMP, CMMC, and PCI DSS assessments.
- BARR Advisory (licensed CPA firm): optional readiness meetings and the SOC 2 examination from the same firm.
- Johanson Group (licensed CPA firm): audits run inside the compliance tools your team already uses.
- Linford & Company (licensed CPA firm): SOC 2 audits make up 90% of its work.
- RSI Security (readiness consultant): advisory and readiness work only, so you choose the CPA firm that issues the report.
- KirkpatrickPrice (licensed CPA firm): PCI DSS and HITRUST CSF assessments alongside SOC 2, from one firm.
- Tevora (readiness consultant): audit support from readiness onward, for organizations whose SOC 2 sits inside a CISO-led security program.
- CBIZ Pivot Point Security (readiness consultant): a month-by-month roadmap to the CPA audit, with a mock audit before the fieldwork.
Types of SOC 2 Compliance Service Providers
Of the three kinds of provider, only a licensed CPA firm can sign your SOC 2 report.
Table 1. Three kinds of SOC 2 provider and what each delivers
| Provider | What it does | What you get | Issues the report? |
|---|---|---|---|
| Readiness consultant | Scopes the report with you, runs a readiness assessment against the trust services criteria in scope, guides remediation and evidence collection | A gap assessment report and a remediation plan | No; a licensed CPA firm does |
| Licensed CPA firm | Examines your controls as the service auditor | The report: management's description, management's written assertion, and the service auditor's opinion (2) (3) | Yes |
| Compliance automation platform | Connects to your systems, collects evidence, and monitors controls | Software, policy templates, and a workspace your auditor can use | No; one platform in this article includes an affiliated CPA firm |
Sources: AICPA, SOC Suite of Services (4), Trust Services Criteria (2) and AT-C section 205 (3); the providers' own pages; read October 2026.
The AICPA Code of Professional Conduct draws the line between running your controls and examining them. A CPA firm that examines you cannot take on your management's responsibilities, such as "accepting responsibility for designing, implementing, or maintaining internal control"; if it did, its independence would be impaired (5). It may still provide other services, as long as your management oversees them and accepts responsibility for the results.
So whichever providers you hire, a SOC 2 engagement can involve three roles. A readiness consultant scopes the work, assesses your readiness, and guides the fixes. Your team and management put the controls in place, keep responsibility for them, and write the system description (5). A licensed CPA firm examines the controls and signs the SOC 2 report (2) (4). Whether you compare the leading consulting firms for SOC 2 readiness or CPA firms that also offer readiness work, ask each to put in writing which tasks it takes on and which stay with your team.
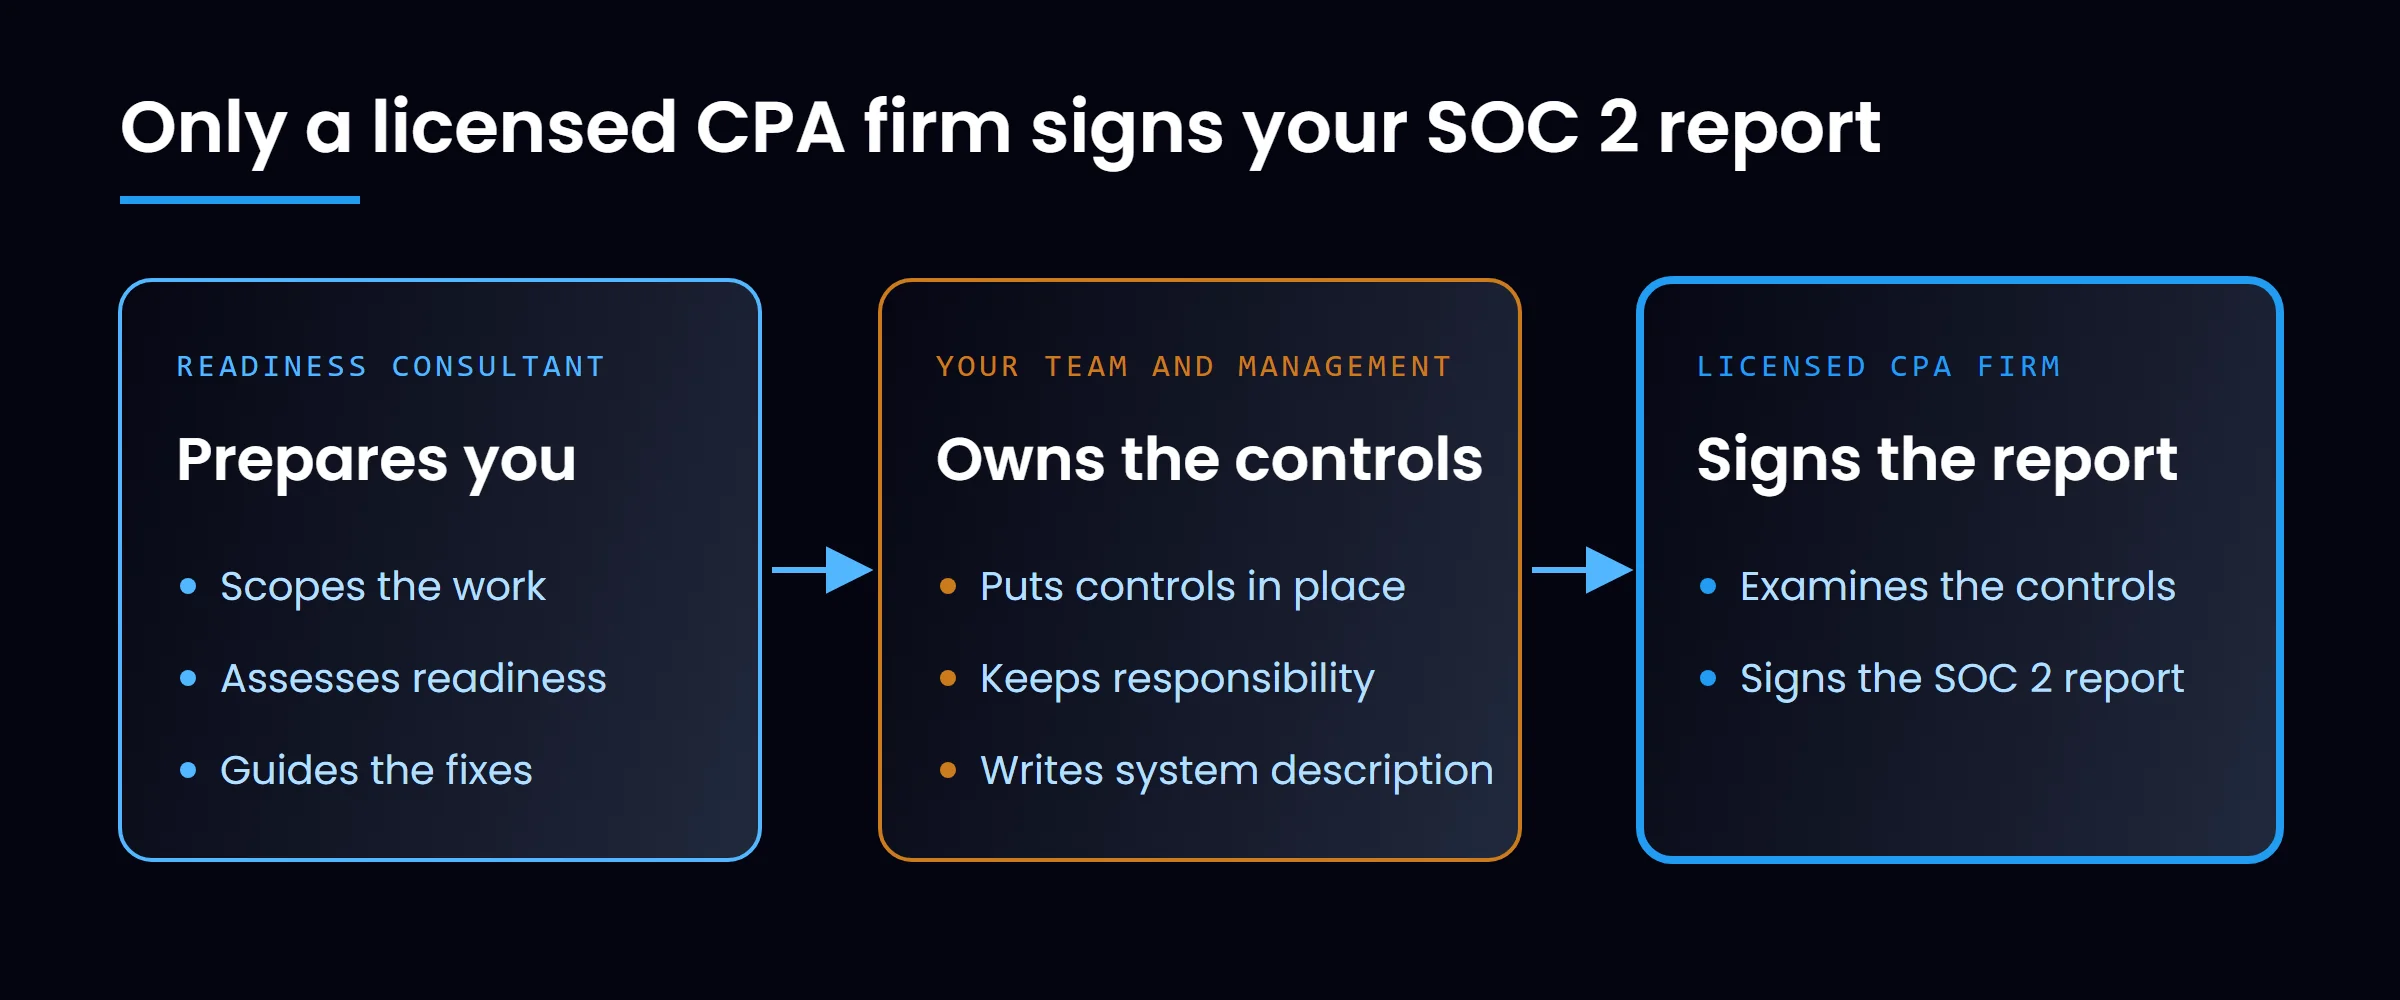
Adapted from: AICPA Code of Professional Conduct, 1.295.030 and 1.295.040 (5); AICPA, SOC Suite of Services (4); AICPA, Trust Services Criteria, TSP section 100 (2).
Whichever provider you hire, every report covers security, through the common criteria (2). Availability, processing integrity, confidentiality, and privacy each add specific criteria of their own. The CPA firm may report on these categories "either individually or in combination", so you add only the categories your customers need beyond security.
Learn more about SOC 2 Type 1 and Type 2
Once the categories are set, the other early choice is the report type. Our SOC 2 Type 1 vs Type 2 comparison puts the two reports side by side and helps you check which one your customer's request calls for.
10 SOC 2 Firms Compared at a Glance
Table 2. Ten SOC 2 firms: role, peer review record, services, pricing, and fit
| Company | Type | AICPA peer review (most recent accepted) | Core services | Pricing | Best for |
|---|---|---|---|---|---|
| CyberCrest | Compliance consultancy | Not applicable: consultancy; report signed by Cyber Crest CPA Services | Readiness and gap assessment, remediation roadmap, review of policies and the system description, evidence register | Priced by scope | Companies with a customer waiting on SOC 2 that want to start right away |
| A-LIGN | CPA firm plus a services entity | Pass, accepted 03/28/2024, for 07/01/2022 to 06/30/2023 | Readiness assessment, Type 1 and Type 2 reports, audits across other frameworks | Fixed fee after a scoping session | Vendors that face SOC 2 alongside ISO 27001, FedRAMP, or other audits and want one provider for all of them |
| Schellman | CPA firm with a nonattest affiliate | Pass, accepted 10/15/2024, for 04/01/2023 to 03/31/2024 | SOC 1, SOC 2, and SOC 3 examinations; FedRAMP, PCI DSS, ISO, and HITRUST assessments | Depends on size, system complexity, and auditor type; no figures | Cloud providers and defense contractors that also need FedRAMP or CMMC |
| BARR Advisory | CPA firm; auditor or consultant | Pass, accepted 06/06/2026, for 09/01/2024 to 08/31/2025 | Readiness meetings, Type 1 and Type 2 examinations, SOC 1, SOC 3, and SOC for Cybersecurity | "Competitive, fixed rates"; no figures | Technology and cloud providers that want readiness meetings and the report from one firm |
| Johanson Group | CPA firm; security and compliance audits | Review accepted 04/30/2025, for 08/01/2023 to 07/31/2024; rating not published in the AICPA public file | Type 1 and Type 2 audits, control testing inside your tools, renewal audits | Not published | SaaS companies that sell to enterprises, already run a compliance platform, and want the audit in it |
| Linford & Company | CPA firm focused on SOC 2 audits | Pass, accepted 12/19/2024, for 06/01/2023 to 05/31/2024 | Scoping consultation, Type 1 and Type 2 audits, recommendations on internal controls | On average, $20,000 to $100,000 | Service organizations that have their readiness covered and want an audit-focused CPA firm with a price range up front |
| RSI Security | Consultancy for advisory and readiness only | Not a CPA firm | Scoping, readiness preparation, evidence preparation, Type 2 lifecycle support | Not published | Organizations that want readiness help and a free choice of CPA firm |
| KirkpatrickPrice | CPA firm, PCI QSA, HITRUST CSF Assessor | Pass, accepted 03/25/2026, for 09/01/2024 to 08/31/2025 | Optional gap analysis, SOC 2 audits, PCI DSS, HITRUST CSF, and ISO 27001 audits | Priced by scope | Companies with PCI DSS or HITRUST obligations that want one auditor for SOC 2 too |
| Tevora | Cybersecurity and compliance consultancy | Not a CPA firm | Readiness assessment, remediation with GRC support, audit support | Estimate by scope, size, and readiness | Security teams led by a CISO that want one consultancy from readiness to the audit |
| CBIZ Pivot Point Security | Information security consultancy, part of CBIZ | Not a CPA firm | Scoping, remediation, mock audit, support during the CPA audit | Not published | Businesses that want consultants to design and implement the controls for them |
Sources: AICPA Peer Review Program public file (1); the firms' own pages; read October 2026. "Not published": the firm gives no price or fee basis.
The ratings follow the AICPA's definitions for System Reviews (6). A pass means the firm's system of quality management "has been suitably designed, implemented, and operated" to give it reasonable assurance of performing and reporting in conformity with professional standards. Johanson Group's entry shows an accepted review with no rating; ask the firm for its peer review report (1).
Top SOC 2 Compliance Consulting Firms and CPA Firms in 2026: Full Breakdown
None of the four consultancies on this list is a CPA firm, so none of them performs the SOC 2 examination; they prepare you for it (4). The six licensed CPA firms examine your controls and sign the report. Each profile gives the legal entity that signs; search that name, not the brand, in the AICPA public file (1). The file is free to search, so recheck the record on the day you sign.
If SOC 2 is one of several audits you face, look for the best security compliance services among firms that also cover your other frameworks, such as ISO 27001 or PCI DSS; each profile lists them. We are a PCI DSS Qualified Security Assessor Company and an Authorized External Assessor Organization for HITRUST.
1. CyberCrest: From Readiness Assessment to Fieldwork
We prepare you and support you through the fieldwork; the report, and the opinion in it, come from Cyber Crest CPA Services. We can begin immediately: a kickoff call sets the objectives, the timeline, and the approach. One of our consultants then sits with your IT team while they implement each fix.
- Type: Compliance consultancy
- Founded: 2021
- HQ: Encinitas, CA
- Serves: Over 100 client engagements across industries, with clients in the US, Canada, Europe, and APAC
- Signs the report as: Cyber Crest CPA Services
- AICPA peer review: Not applicable: we are the consultancy, not the firm that signs the report
- Credentials: PCI DSS Qualified Security Assessor Company; Authorized External Assessor Organization for HITRUST
- Pricing: Priced by scope
- Engagement model: Services bought one at a time or as a single engagement, starting with a walkthrough of your environment
- Other frameworks: ISO 27001, PCI DSS, HITRUST, HIPAA, CMMC, NIST 800-171, NIST CSF, FedRAMP, NIS 2, and GDPR
SOC 2 services
Our SOC 2 compliance services cover the path from scoping to the fieldwork:
- A readiness assessment that maps your existing controls to each criterion in scope
- A gap assessment and a remediation roadmap
- Control and policy guidance, and a review of each policy your team writes, from access provisioning to incident response
- A review of the system description your management writes, against the AICPA description criteria (DC section 200)
- An evidence register and preparation for the service auditor's requests
- Compliance maintenance that keeps evidence collection on track between examinations
Keep in mind
Your team will write policies, put the controls in place, and capture the evidence. That is because the AICPA Code keeps responsibility for your internal control with your management, and the firm that examines you cannot take it on (5). We guide you, specify what each control and document needs, and review your work, so plan for your staff's time.
Best for
Companies whose customer or partner needs a SOC 2 report before it signs or renews, and that want to start right away, with us from the kickoff call to the end of the fieldwork.
2. A-LIGN: Multi-Framework Auditor with the A-SCEND Platform
A-LIGN presents itself as "the world's #1 issuer of SOC 2 reports", with "a process sharpened over 36,000+ audits". Its SOC 2 reports are signed by Price and Associates CPAs, LLC dba A-LIGN, a licensed CPA firm registered with the Public Company Accounting Oversight Board (PCAOB).
- Type: CPA firm plus a services entity
- Founded: 2009, as A-LIGN Compliance and Security, Inc.
- HQ: Tampa, FL
- Serves: More than 6,400 organizations
- Signs the report as: Price and Associates CPAs, LLC dba A-LIGN
- AICPA peer review: Pass, accepted 03/28/2024, for 07/01/2022 to 06/30/2023 (1)
- Credentials: PCAOB-registered CPA firm; accredited FedRAMP 3PAO; CMMC C3PAO; PCI QSA company; accredited ISO certification body; HITRUST CSF assessor firm
- Pricing: Fixed fee after a scoping session
- Engagement model: One provider for readiness, the SOC 2 audit, and other frameworks
- Typical timeline: A Type 2 period of 3 to 12 months
- Audit platform: A-SCEND
- Other frameworks: ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST
SOC 2 services
- A readiness assessment that "evaluates your controls against the standard before the audit begins"
- Type 1 reports at a point in time, and Type 2 reports over "typically a 3 to 12 month period"
Keep in mind
The services other than the SOC reports come from a second entity, A-LIGN Compliance and Security, Inc., so check which entity a proposal names for each part of the work.
Best for
Vendors that face SOC 2 alongside other audits, such as ISO 27001 or FedRAMP, and want one provider for all of them.
3. Schellman: SOC Audit Firm with FedRAMP and CMMC Assessments
Schellman began as a SOC audit firm more than 20 years ago and still issues more than 2,000 SOC reports a year. Two entities share the brand. Schellman & Company, LLC is the licensed CPA firm that signs the report. Schellman Compliance, LLC provides nonattest services and is not a licensed CPA firm.
- Type: CPA firm with a nonattest affiliate
- Founded: 2002
- HQ: Tampa, FL
- Serves: Not published
- Signs the report as: Schellman & Company, LLC
- AICPA peer review: Pass, accepted 10/15/2024, for 04/01/2023 to 03/31/2024 (1)
- Credentials: PCAOB-registered CPA firm; accredited FedRAMP 3PAO; CMMC C3PAO, presented as "one of the first C3PAOs cleared by the CMMC Accreditation Body"; QSA and PA-QSA for P2PE
- Pricing: Depends on size, system complexity, and auditor type; no figures
- Engagement model: An optional readiness assessment, then the examination
- Typical timeline: A Type 2 period of 6 months or more
- Audit platform: Not published
- Other frameworks: FedRAMP, CMMC, PCI DSS, ISO certifications, and HITRUST
SOC 2 services
- SOC 1, SOC 2, and SOC 3 examinations
- Point-in-time Type 1 reports, and Type 2 reports over "typically six months or more"
Keep in mind
The readiness assessment only evaluates your controls: the assessor "does not provide advisory, remediation, or implementation services". The fixes stay with your team or a consultant.
Best for
Cloud service providers that need a FedRAMP assessment, and defense contractors that need a CMMC assessment, alongside SOC 2.
4. BARR Advisory: Auditor or Consultant from One CPA Firm
BARR Advisory is a licensed CPA firm that offers to work as "an external auditor, internal auditor, or an expert consultant".
- Type: CPA firm
- Founded: Not published
- HQ: Fairway, KS
- Serves: Clients in 20+ countries
- Signs the report as: BARR Advisory, P.A.
- AICPA peer review: Pass, accepted 06/06/2026, for 09/01/2024 to 08/31/2025 (1)
- Credentials: Licensed CPA firm
- Pricing: "Competitive, fixed rates"; no figures
- Engagement model: Readiness meetings before the examination, if you want them
- Typical timeline: An engagement cycle of 3 to 12 months
- Audit platform: Not published
- Other frameworks: ISO 27001, HITRUST, PCI DSS, and CMMC, plus SOC 1, SOC 3, and SOC for Cybersecurity
SOC 2 services
- An optional readiness period with a series of readiness meetings before the examination
- Engagement cycles of 3 to 12 months for Type 1 and Type 2 reports, with the Type 2 "often issued annually"
- Examinations for SOC 1, SOC 3, and SOC for Cybersecurity
Keep in mind
If BARR both advises and examines you, your management keeps responsibility for the controls, so agree in writing who owns each one (5).
Best for
Technology and cloud service providers that want readiness meetings and the examination from the same CPA firm.
5. Johanson Group: Audits Inside the Tools You Already Use
Johanson Group is a CPA firm that audits security and compliance programs.
- Type: CPA firm; security and compliance audits
- Founded: 2012
- HQ: Colorado Springs, CO
- Serves: Clients in the US, Latin America, Europe, and APAC
- Signs the report as: Johanson Group LLP
- AICPA peer review: Review accepted 04/30/2025, for 08/01/2023 to 07/31/2024; rating not published in the AICPA public file (1)
- Credentials: Active Colorado accountancy firm license
- Pricing: Not published
- Engagement model: A dedicated Customer Success Manager from scoping through annual renewal
- Typical timeline: Type 1 in 8 to 12 weeks; a Type 2 period of 6 to 12 months, plus 6 to 8 weeks of fieldwork and reporting
- Audit platform: Audits inside your existing tools
- Other frameworks: ISO 27001, ISO 27017/18, ISO 42001, HIPAA, GDPR, PCI DSS, and NIST
SOC 2 services
- SOC 2 Type 1 and Type 2 audits
- Walkthroughs, evidence inspection, and control testing
- Your sign-off on the draft report before it is finalized
- Renewal audits planned before the prior period lapses
Keep in mind
Before a first SOC 2, Johanson strongly recommends a readiness assessment, but it is not among the services above, so ask who will run it before you engage the firm.
Best for
Software and SaaS vendors that sell to enterprise buyers and already run a compliance platform.
6. Linford & Company: A CPA Firm Focused on SOC 2 Audits
Linford & Company is a Denver CPA firm, and SOC 2 audits make up 90% of its work.
- Type: CPA firm
- Founded: Not published; Colorado firm license first issued in 2008
- HQ: Denver, CO
- Serves: Small businesses to Fortune 500 companies
- Signs the report as: Linford & Company LLP
- AICPA peer review: Pass, accepted 12/19/2024, for 06/01/2023 to 05/31/2024 (1)
- Credentials: Active Colorado accountancy firm license
- Pricing: On average, $20,000 to $100,000
- Engagement model: Partner involvement in each audit
- Typical timeline: Usually a 12-month Type 2 period
- Audit platform: Not published
- Other frameworks: SOC 1, HITRUST, HIPAA, and FedRAMP
SOC 2 services
- Two audit types, Type 1 and Type 2, with a Type 2 covering "usually a period of 12 months"
- A consultation with management to settle which trust services criteria are in scope
- An engagement fee estimate and a timeline once the scope is clear, with a to-do list and a risk and controls matrix
- Onsite or virtual interviews, then the report and recommendations on processes and internal controls
Keep in mind
Linford's services include no readiness assessment, so plan the preparation with your own team or a consultant.
Best for
Service organizations that have their readiness work covered and want an auditor with a published price range.
7. RSI Security: Advisory and Readiness Without the Examination
RSI Security provides SOC 2 advisory and readiness services to clients in healthcare, defense, finance, SaaS, and the public sector.
- Type: Readiness consultancy
- Founded: 2013
- HQ: Southlake, TX
- Serves: Over 1,000 organizations
- Signs the report as: A licensed CPA firm you choose
- AICPA peer review: Not a CPA firm
- Credentials: Authorized CMMC C3PAO in the Cyber AB Marketplace, listed as RSI Systems, Inc.
- Pricing: Not published
- Engagement model: Five steps, from discovery to ongoing support
- Typical timeline: A Type 2 period of at least 6 months
- Audit platform: Not published
- Other frameworks: NIST CSF, the HIPAA Security Rule, PCI DSS, ISO/IEC 27001, and CMMC
SOC 2 services
RSI's readiness work, including evidence organization and audit preparation support, runs in five steps:
- Initial understanding and discovery: business services, customer commitments, and data handling practices
- Clarification of scope: "in-scope systems, data flows, and applicable Trust Services Criteria"
- Structured readiness preparation, with policies, procedures, and technical controls evaluated against SOC 2 expectations
- Readiness review and evidence preparation: gaps identified, documentation improved, and audit-ready evidence organized
- Ongoing lifecycle support for Type 2 reporting and later audit cycles
Keep in mind
The examination is a second engagement, with a CPA firm you select and contract separately.
Best for
Organizations in healthcare, finance, SaaS, or the public sector that want readiness help and their own choice of CPA firm.
8. KirkpatrickPrice: SOC 2 with PCI DSS and HITRUST Assessments
KirkpatrickPrice is a licensed CPA firm that runs SOC 2 audits alongside PCI DSS, HITRUST, and ISO 27001 assessments, with locations across the US from Atlanta to Seattle.
- Type: CPA firm
- Founded: Not published
- HQ: Nashville, TN
- Serves: Over 2,000 clients worldwide
- Signs the report as: Kirkpatrick Price Inc.
- AICPA peer review: Pass, accepted 03/25/2026, for 09/01/2024 to 08/31/2025 (1)
- Credentials: Licensed CPA firm, PCI QSA, and HITRUST CSF Assessor
- Pricing: Priced by scope
- Engagement model: A dedicated specialist from audit readiness to the final report
- Typical timeline: Weeks to months, depending on preparedness and staff availability
- Audit platform: Online Audit Manager
- Other frameworks: SOC 1, HIPAA, HITRUST CSF, PCI DSS, GDPR, ISO 27001, and FISMA
SOC 2 services
A KirkpatrickPrice SOC 2 audit typically includes:
- A gap analysis, if you choose one, and scoping exercises
- An onsite visit and an evidence gathering period
- The SOC 2 report
Keep in mind
Remediation time can be added to a KirkpatrickPrice engagement, so ask what it covers and which work stays with your team.
Best for
Teams with PCI DSS or HITRUST obligations that want SOC 2 from the same auditor.
9. Tevora: SOC 2 Consulting for the CISO's Security Program
Tevora is a cybersecurity and compliance consultancy focused on supporting a client's Chief Information Security Officer.
- Type: Cybersecurity and compliance consultancy
- Founded: 2003
- HQ: Irvine, CA
- Serves: SaaS, fintech, and cloud-first organizations
- Signs the report as: A licensed CPA firm, name not disclosed
- AICPA peer review: Not a CPA firm
- Credentials: Authorized CMMC C3PAO; FedRAMP 3PAO
- Pricing: Estimate by scope, size, and readiness
- Engagement model: Three stages: readiness assessment, remediation, and support through the attestation
- Typical timeline: A Type 2 period of 6 to 12 months
- Audit platform: Not published
- Other frameworks: CMMC, FedRAMP, HITRUST, HIPAA, the ISO series including ISO 42001, and PCI
SOC 2 services
- A readiness assessment that sets the scope of the attestation and compares your current state with the desired one
- Remediation, with supplemental GRC support where controls still have to be put in place
- Audit support through the attestation
- Work on compliance maturity "year after year" once the first report is out
Keep in mind
Ask who will sign your report before you hire Tevora, because Tevora does not name the CPA firm that issues its clients' reports.
Best for
Security teams led by a CISO that want one consultancy from the readiness assessment to the audit.
10. CBIZ Pivot Point Security: A Month-by-Month Roadmap to the CPA Audit
CBIZ Pivot Point Security offers SOC 2 consulting and has been part of CBIZ, Inc. since an acquisition effective June 1, 2023.
On July 29, 2026, Grant Thornton Advisors announced an agreement to acquire CBIZ, with closing expected in the fourth quarter of 2026. The deal still needs shareholder and regulatory approvals. If your engagement will run into that quarter or later, ask Pivot Point who will deliver it.
- Type: Information security consultancy, part of CBIZ
- Founded: 2001
- HQ: Hamilton, NJ
- Serves: More than 1,000 companies across North America, Europe, and APAC
- Signs the report as: A licensed CPA firm, name not disclosed
- AICPA peer review: Not a CPA firm
- Credentials: Not published
- Pricing: Not published
- Engagement model: A four-phase roadmap from scoping to the CPA audit, then annual renewal support
- Typical timeline: Type 1 in 3 to 4 months; Type 2 in 6 to 12 months
- Audit platform: Not published
- Other frameworks: ISO 27001 and CMMC, mapped from the SOC 2 controls
SOC 2 services
Pivot Point's roadmap to a first report has four phases:
- Scope and align (month 1): the trust services criteria that match your business, chosen to prevent over-scoping.
- Build and remediate (months 2 to 4): Pivot Point designs and implements the technical controls and policies that close the gaps.
- Validate (month 5): a readiness assessment (mock audit) before the CPA audit.
- Attest (month 6 onward): support during the CPA audit.
After the first report, annual renewal support covers the Type 2 observation period and evidence collection.
Keep in mind
A licensed CPA firm, not Pivot Point, performs the SOC 2 examination, so the audit is a second engagement to arrange.
Best for
Businesses that want consultants to design and implement the controls for them and to run a mock audit before the CPA firm arrives.
SOC 2 Compliance Software Platforms
A compliance automation platform collects evidence and monitors controls, and the report is still signed by a licensed CPA firm (4).
Table 3. Six SOC 2 platforms and how each works with an auditor
| Platform | What it automates | Issues the report? | Works with your auditor or brings one |
|---|---|---|---|
| Drata | Evidence collection mapped to SOC 2 controls; continuous control tests | No | Your auditor, in a separate audit workspace |
| Secureframe | Monitoring of 150+ cloud services; policies, training, vendor risk | No | Your auditor, through evidence collection and fieldwork workflows |
| Sprinto | Evidence from 300+ systems; continuous monitoring | No | Your existing auditor, or a vetted directory of independent audit partners |
| Thoropass | Scope, evidence, requests, and reviews in one audit workspace | Its CPA firm does: Laika Compliance, LLC dba Thoropass Assurance | Brings its own in-house auditors |
| Scrut | Prebuilt controls, hundreds of prebuilt tests, automated evidence | No | External SOC 2 assessors you invite work inside the platform |
| Strike Graph | Tailored controls, automated evidence collection, owners for each risk and control | No | Your existing auditor, or a vetted independent auditor from its partner network |
Sources: each platform's SOC 2 page; AICPA Peer Review Program public file (1) for Laika Compliance LLC; read October 2026.
A platform alone can be enough when your team can scope the work, close the gaps, and write the policies. Sprinto and Scrut add some guidance inside the tool, and Thoropass brings its own auditors. A consultant adds the judgment around the tool: the scope, a readiness or gap assessment, and a roadmap that orders the fixes.
Drata
Drata connects directly to the systems you already run, from cloud infrastructure and identity providers to code repositories and ticketing tools, and maps the evidence it collects to SOC 2 controls. It "continuously tests your SOC 2 controls" across the five trust services categories instead of checking them once a year. Its audit workspace holds the mapped evidence, control status, and change logs in one place.
Secureframe
Secureframe monitors "150+ cloud services including AWS, Google Cloud, and Azure" through read-only access, without agents. Secureframe's in-house security experts and former auditors developed and vetted its policy library, and the platform also runs employee onboarding checks and vendor risk assessments. For the audit it offers "auditor evidence collection workflows and fieldwork processes", and a common control layer carries the controls you have completed for SOC 2 over to additional frameworks.
Sprinto
Sprinto connects to more than 300 systems, from cloud providers to identity and code tools, and pulls the evidence auditors require automatically. It assigns "a certified onboarding manager" who reviews your setup and flags what needs fixing before the audit. A company with no auditor yet can pick one from its directory of audit partners.
Thoropass
Thoropass is the exception among the six: its audits are performed by Laika Compliance, LLC dba Thoropass Assurance, a licensed CPA firm. Its Audit Lifecycle Platform keeps the whole audit, from scope to reviews, in one workspace. You can meet your dedicated auditor before the audit begins and later reuse controls and evidence for frameworks such as ISO 27001 and HITRUST. In the AICPA public file, Laika Compliance LLC's most recent accepted peer review is a pass, accepted 12/12/2025 (1).
Scrut
Scrut prepares companies for SOC 2 Type 1 and Type 2 "with prebuilt controls and automated evidence gathering". Hundreds of prebuilt tests look for gaps against SOC 2 controls, and the platform monitors those controls continuously while it pulls evidence from your integrated tools. For the audit, you can "invite internal auditors and external SOC 2 assessors to review evidence", with role-based access that shows auditors only what they need. Scrut's in-house SOC 2 experts guide control implementation and help fix control gaps.
Strike Graph
Strike Graph tailors the control set so that you spend effort only on the SOC 2 controls "that are necessary for your business". Its platform automates evidence collection and maintenance reminders and assigns each risk, control, and piece of evidence to an owner on your team. Strike Graph also includes 55+ policy templates and support for other frameworks.
How to Choose a SOC 2 Auditor or Consultant
Start from your customer's requirement in writing: the report type, the trust services categories, and the deadline. Then choose a CPA firm by the legal entity that will sign and its record, and a consultant by the work it will and will not do. Put the same questions to each of the best SOC 2 compliance assessment experts on your shortlist.
Questions to Ask Before You Sign
- "Does our customer need a Type 1 or a Type 2?" A Type 1 covers the description and the control design; a Type 2 adds the controls' operating effectiveness throughout a specified period (2).
- "Which systems, locations, and data flows are in scope?" Scope drives the fee at A-LIGN, Linford & Company, and KirkpatrickPrice, so get a fixed scope in writing.
- "Under which legal entity's name is the report signed?" The brand on a proposal and the name on the report can differ, as the A-LIGN and Thoropass entries above show (1).
- "What does that entity's record in the AICPA public file show?" The entry gives the period, the acceptance date, and, where published, the rating of the most recently accepted peer review (1). For any rating other than pass, or no rating, ask for the peer review report.
- "Is the firm licensed by the state board of accountancy?" The AICPA will take action where auditors have "not been enrolled in peer review, and/or are unlicensed", and it refers unlicensed firms to state boards of accountancy (4).
- "Who will do the work, and what stays with our team?" Ask for names and roles, and for who writes the policies; the CPA firm that examines you needs your management to own the controls (5).
- "Are readiness and the examination priced separately?" Separate prices let you compare like with like.
- "From kickoff to the signed report, how long does SOC 2 take with you?" Published figures cover different spans, as Figure 2 below shows, so ask for one that ends at the report.
- "How much will next year's report cost?" A Type 2 report covers a specified period, so the next report needs an observation window and an examination of its own (2).
- "Where will the evidence sit?" Johanson Group audits inside your own tools; A-LIGN uses its A-SCEND platform and KirkpatrickPrice its Online Audit Manager. Ask which one will hold the evidence for security controls such as access reviews.
Red Flags When Choosing a SOC 2 Compliance Company
- A "SOC 2 certificate." The AICPA defines a SOC 2 engagement as an examination that reports on management's description and your controls, not a certificate (2).
- A guaranteed pass or a guaranteed date. The opinion depends on how your controls perform; the AICPA's Journal of Accountancy warns that "Promises of 'fast and easy' threaten SOC credibility" (4).
- One entity offering to take responsibility for your controls and then sign the report. Under the AICPA Code, that would impair the signing firm's independence (5).
- A checklist that bills each point of focus. Points of focus are characteristics the Trust Services Criteria list under each criterion to help apply it, and some may not fit your company (2). Using the criteria "does not require an assessment of whether each point of focus is addressed".
SOC 2 Compliance Timeline and Cost
A first SOC 2 report starts with readiness and fixes. Then comes the report your customer asks for: a Type 1, on the controls at one date, or a Type 2 (2). A Type 2 runs an observation period, then the fieldwork and the report. A-LIGN puts that period at typically 3 to 12 months, and most other firms on this list at 6 to 12 months or more.
Five of the nine firms here with a published figure give only the Type 2 period. They are A-LIGN, Schellman, Linford & Company, RSI Security, and Tevora. So ask each firm for the time from kickoff to the signed report.
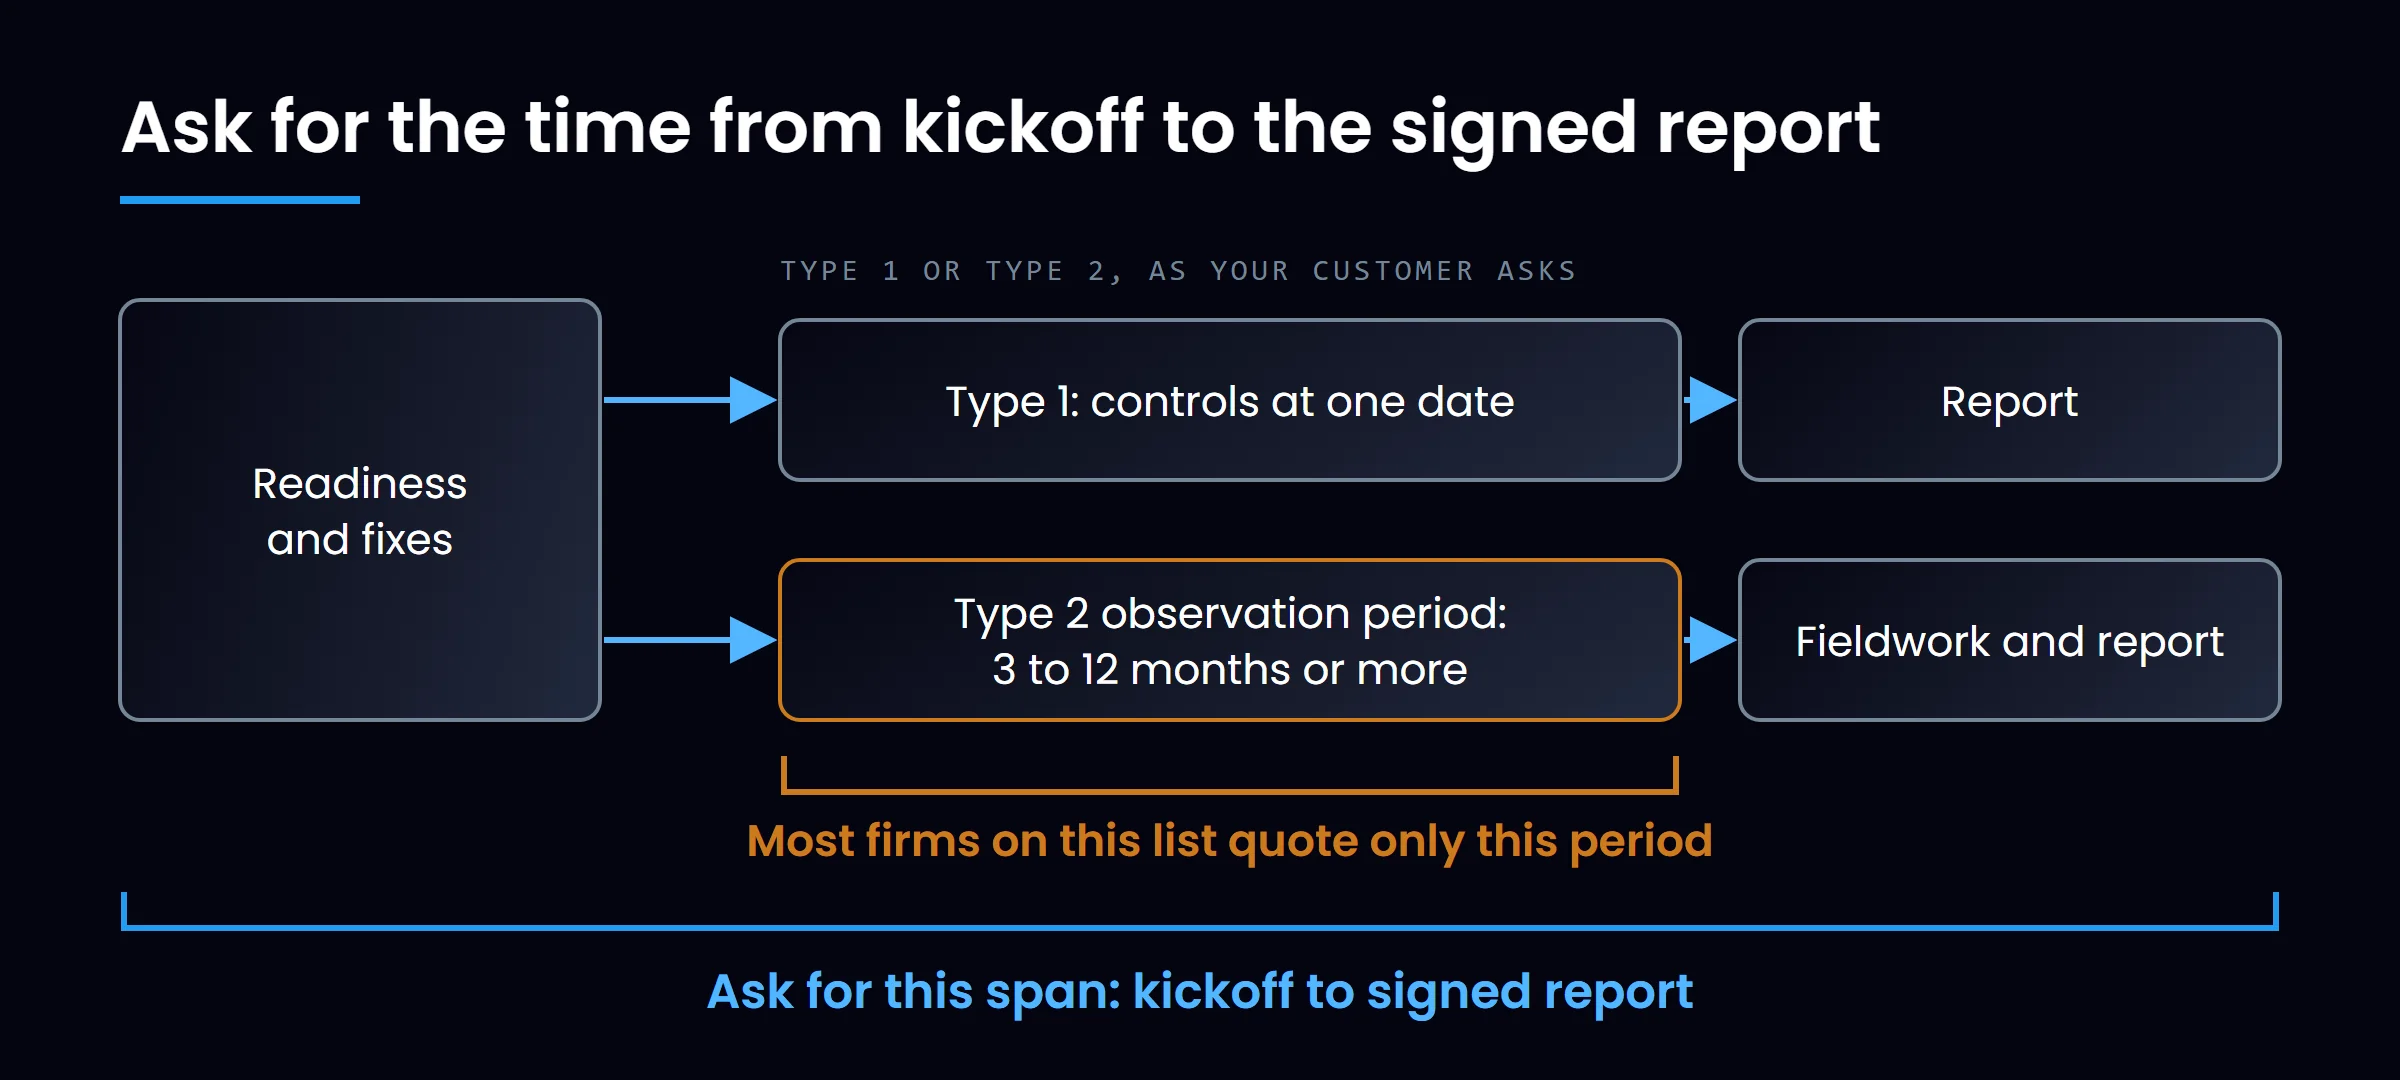
Adapted from: the firms' own SOC 2 pages.
Cost follows scope. Linford & Company is the only firm on this list that publishes a range: a SOC 2 audit costs "on average, $20,000 to $100,000". A-LIGN, Linford & Company, and KirkpatrickPrice name these drivers:
- The trust services criteria in scope beyond security
- The systems, applications, locations, and third parties or subservice organizations inside the boundary
- The report type: a Type 2 requires more testing than a Type 1
- The readiness work, gap analysis, or remediation time the engagement includes
Learn more about SOC 2 costs
For a closer look at each of these drivers, our SOC 2 cost guide separates direct fees from indirect expenses, explains why a Type 2 can cost more than a Type 1, and covers annual maintenance and continuous improvement.
Conclusion
A first SOC 2 report needs preparation and an examination, and only a licensed CPA firm can issue it, whether your consultant names the firm or you choose one yourself. If your team can do the readiness work itself, a compliance platform and a CPA firm may be enough. If it cannot, a consultant scopes the work, finds the gaps, and puts the fixes in order.
Before you sign, get your customer's requirement in writing and search the signing entity's legal name in the AICPA public file. Once you have the report, keep each control producing evidence through the next period, because the next report covers that period, not the day of the audit (2).
Prepare for Your SOC 2 Examination with CyberCrest
We run your readiness assessment against each criterion in scope and give you a remediation roadmap that puts the fixes in the order they have to happen. While your team closes the gaps, we review the policies it writes and your management's system description against the criteria, then prepare your team for the fieldwork and stay with you until it ends. If a customer has asked you for a SOC 2 report, book a call and we can begin immediately.
Sources
- AICPA, Peer Review Program public file search. https://peerreview.aicpa.org/public_file_search.html
- AICPA, 2017 Trust Services Criteria (With Revised Points of Focus, 2022), TSP section 100. https://assets.ctfassets.net/rb9cdnjh59cm/72xv4p67HVXKp6CjWmjkPk/1cdbfa19f6307e2720396b66a6194dc9/trust-services-criteria-updated-copyright.pdf
- AICPA, AT-C section 205, Assertion-Based Examination Engagements. https://assets.ctfassets.net/rb9cdnjh59cm/49M1391nsNvsSx6gou3EKW/d0e0475caf4596239d342b35acfabe4d/at-c-sections-100-300.pdf
- AICPA & CIMA, System and Organization Controls: SOC Suite of Services. https://www.aicpa-cima.com/resources/landing/system-and-organization-controls-soc-suite-of-services
- AICPA, Code of Professional Conduct, 1.295.030 Management Responsibilities and 1.295.040 General Requirements for Performing Nonattest Services. https://pub.aicpa.org/codeofconduct/ethicsresources/et-cod.pdf
- AICPA, Peer Review Program FAQs. https://assets.ctfassets.net/rb9cdnjh59cm/76TEZGSn6C9DFvjn4U3RqW/9c19e4e9dd5aff4d60432dace14a7bba/peer-review-program-faqs.pdf




FAQ
Who needs SOC 2 compliance?

No law requires a SOC 2 report; a customer asks for it, in a security questionnaire, a procurement checklist, or a contract clause, before trusting a provider with customer data. SaaS and cloud providers, fintech platforms serving banks, health tech vendors, and managed service providers are asked most often. Our guide to SOC 2 reports explains what one contains.
How long does it take to get SOC 2 compliance?
Plan for about 3 to 4 months for a Type 1 and 6 to 12 months for a Type 2, the figures CBIZ Pivot Point Security gives for the whole process. Some firms quote only the Type 2 observation period, which A-LIGN puts at "typically a 3 to 12 month period", so ask each firm for the time from kickoff to the signed report; your readiness moves it most. Our step-by-step guide to SOC 2 attestation walks through each stage.
What is a SOC 2 audit and who performs it?
What buyers call a SOC 2 audit is a SOC 2 examination of a service organization's controls under the AICPA's attestation standards, reporting on management's description of its system, the design of its controls and, in a Type 2, their operating effectiveness (2). A licensed CPA firm performs it (4).
How much does SOC 2 compliance cost?
Published prices are rare: Linford & Company gives "on average, $20,000 to $100,000" for a SOC 2 audit, depending on scope and other factors. A-LIGN offers "transparent, fixed-fee pricing after the scoping session", and KirkpatrickPrice prices by scoping factors such as applications and locations. Ask for readiness work and the examination as separate lines before you compare quotes.
How do companies prepare for a SOC 2 audit?
Preparation starts with scope: the report type and the trust services categories your customers need. The common criteria, which cover security, are in every report (2). A readiness assessment compares your current controls with those criteria, and a roadmap orders the fixes. Your team puts each control in place and sets up its evidence, and management writes the system description before the fieldwork. Some firms add a mock audit. If this will be your first report, our SOC 2 roadmap for startups walks through the work before the examination.
How do buyers verify vendor SOC 2 compliance?
They ask for the report itself rather than a certificate: management's description and written assertion, and the service auditor's opinion on the controls (2) (3). Then they check the report type and period, and whether the categories they rely on are in scope. An experienced reviewer reads the opinion next. A qualified or adverse opinion, or a disclaimer, is a modified opinion, and the report explains the matter behind it in a separate paragraph (3).
What documentation supports SOC 2 readiness?
A SOC 2 examination rests on two documents from management, the system description it writes and the assertion it signs (3). The description covers the services, the service commitments and system requirements, the system's components, and the controls. Behind them sit your policies and procedures and the evidence each control leaves over time.
About the author
Ron Gupta
—
Senior Director: Governance, Risk and Compliance
Getting his start in tech as an analyst and founder at Via Digital ID, Ron brings to the table a unique approach to cyber security. With over a decade of experience in GRC, Ron has developed and honed a skillset rich in combined audit and assessment as well as risk management and mitigation.
Ron’s ability to convey critical information, results and plans of action to executive leadership is a key skill that allows him to propel the clients he engages with to success. Ron is adept at taking target frameworks, implementing them within environments while reducing overall risk to organizations.